
In today’s fast-paced cloud environments, risks and threats evolve by the minute, and teams closest to the code and infrastructure need the ability to understand their security posture, but also the flexibility of taking ownership of how to prioritize and remediate any given risk.
In order to do so, security professionals need a way to customize how risk is calculated and managed: examining findings, recasting their severity, accepting or dismissing issues, tagging other teams for review, or snoozing them for another day. Without this, security findings is just just a list of problems.
That’s why we’re excited to introduce a new set of capabilities to Modify, Accept, Recast, and Snooze Risks directly within the Upwind platform. This release represents a broader shift we’re driving at Upwind: open source security.
This release introduces a new model for distributed risk control, one that emphasizes ownership, customization, and transparency across the organization. It’s inspired by the principles of open source security: systems that evolve through shared input, accountability, and iteration.
From Centralized Control to Custom Ownership
Modern security operations are overloaded with findings, but not all issues carry equal weight. Some are accepted risks, some are mitigated in progress, and others simply reflect theoretical exposure.
Upwind’s new model allows teams to adapt their workflows to how they actually operate. Findings can be snoozed, recast, or accepted with justification, keeping dashboards focused on what’s actionable. This approach ensures that every decision is backed by context from runtime intelligence.
By enabling customizable workflows, Upwind empowers every team to take responsibility for their part of the security lifecycle, without losing alignment or visibility at the organizational level.
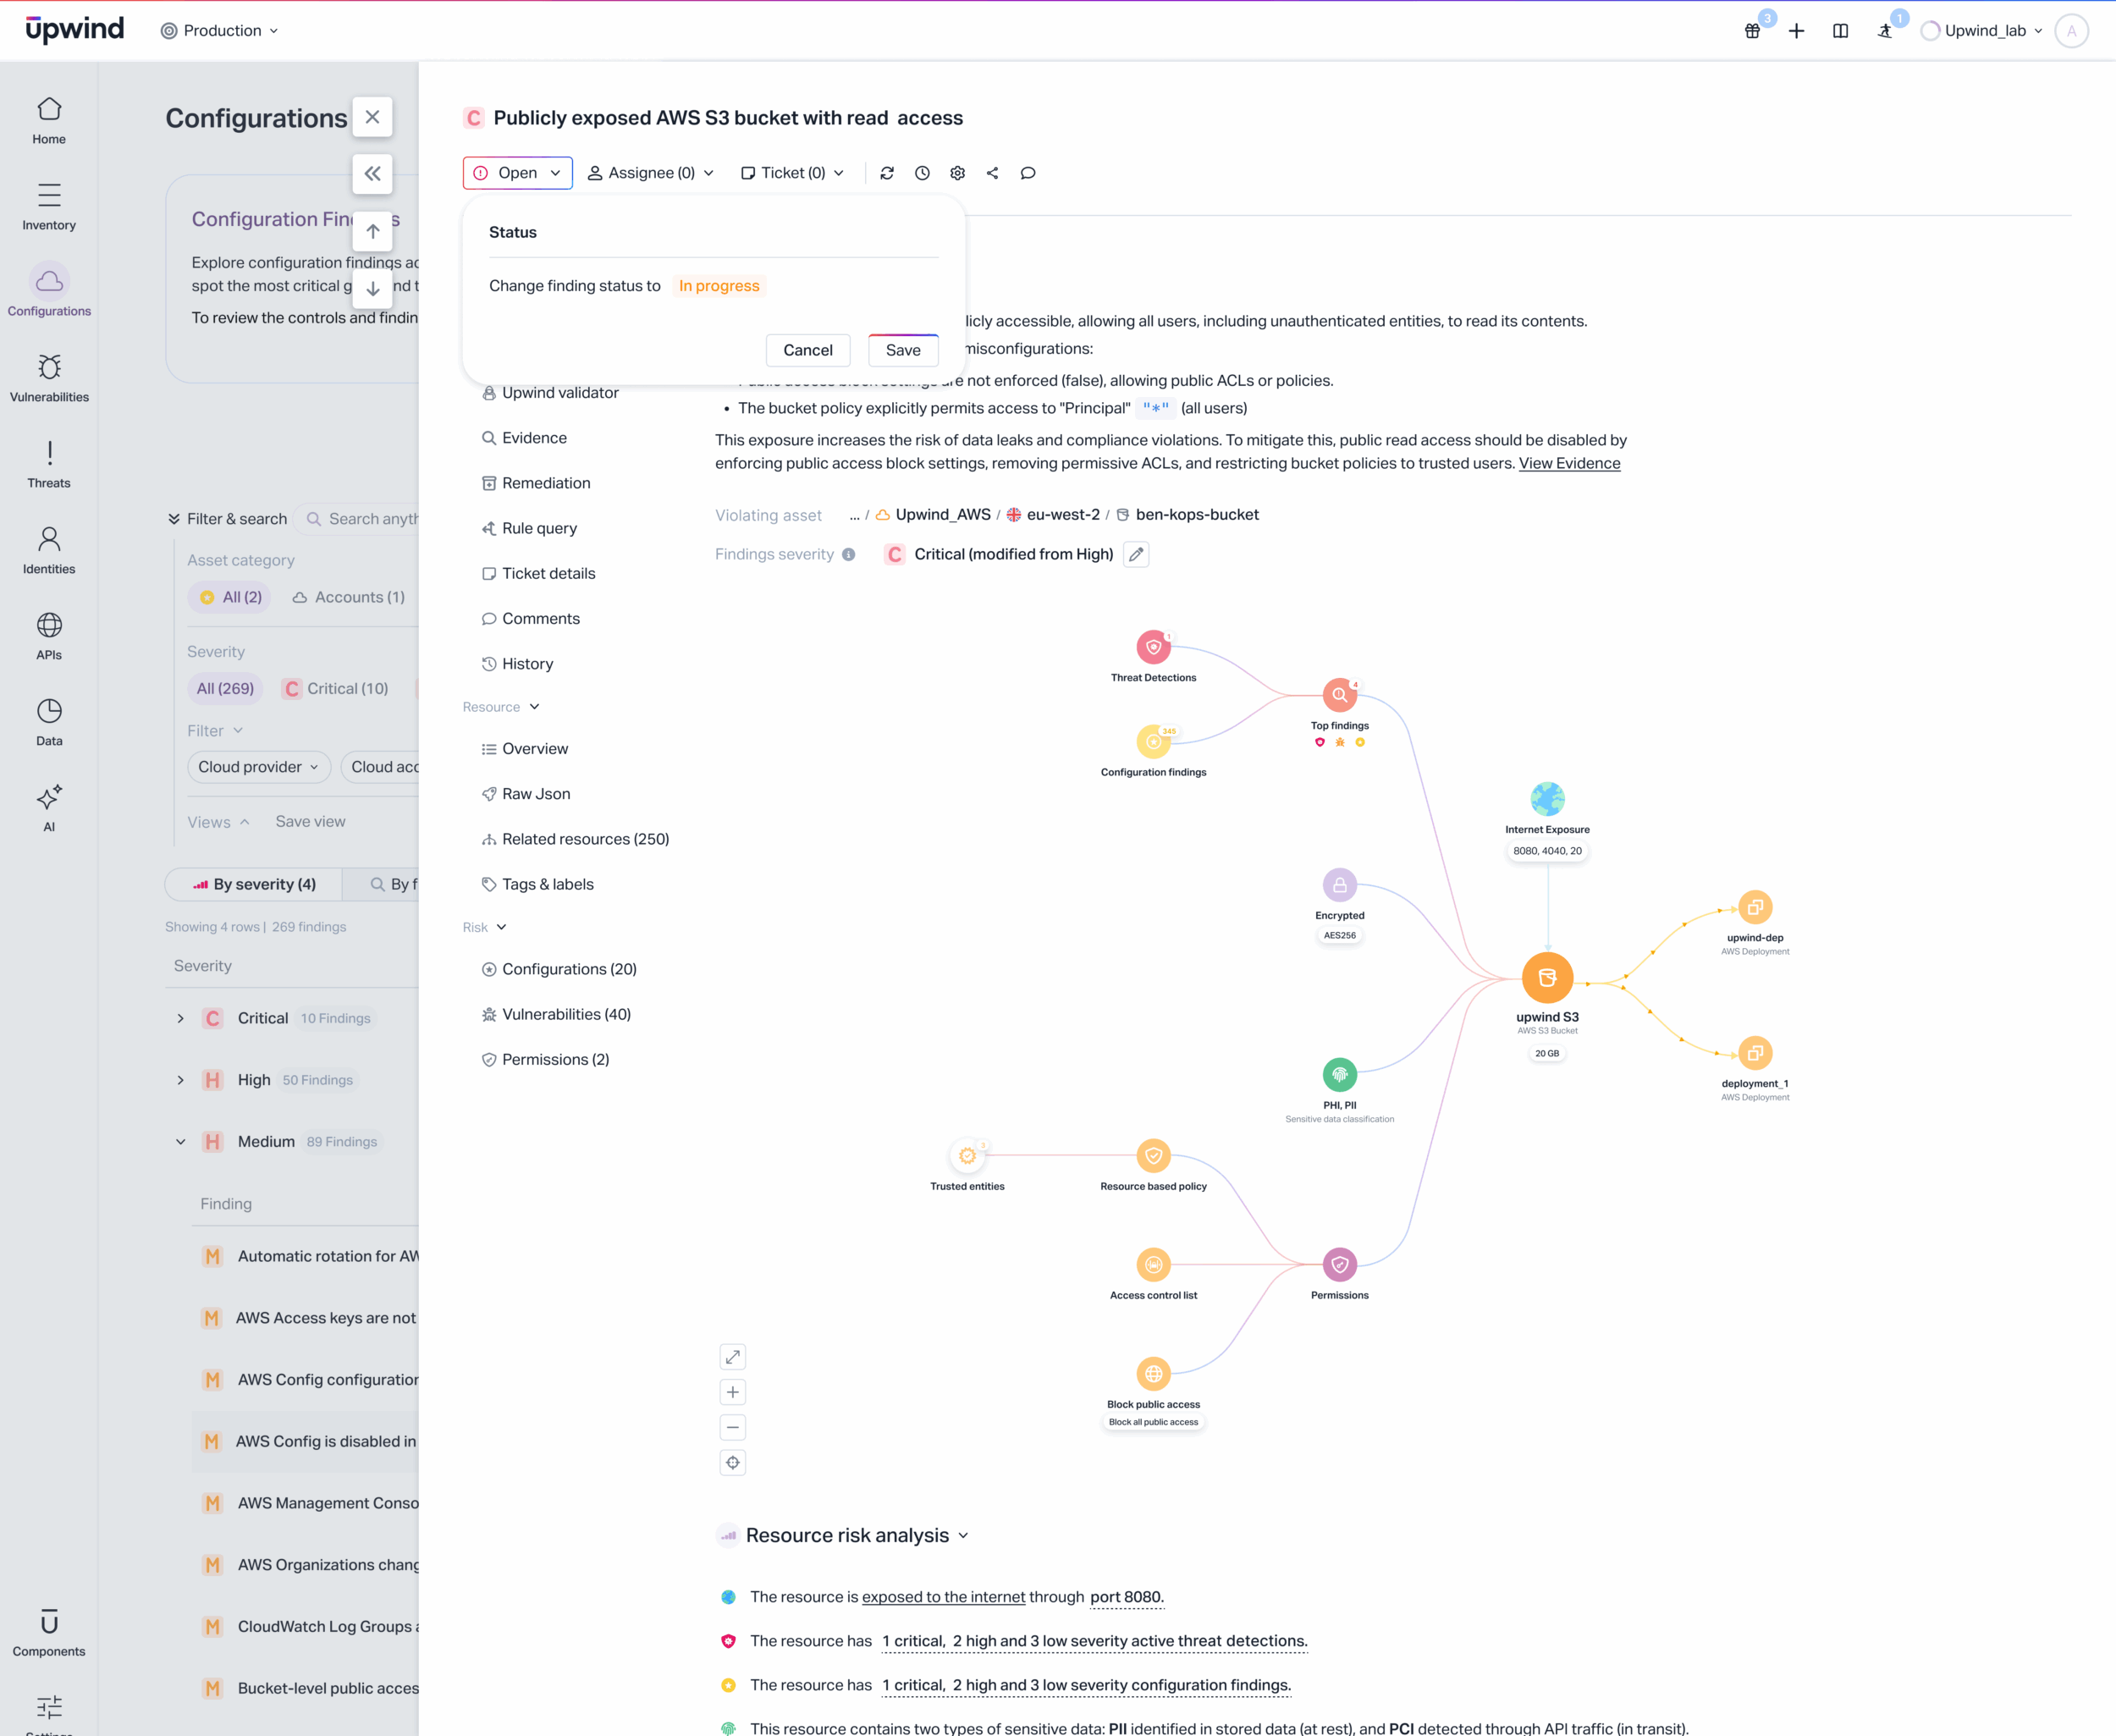
Turning Findings into Custom Workflows
Upwind’s new model decentralizes control over security findings while keeping alignment intact. This model encourages collaboration and ownership, giving developers, analysts, and security leads the ability to act, contribute, and improve.
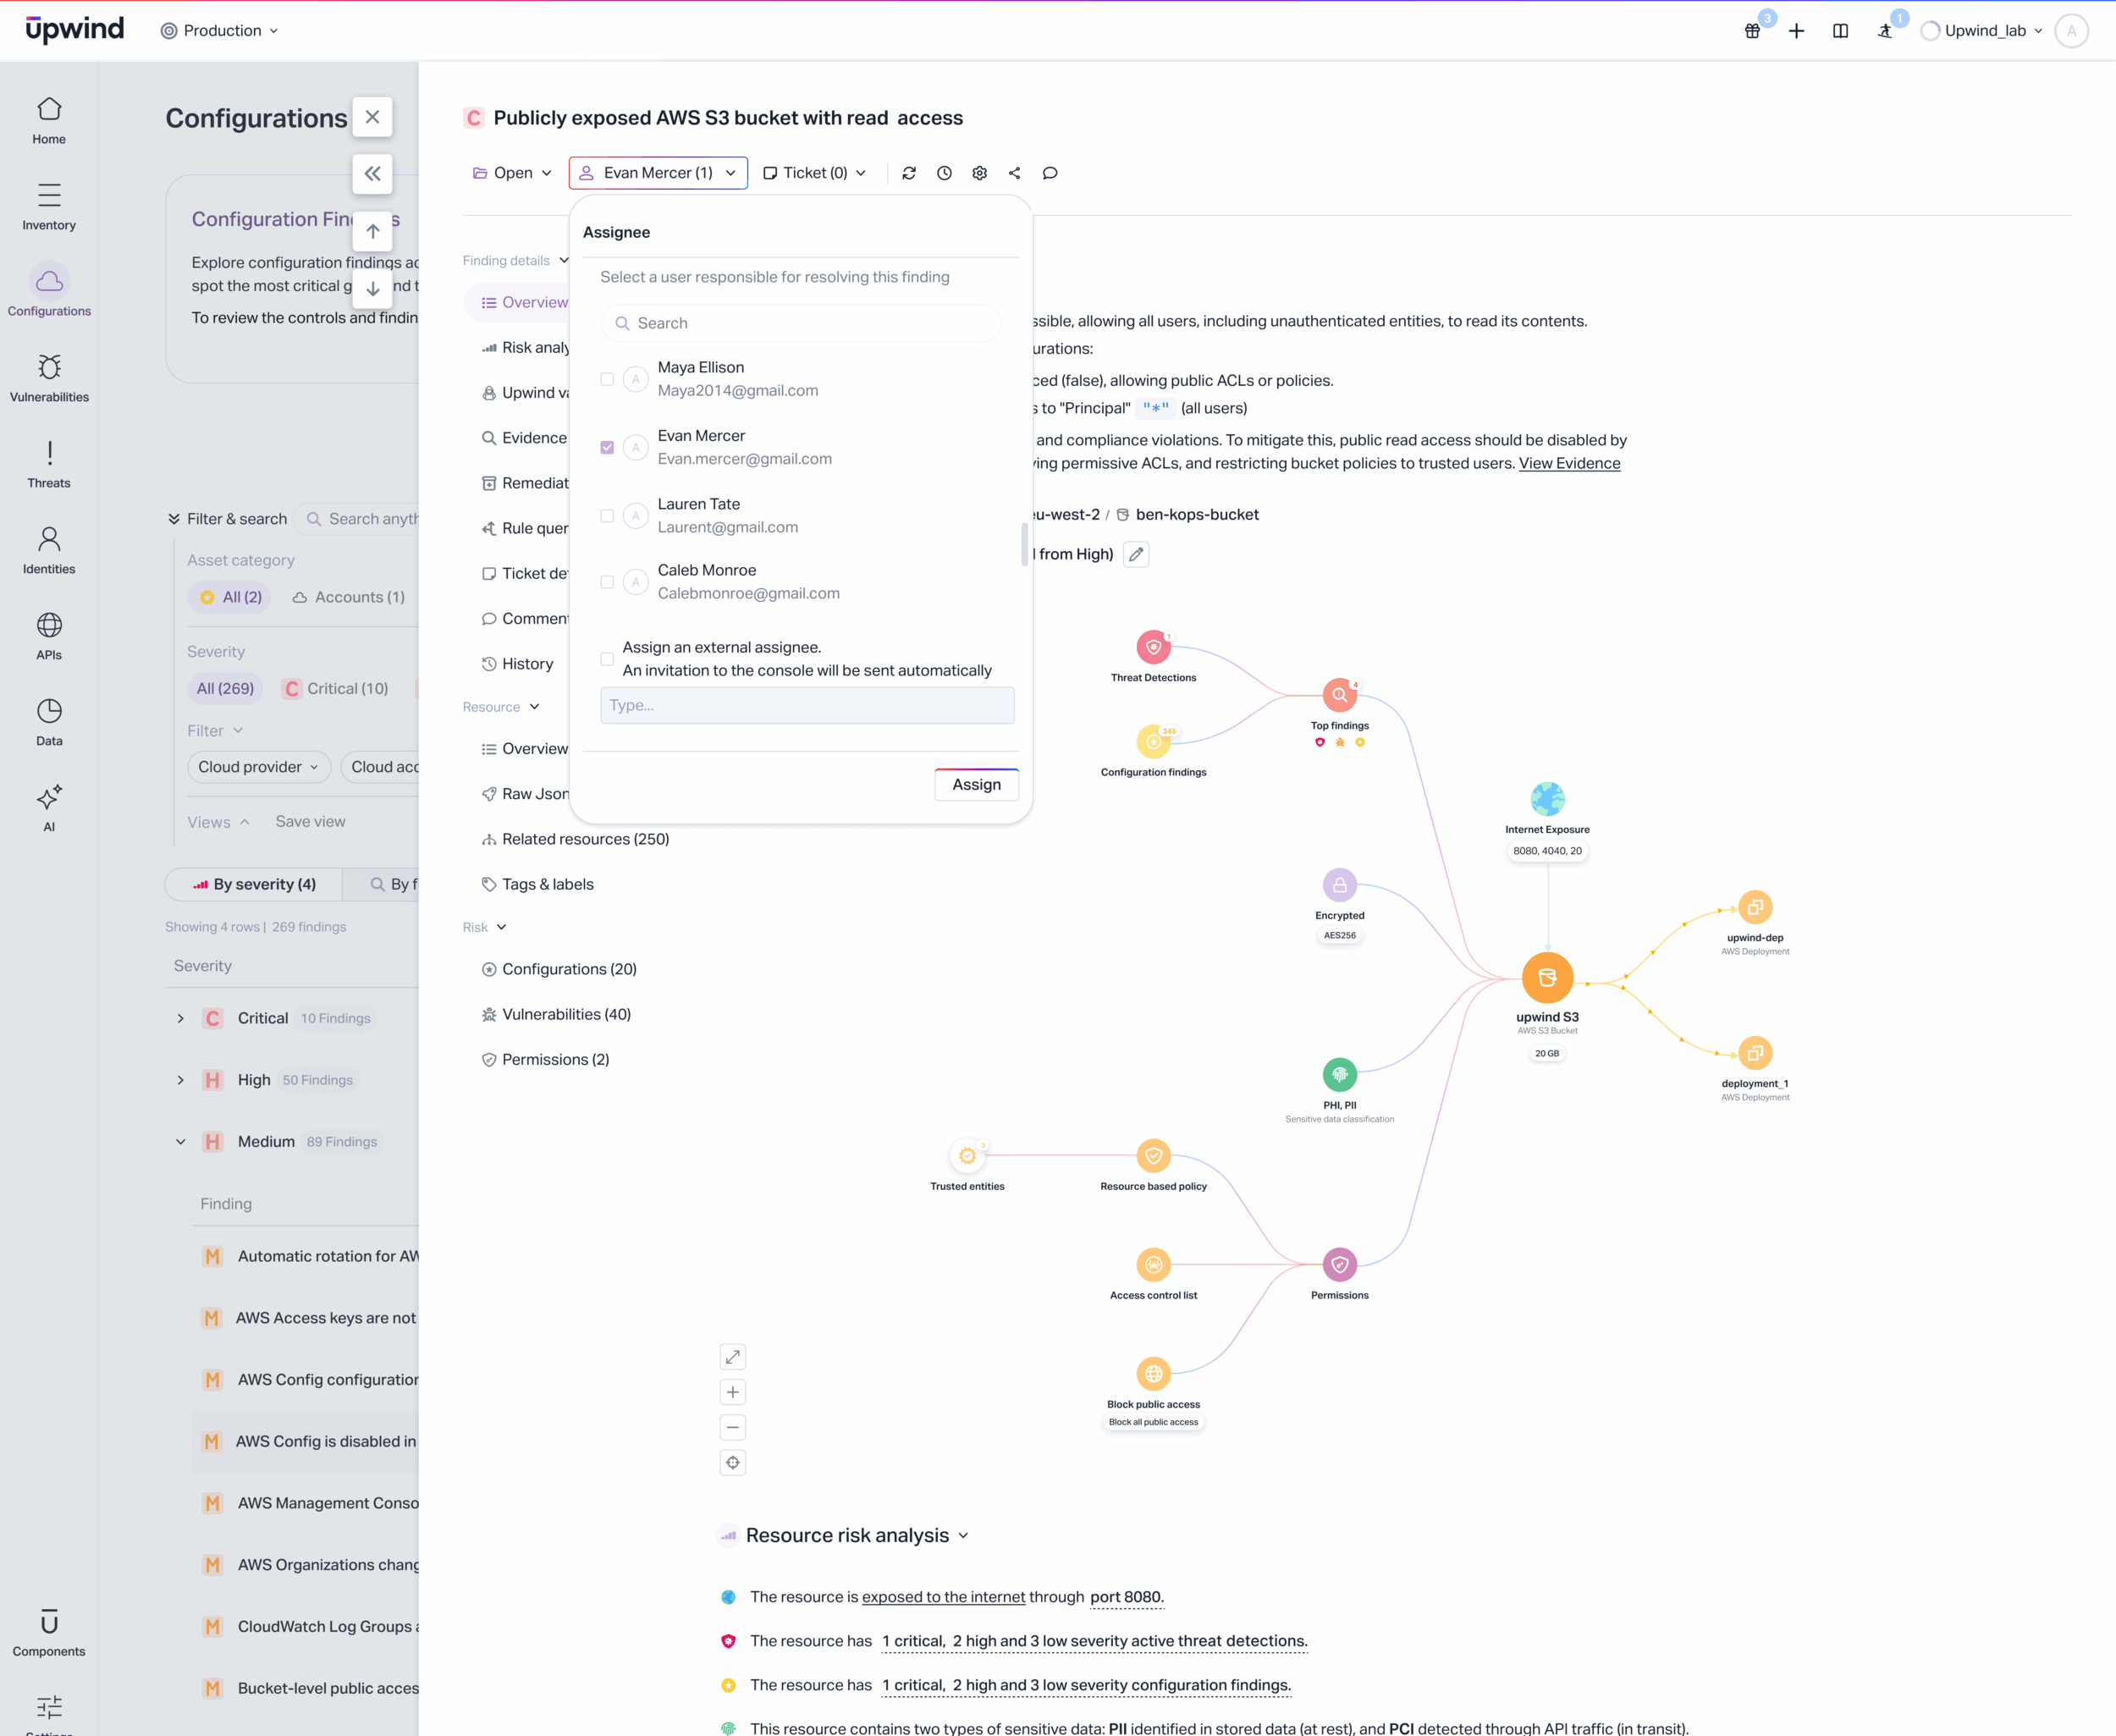
This model reflects how modern security and engineering teams operate: not in isolation, but as partners in managing risk.
Key benefits include:
- Operational Flexibility: Teams can snooze findings that are in progress, under review, or accepted without deleting or losing traceability.
- Adaptive Prioritization: Modify severity levels to reflect real business impact, ensuring the most critical issues rise to the top.
- Clear Accountability: Every change, from recast to acceptance, is logged with who, why, and when, creating a transparent record of decisions.
- Shared Understanding: Standardized reasons and actions align Security, DevOps, and Compliance teams, keeping everyone on the same page.
The result of this streamlined workflow is a more manageable way to handle findings; one that mirrors how teams actually work.
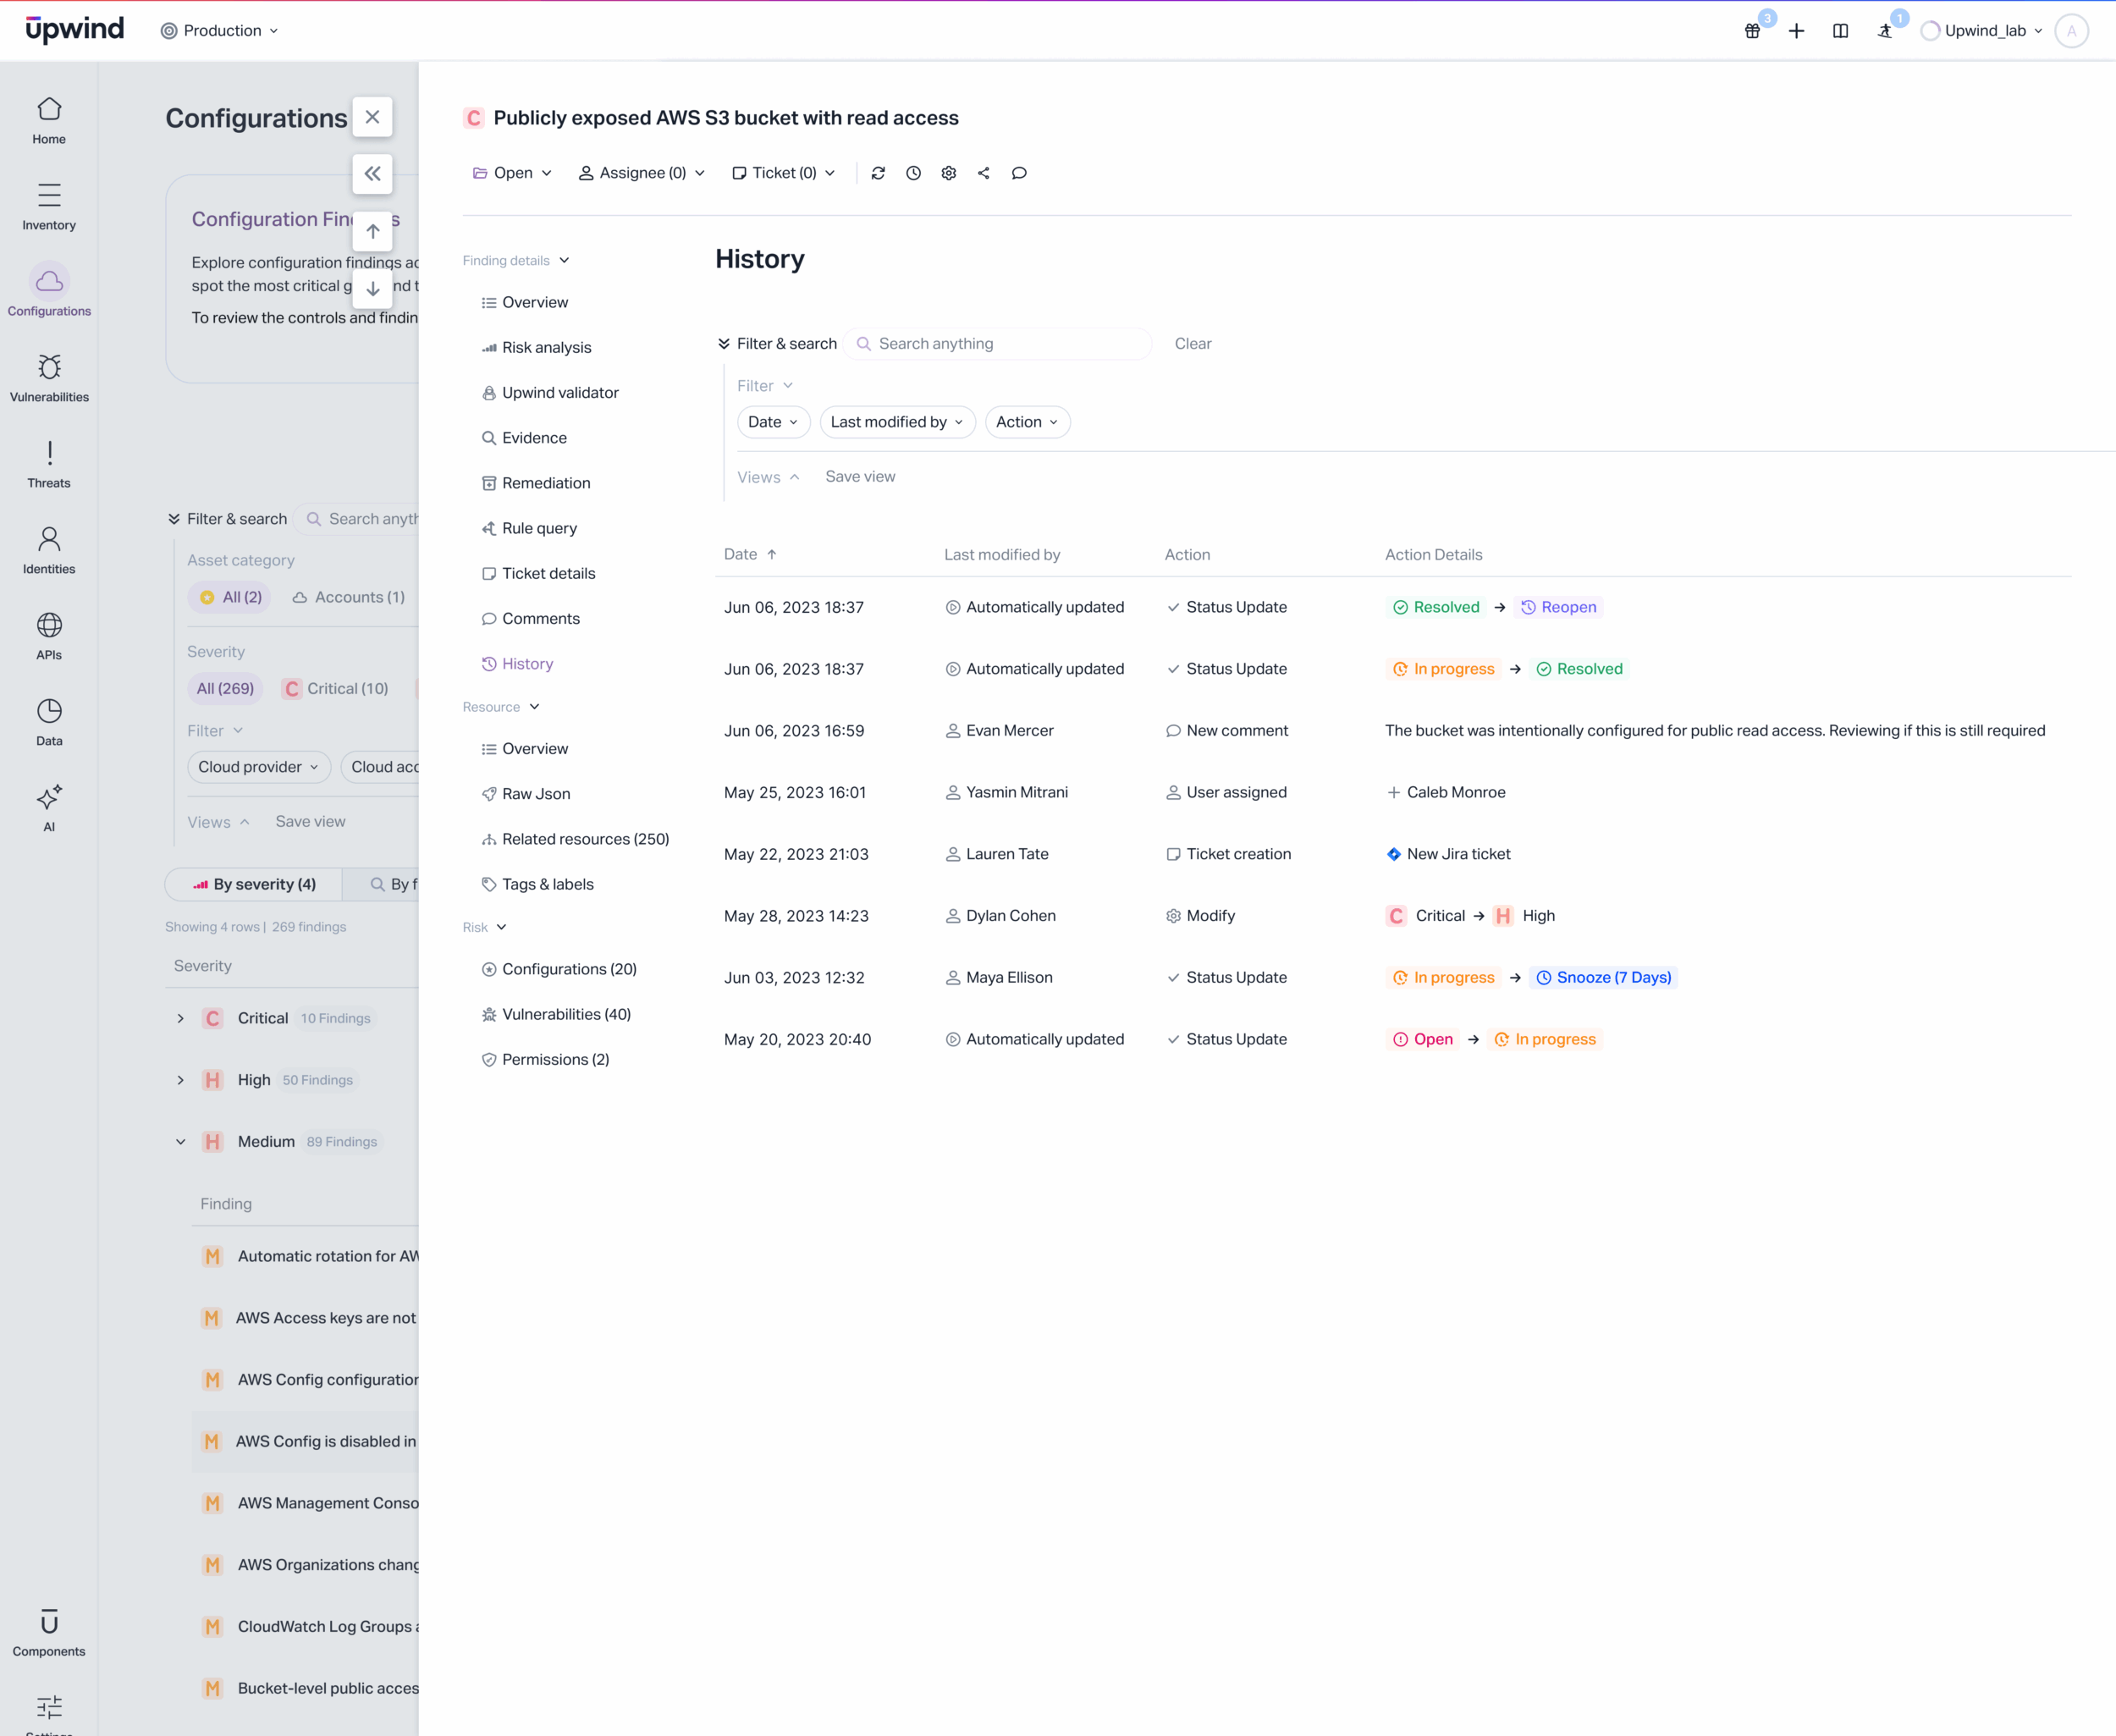
How Teams Drive Ownership in Upwind
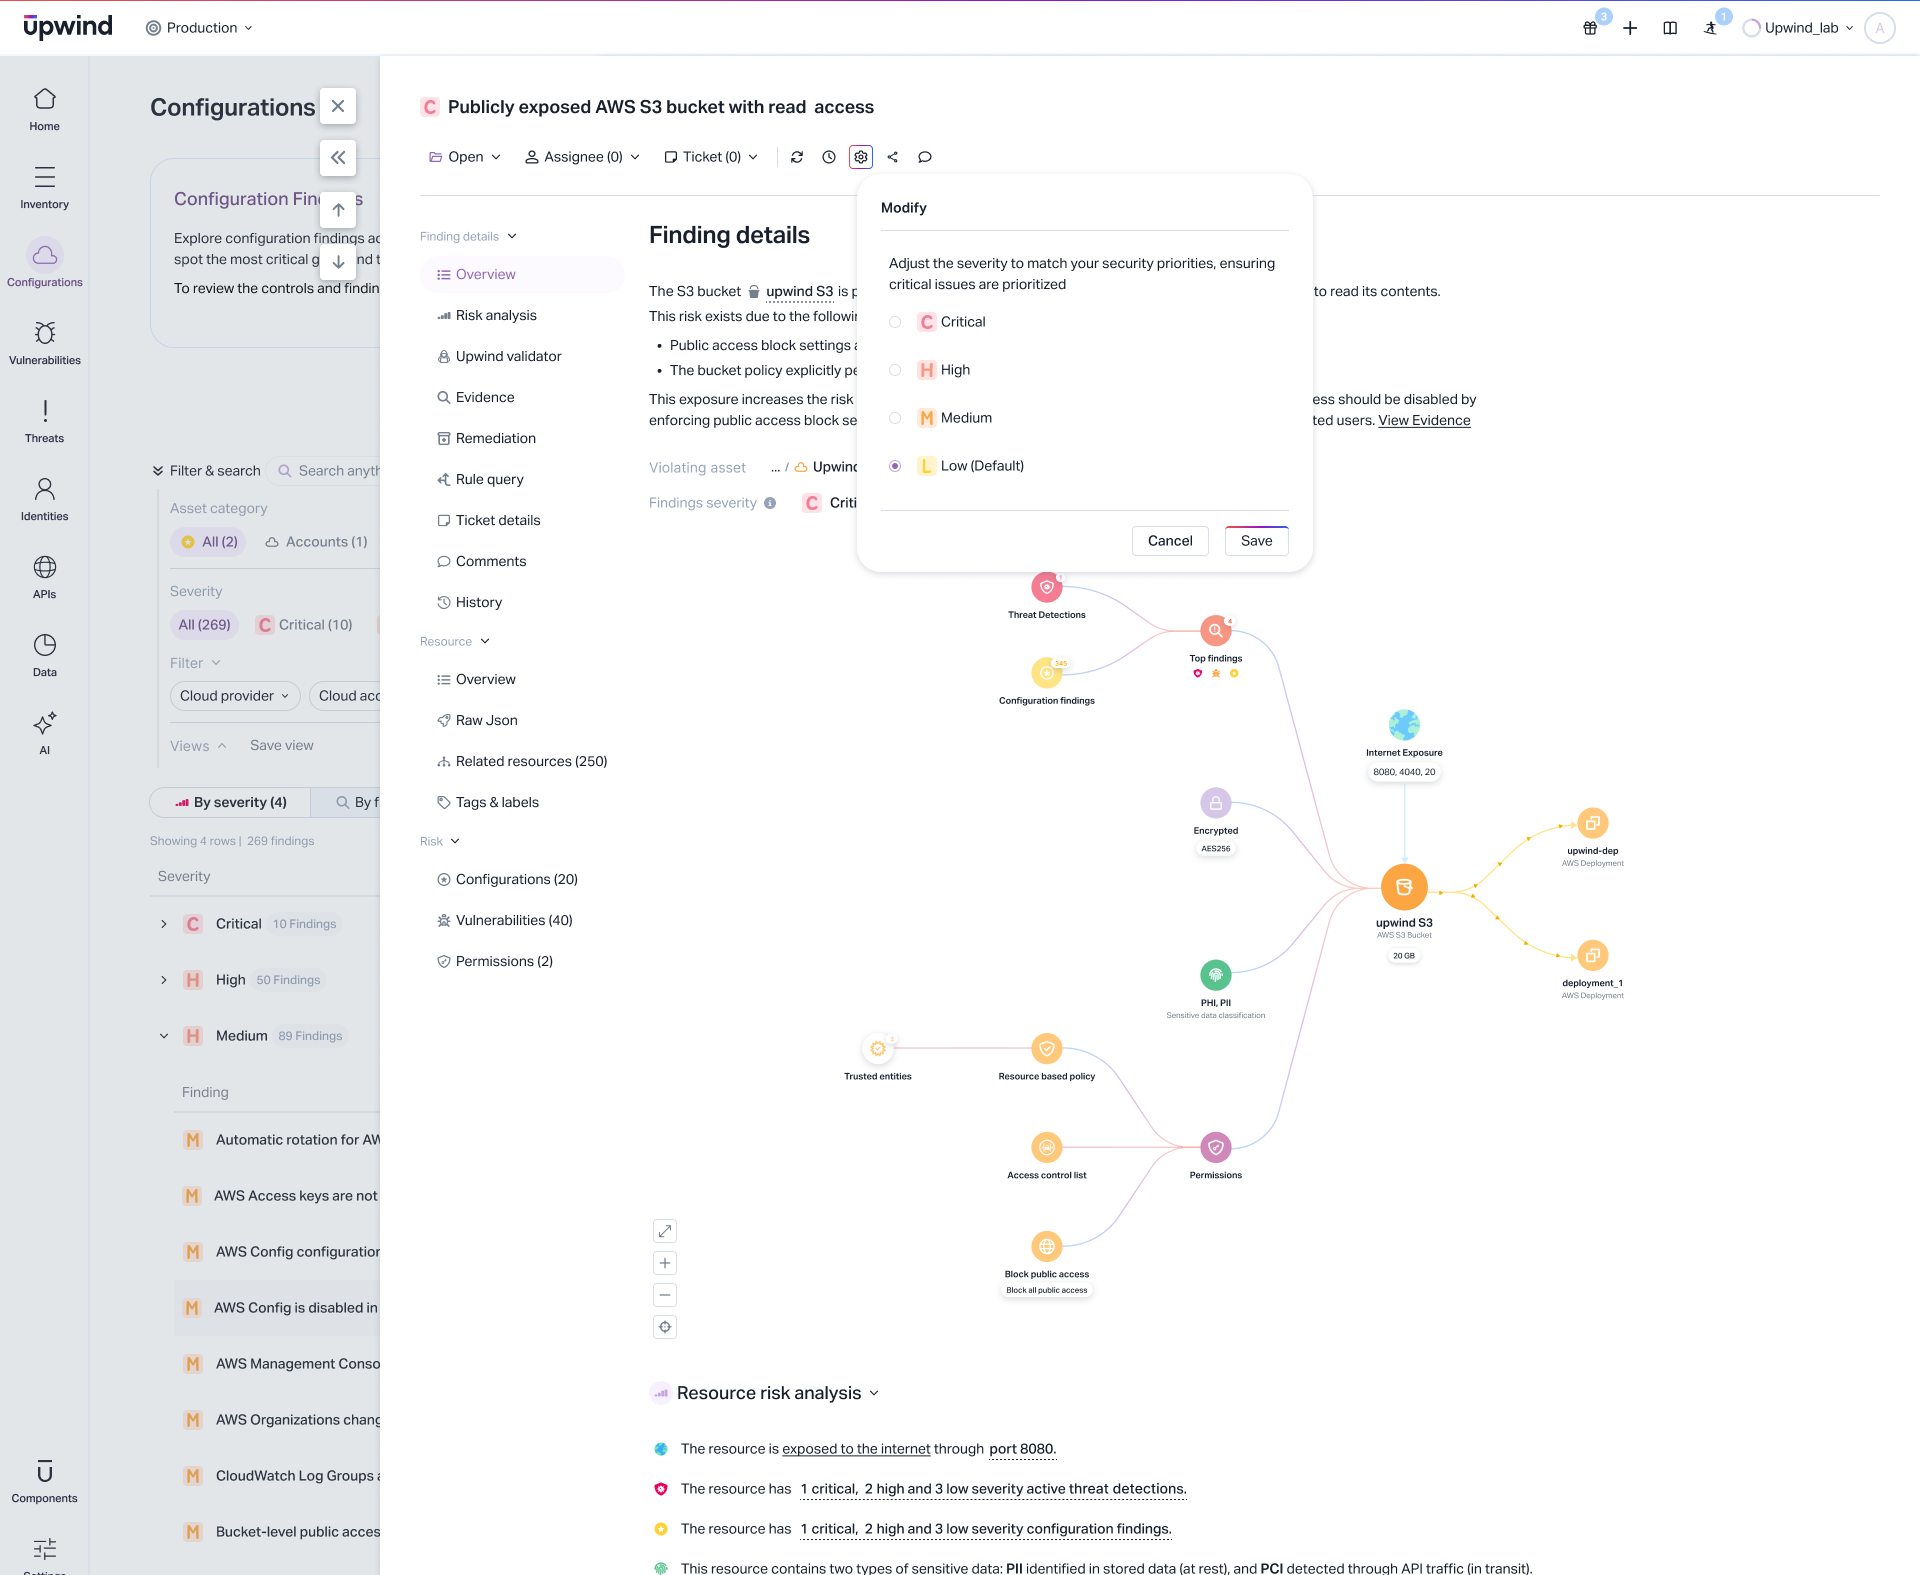
With Upwind, teams can now tailor how they manage findings, creating an environment where control and flexibility coexist.
These customizations include:
- Modify Severity: Adjust a finding’s criticality to match your organization’s priorities and ensure the right issues receive focus.
- Accept Risk: Mark findings that represent known or tolerable exposures, recording justification and ownership.
- Recast or Assign: Redirect a finding to another team or redefine its classification for accurate triage.
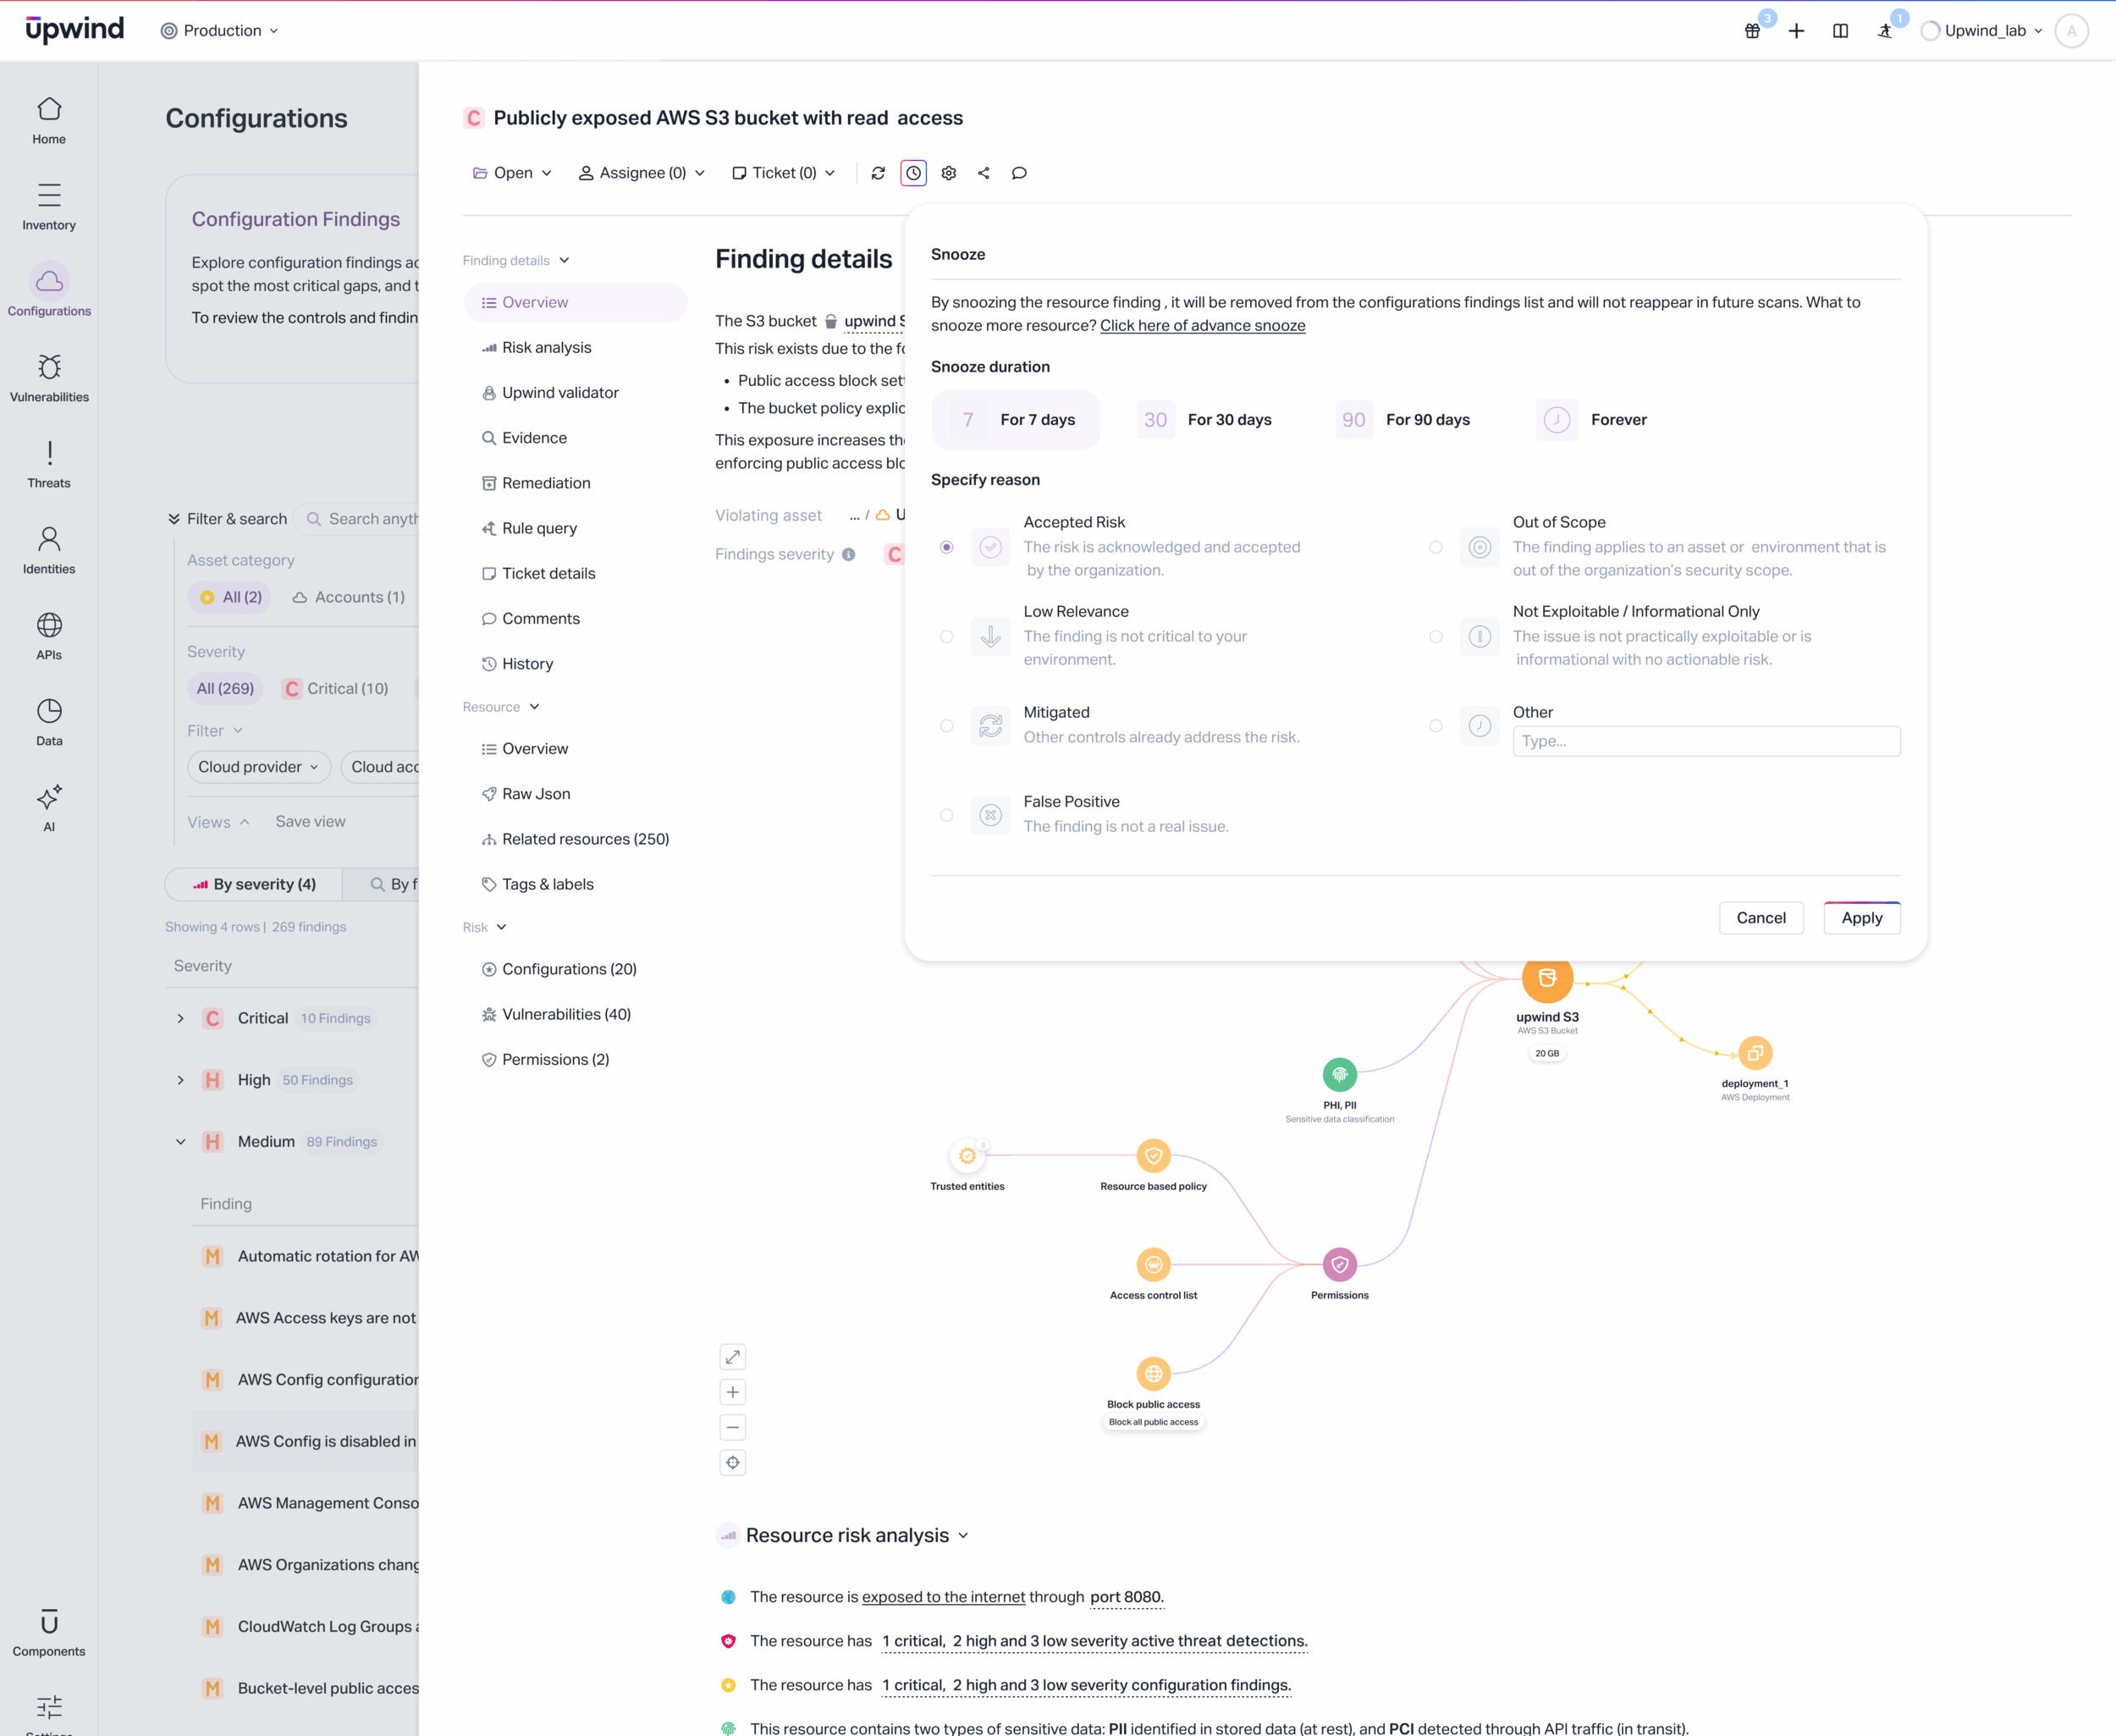
- Snooze Findings: Temporarily suppress low-priority or in-progress items without losing visibility or auditability, controlling snooze duration and the reason for snoozing the finding such as Accepted risk, Low relevance, or Mitigated.
All actions are unified under a single runtime-aware platform, ensuring shared context across dashboards, exports, and reports.
What’s Next
Upwind is continuing to enhance how teams manage findings across our platform. Upcoming releases will expand this control to more areas, including:
- Expanded Severity Modification: Empower teams to redefine issue criticality across the entire Upwind platform to better reflect business impact.
- Snooze Scope: Apply suppressions with precision using attributes like Resource Name, Kind, Account, and Labels.
- Public API Support: Automate actions through pipelines and internal tools for consistency at scale.
- Vulnerability Module Integration: Extend open source operations to vulnerabilities for unified risk control.
Redefining Open Source Security Through Ownership
At Upwind, we’re building a new model for how security operates: open, decentralized, and owned by everyone involved. By combining runtime intelligence with collaborative workflows, we’re creating an ecosystem where teams can collectively improve how risk is identified, prioritized, and resolved.
This is how we’re evolving the concept of open source security, not just as transparency, but as extreme ownership: where every team contributes, customizes, and continuously improves the way their organization defends itself.
If your team is ready to simplify how you manage findings and make security truly actionable, schedule a customized demo to see how Upwind can help you stay focused on what matters most.