Blog
Upwind Blog
Feed
Grid
Product
November 18, 2026
Attack in Review: 34 Minutes to Full Cluster Compromise

An attacker turned one HTTPS POST into a full compromise of a production EKS cluster in 34 minutes. We built Upwind Story Graph so that when an incident like this one lands on your team, you can see in one look how far the attacker got and what you need to shut first.Here is how…
November 18, 2026
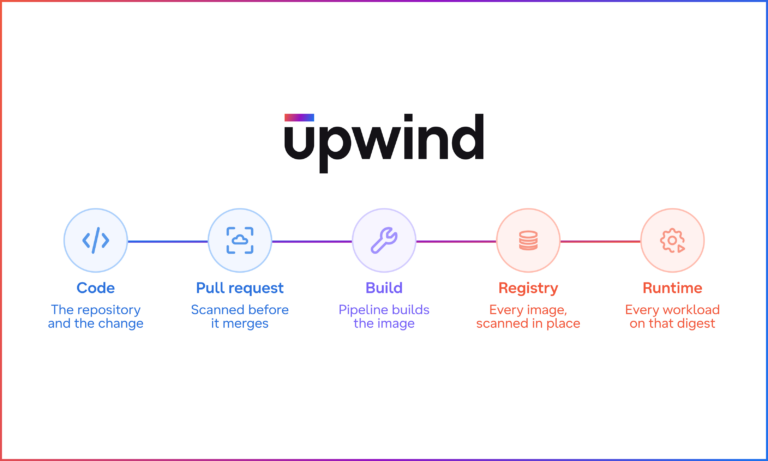
Upwind Now Follows Every Container Image From Pull Request to Runtime

Upwind now scans the container images in your cloud registries and follows every image from the pull request that changed it to the workloads running it. You catch risky images before they ship, and because Upwind also sees runtime, you know which of the running ones matter. Key Takeaways When an agent's pull request adds…
November 12, 2026
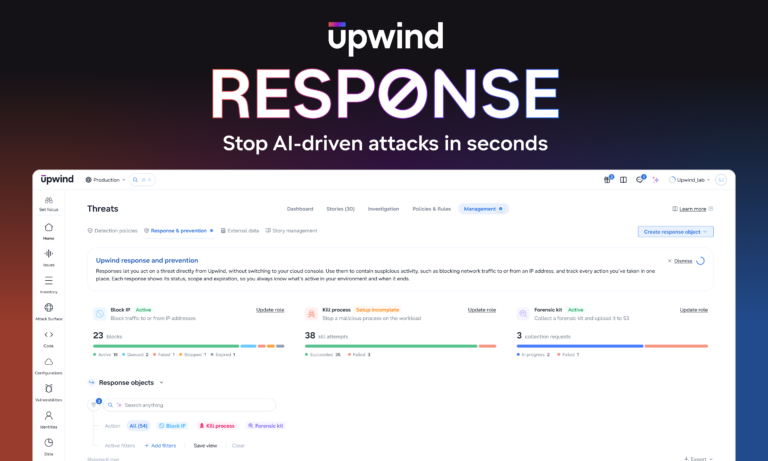
Introducing Upwind Response – The Next Wave in Cloud & AI Security

The CVE Tsunami is here, Vulnpocalypse if you will. In recent weeks, enterprises around the world have suffered real breaches. Our MDR heroes have spent weekends, days and nights with customers helping them to detect fast and contain their attacks. We came to a realization that detection, even the fastest detection, is no longer enough.…
November 4, 2026
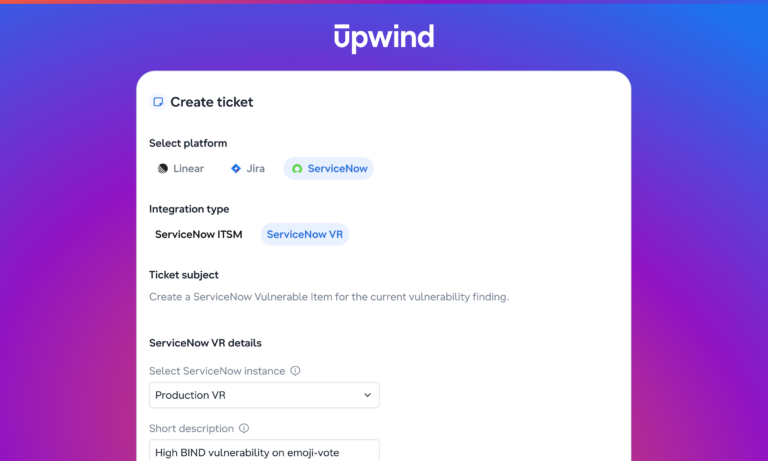
Upwind + ServiceNow VR: Only real findings reach the ticket queue

Send vulnerability findings straight into your VR queues, and let Upwind verify every fix before a ticket stays closed. Key Takeaways Upwind now integrates with ServiceNow Vulnerability Response (VR), the ServiceNow module where remediation teams track and fix vulnerabilities. The integration is generally available. It sends Upwind findings into VR as native Vulnerable Items and…
November 3, 2026
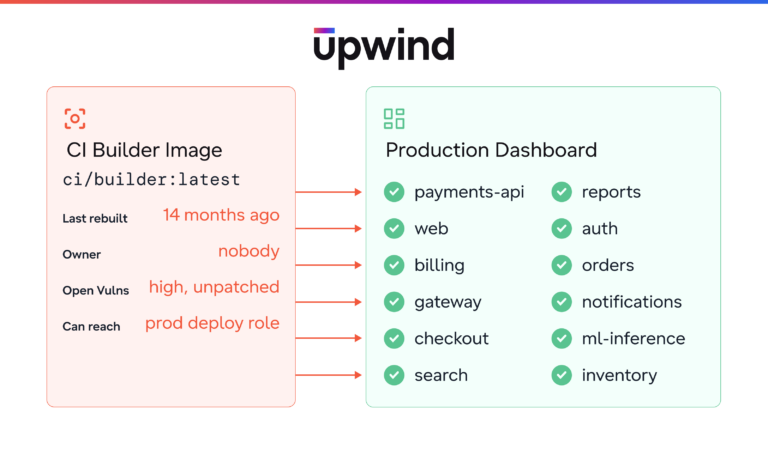
Your CI Runner Image Can Deploy to Prod. Who’s Scanning It?
How to find, rank, and trace the most privileged containers in your cloud before an attacker does Key Takeaways Every recent supply-chain attacks hit the build path Someone reports a compromise in a popular CI dependency, and security asks one question in the incident channel: "Are we affected?" Production dashboards are green, runtime alerts are…
October 22, 2026
The context gap: what runtime context changes in cloud and AI security


Key takeaways Most cloud security teams can see their environment. Inventory is broad, scanners run on schedule and findings pile up. What they can't tell you is which of those findings matter right now. That's the context gap. Visibility was the right foundation, and most programs have built it (see where yours sits on the…
October 21, 2026
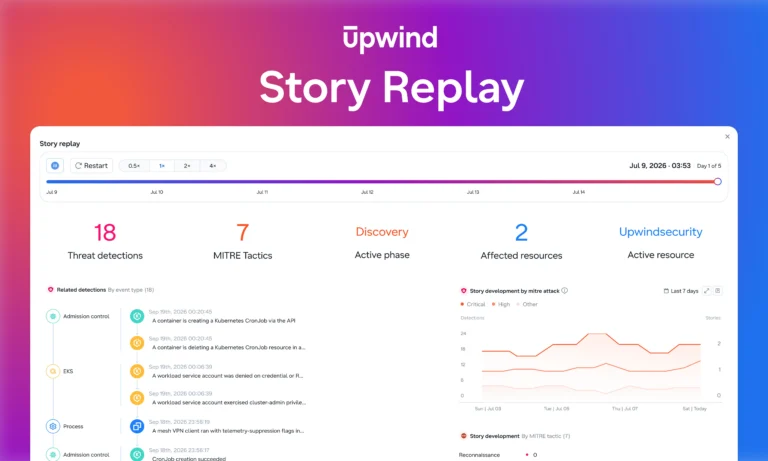
Upwind Story Replay: Watch the Attack Unfold

Upwind Story Replay is now available in Upwind: a visual timeline of the detections that led to a threat. Click a threat story, watch the attack unfold step by step. Three Vectors in One Week AI is accelerating everything we knew about supply chain attacks, zero-days, and finding new critical CVEs. Attacks are unfolding fast…
October 19, 2026
Runtime First, Agentless Everywhere
TL;DR Kubernetes has taken on a second job. Clusters still run the applications they always ran, but now they also run AI agents, model-serving workloads, and MCP servers alongside the applications those agents work on. These workloads do not behave like the applications Kubernetes was built to run. They call tools, reach external services, and…
October 19, 2026
Upwind Launches Databricks Security for Lakehouse Data and AI

Databricks permissions now trace to the cloud resources they actually reach. Ask a Databricks admin who can read a given catalog and you'll get an answer. Ask what that access reaches in your cloud account and nobody can tell you, because Databricks doesn't track it. Unity Catalog ends at the storage credential, and what sits…
October 19, 2026
Can AI Agents Safely Remediate Cloud Misconfigurations? We Tested 12 Models.


Introduction Teams are starting to let AI agents fix their cloud findings. What nobody has measured is whether those changes are safe to run. So we built a live AWS account, broke it on purpose in eighteen ways that chain into nine attack paths, and gave twelve AI models read-only access to it with one…
October 13, 2026
Upwind x Cursor Origin – Securing Software Factories


Upwind is partnering with Cursor Origin to secure every change pushed to the repository, whether a human or an agent wrote it. Upwind now scans code in Origin. Every pull request and every push to the default branch is checked automatically, with findings delivered as pull request comments, checks, and alerts in the Upwind console.…
October 7, 2026
What I’ve Learned Building a Technology Partner Ecosystem
Reaching 100+ integrations with The Lineup at Upwind is a milestone I’m incredibly proud of. But when I think about what it took to get here, the number itself isn’t the most interesting part. The interesting part is what happens along the way. You start by building integrations. Then customers introduce new use cases. Partners…
Attack in Review: 34 Minutes to Full Cluster Compromise
An attacker turned one HTTPS POST into a full compromise of a production EKS cluster in 34 minutes. We built Upwind Story Graph so that when an incident like this one lands on your team, you can see in one look how far the attacker got and what you need to shut first.Here is how…
Upwind Now Follows Every Container Image From Pull Request to Runtime
Upwind now scans the container images in your cloud registries and follows every image from the pull request that changed it to the workloads running it. You catch risky images before they ship, and because Upwind also sees runtime, you know which of the running ones matter. Key Takeaways When an agent's pull request adds…
Introducing Upwind Response – The Next Wave in Cloud & AI Security
The CVE Tsunami is here, Vulnpocalypse if you will. In recent weeks, enterprises around the world have suffered real breaches. Our MDR heroes have spent weekends, days and nights with customers helping them to detect fast and contain their attacks. We came to a realization that detection, even the fastest detection, is no longer enough.…
Upwind + ServiceNow VR: Only real findings reach the ticket queue
Send vulnerability findings straight into your VR queues, and let Upwind verify every fix before a ticket stays closed. Key Takeaways Upwind now integrates with ServiceNow Vulnerability Response (VR), the ServiceNow module where remediation teams track and fix vulnerabilities. The integration is generally available. It sends Upwind findings into VR as native Vulnerable Items and…
Your CI Runner Image Can Deploy to Prod. Who’s Scanning It?
How to find, rank, and trace the most privileged containers in your cloud before an attacker does Key Takeaways Every recent supply-chain attacks hit the build path Someone reports a compromise in a popular CI dependency, and security asks one question in the incident channel: "Are we affected?" Production dashboards are green, runtime alerts are…
The context gap: what runtime context changes in cloud and AI security
Key takeaways Most cloud security teams can see their environment. Inventory is broad, scanners run on schedule and findings pile up. What they can't tell you is which of those findings matter right now. That's the context gap. Visibility was the right foundation, and most programs have built it (see where yours sits on the…
Upwind Story Replay: Watch the Attack Unfold
Upwind Story Replay is now available in Upwind: a visual timeline of the detections that led to a threat. Click a threat story, watch the attack unfold step by step. Three Vectors in One Week AI is accelerating everything we knew about supply chain attacks, zero-days, and finding new critical CVEs. Attacks are unfolding fast…
Runtime First, Agentless Everywhere
TL;DR Kubernetes has taken on a second job. Clusters still run the applications they always ran, but now they also run AI agents, model-serving workloads, and MCP servers alongside the applications those agents work on. These workloads do not behave like the applications Kubernetes was built to run. They call tools, reach external services, and…
Upwind Launches Databricks Security for Lakehouse Data and AI
Databricks permissions now trace to the cloud resources they actually reach. Ask a Databricks admin who can read a given catalog and you'll get an answer. Ask what that access reaches in your cloud account and nobody can tell you, because Databricks doesn't track it. Unity Catalog ends at the storage credential, and what sits…
Can AI Agents Safely Remediate Cloud Misconfigurations? We Tested 12 Models.
Introduction Teams are starting to let AI agents fix their cloud findings. What nobody has measured is whether those changes are safe to run. So we built a live AWS account, broke it on purpose in eighteen ways that chain into nine attack paths, and gave twelve AI models read-only access to it with one…
Upwind x Cursor Origin – Securing Software Factories
Upwind is partnering with Cursor Origin to secure every change pushed to the repository, whether a human or an agent wrote it. Upwind now scans code in Origin. Every pull request and every push to the default branch is checked automatically, with findings delivered as pull request comments, checks, and alerts in the Upwind console.…
What I’ve Learned Building a Technology Partner Ecosystem
Reaching 100+ integrations with The Lineup at Upwind is a milestone I’m incredibly proud of. But when I think about what it took to get here, the number itself isn’t the most interesting part. The interesting part is what happens along the way. You start by building integrations. Then customers introduce new use cases. Partners…