
Security teams are drowning in alerts. Static scanners surface thousands of issues, but most are irrelevant. The real challenge isn’t finding problems, it’s knowing which ones to fix.
The Upwind + Jit integration brings runtime intelligence directly into AI-powered workflows so you can stop guessing and start fixing what matters. By combining Upwind’s real-time context with Jit’s automation, teams can immediately prioritize vulnerabilities that are actually exploitable in production, not just flagged by static scanners.
From Findings to Focused Action
Upwind continuously monitors cloud workloads at runtime using our eBPF-based sensor. We correlate vulnerability data with exposure, identity, privilege, and behavior, so when a container is vulnerable and exposed to the internet, or when a Lambda function contains secrets and has elevated permissions, it surfaces as a true operational risk.
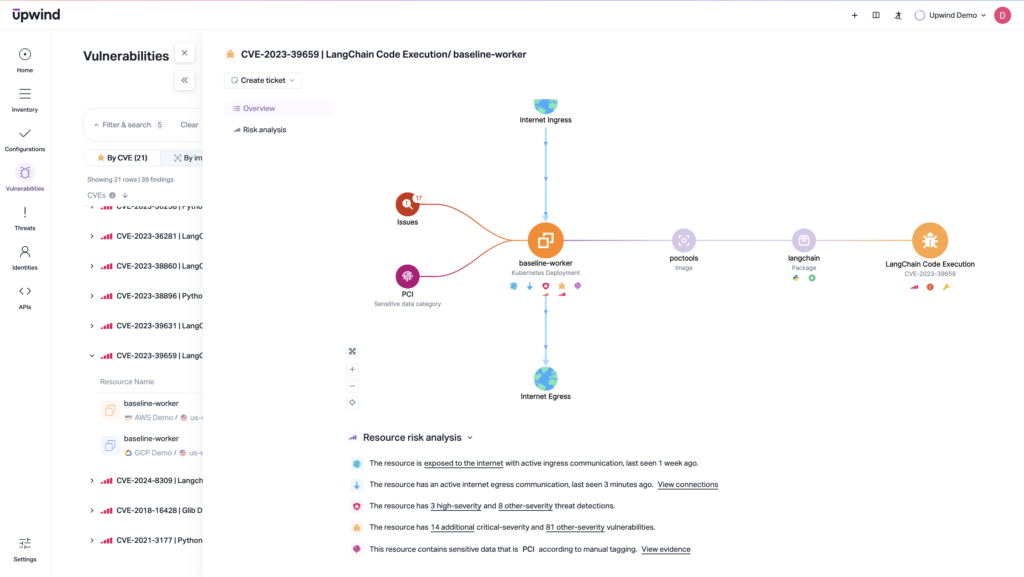
With the Upwind integration live, Jit’s AI Agents can instantly query Upwind’s APIs in real time, pulling that runtime context into their triage workflows. The result is a more intelligent, automated, and prioritized approach to security.
With Upwind’s runtime data flowing directly into Jit, security teams can triage smarter without leaving their workflow. This means:
- No more false positives: Filter out vulnerabilities that aren’t active, exposed, or reachable in production.
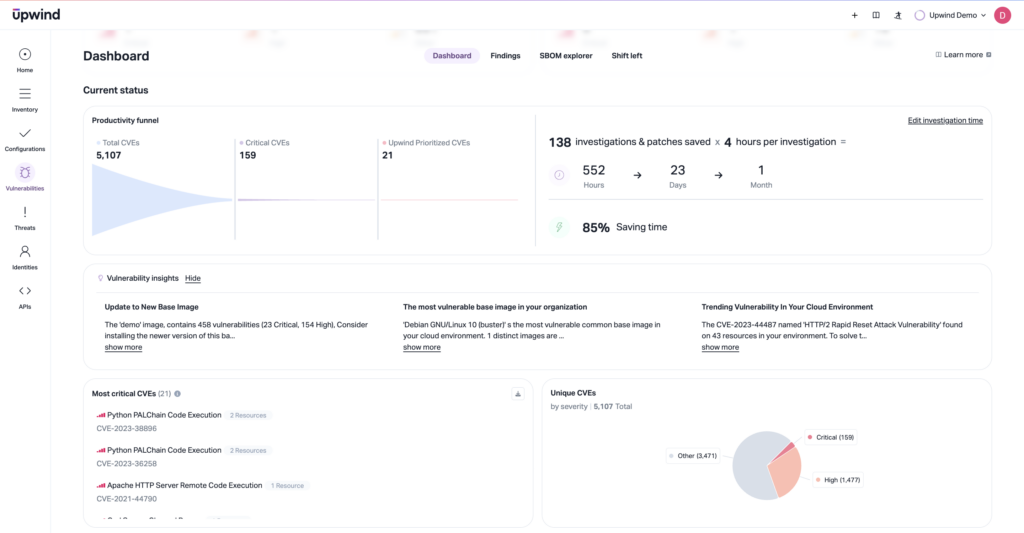
- Real prioritization: Focus on risks that matter most, based on Upwind’s live analysis of exploitability and behavior.
- Triage without switching tools: Upwind findings appear directly in Jit’s interface, enhanced with real-time context and ownership information.
Jit users can ask natural-language questions like, “What are the top 10 critical vulnerabilities in Application X?” and get prioritized answers in seconds, powered by real-time context and ranked by Upwind’s real-time risk signals – such as internet exposure, active usage, privilege levels, and network reachability.
How It Works
The integration is powered by Jit’s Model Context Protocol (MCP), which allows its agents to query Upwind’s API during inference. When a vulnerability is detected, Jit reaches out to Upwind in real time to determine whether the issue is:
- Running in a production environment
- Accessible from external networks
- Tied to elevated IAM permissions
- Involved in active workload traffic
Upwind returns structured, machine-readable results that Jit’s AI agents can use immediately – streamlining triage and reducing noise.
From Static Alerts to Real Risk Reduction
This integration helps solve a critical gap in modern AppSec: how to connect static scanner findings to runtime context, without manual work or guesswork.
With Upwind + Jit, security teams gain:
- Automated risk enrichment based on what’s actually running
- Structured, actionable data for prioritization
- Tighter collaboration between AppSec, DevOps, and engineering
Together, Upwind and Jit Together, Upwind and Jit turn endless alerts into clear, prioritized actions that secure your environment faster so teams stop wasting time chasing ghosts and focus on what truly matters. Book a demo today to learn how Upwind’s runtime prioritization engine automatically highlights critical vulnerabilities.