
Modern cloud-native environments offer unprecedented speed, scalability, and developer agility – but they also introduce complexity that traditional security tools struggle to manage. Containers spin up and down in seconds, microservices multiply rapidly, and infrastructure changes dynamically. Static logs and agent-based security solutions simply can’t keep up.
That’s where eBPF comes in – and why Upwind Security has made it the core of its platform.
Why eBPF Is Transformational for Runtime Security
eBPF is a Linux kernel technology that enables real-time, high-fidelity observability by allowing small programs to run safely inside the kernel. These programs can monitor system calls, network events, and process behavior as they happen – without needing to modify application code, inject sidecars, or rely on log scraping.
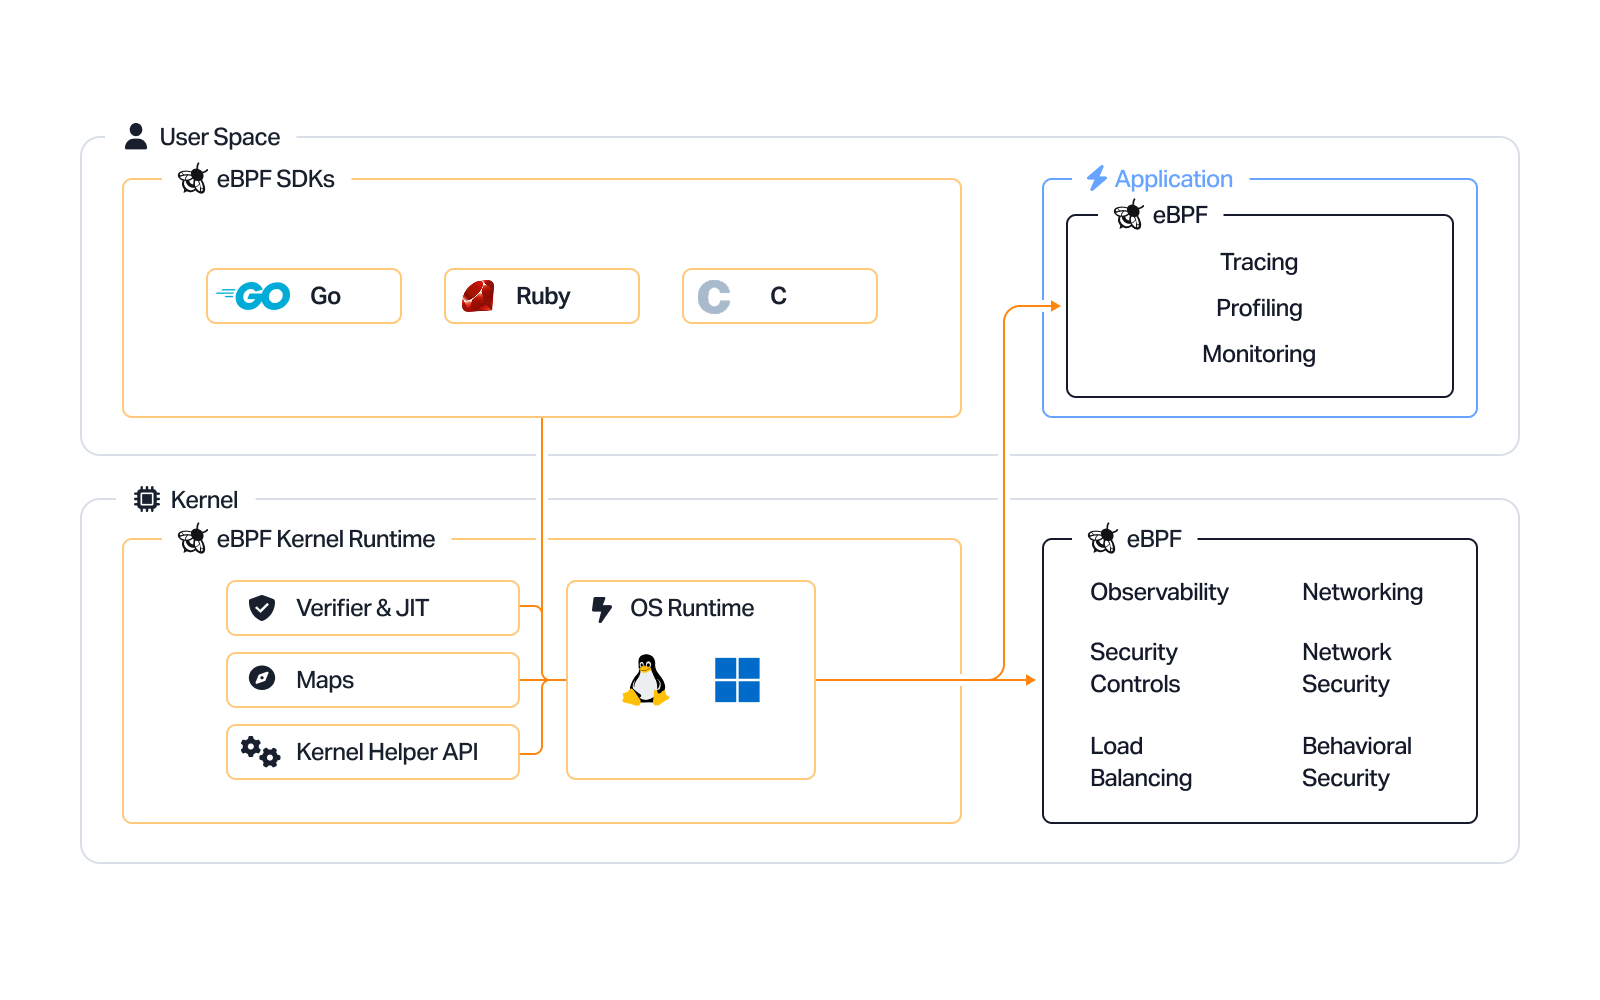
At Upwind, eBPF isn’t just a feature – it’s foundational. eBPF’s runtime insights underpin every pillar of cloud security, powering everything in the Upwind Platform and securing your cloud deployments, configurations, and applications through a runtime fabric that provides real-time visibility from the inside out. You get a live map of your network and application topology, can prioritize fixes based on real usage, and detect threats as they happen. With Upwind, security, dev, and ops teams move faster, stay focused, and fix risks that matter most.
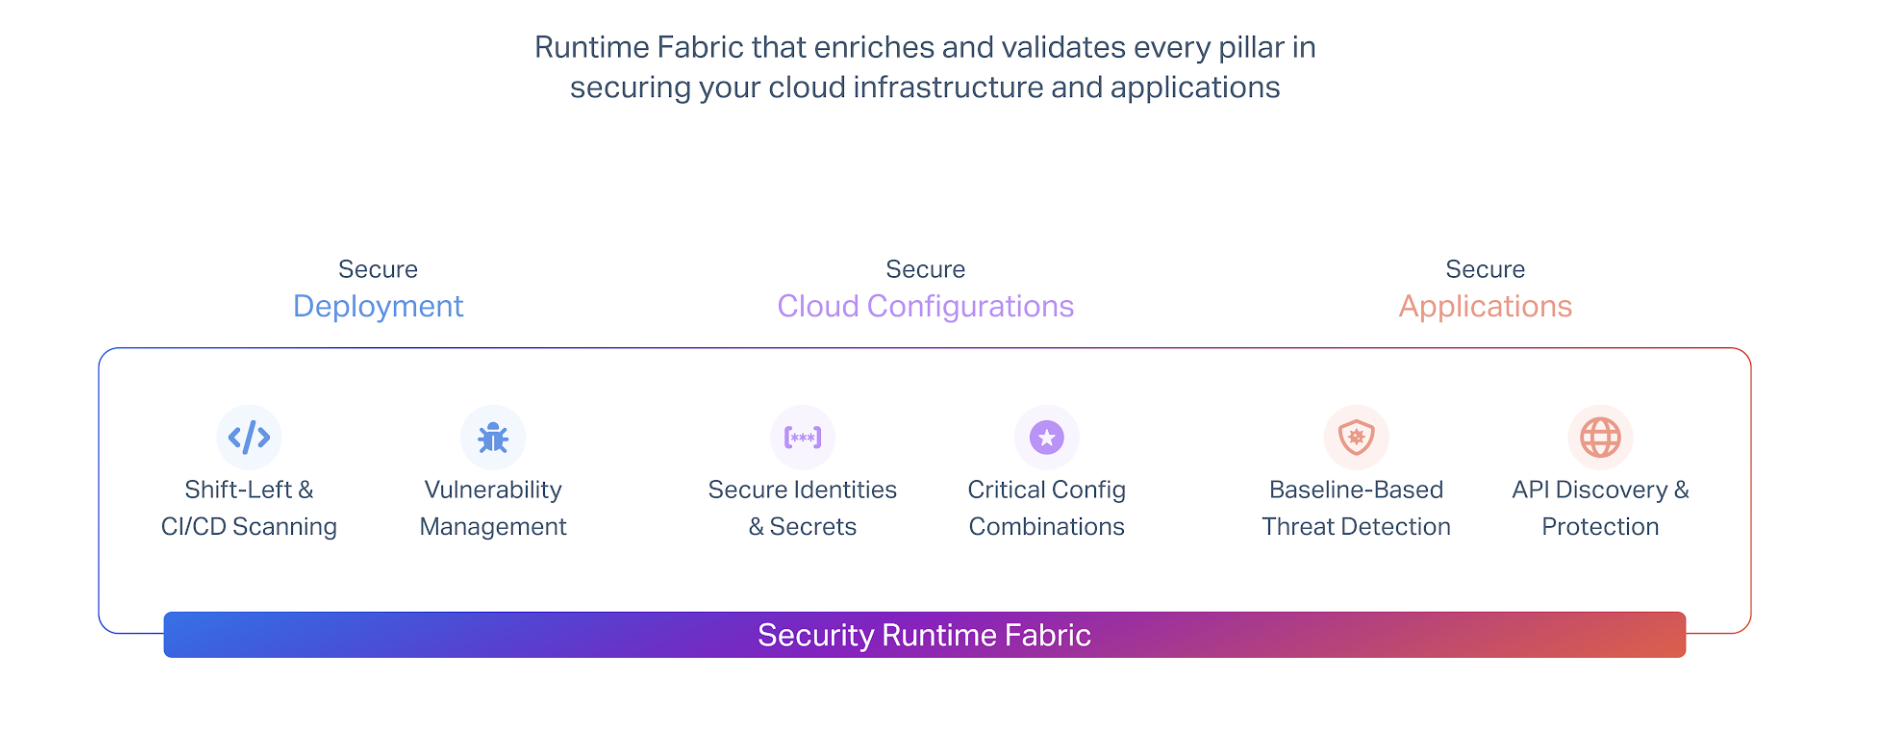
What That Means for You
Upwind leverages eBPF to transform raw system telemetry into actionable, context-rich security insights, like:
- Real-Time Threat Detection: Upwind monitors system calls and network activity as they happen, detecting suspicious behavior instantly – not minutes or hours later.
- Context-Enriched Alerts: Every event is mapped to the relevant pod, service, namespace, cloud account, or container image. That means fewer false positives and more actionable alerts.
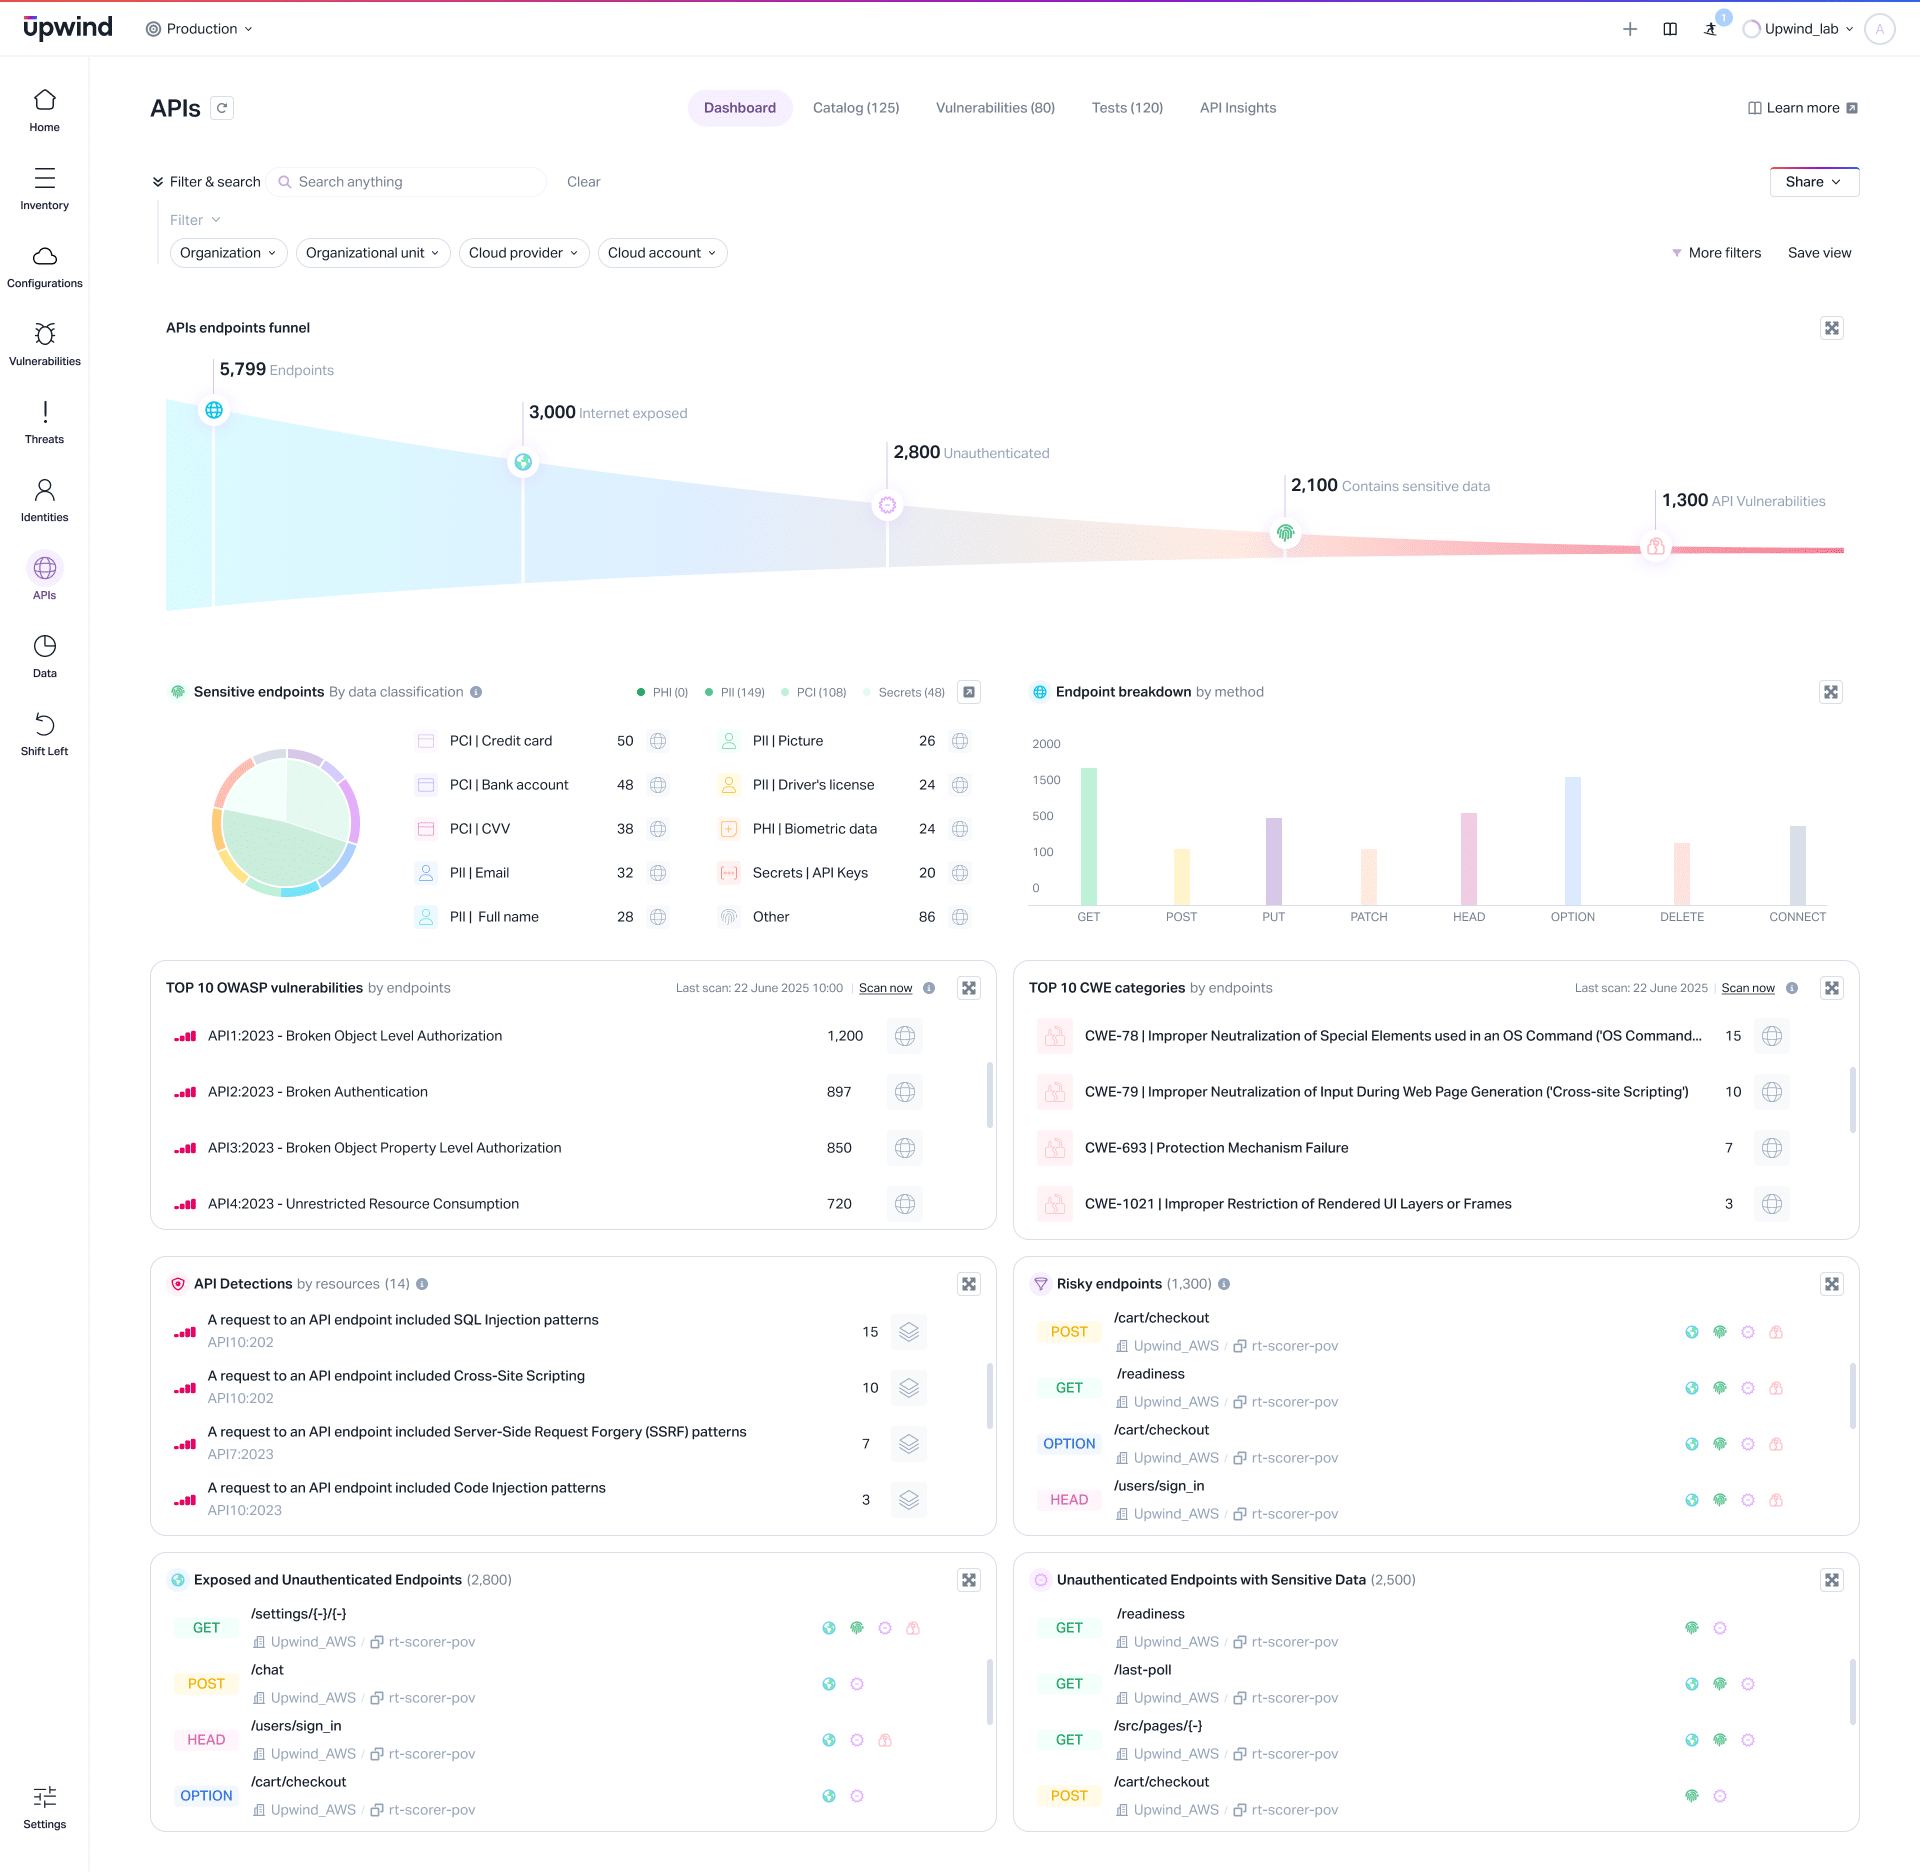
- Deep API Visibility Without Sidecars: Upwind inspects socket-level traffic using eBPF to reconstruct API calls – even for encrypted traffic or undocumented services – without the need for sidecars or proxies.
- Granular Data Flow Tracking: Whether it’s sensitive data like PCI or PII, or unexpected lateral movement across tenants, Upwind maps where data flows in real time, ensuring compliance and catching misconfigurations before they become breaches.
Built to Scale, Designed for Safety
Security tools often struggle to scale in cloud native environments because of added overhead from sidecars or packet duplication. Upwind avoids those pitfalls with eBPF, achieving zero-copy visibility with near-zero impact on system performance.
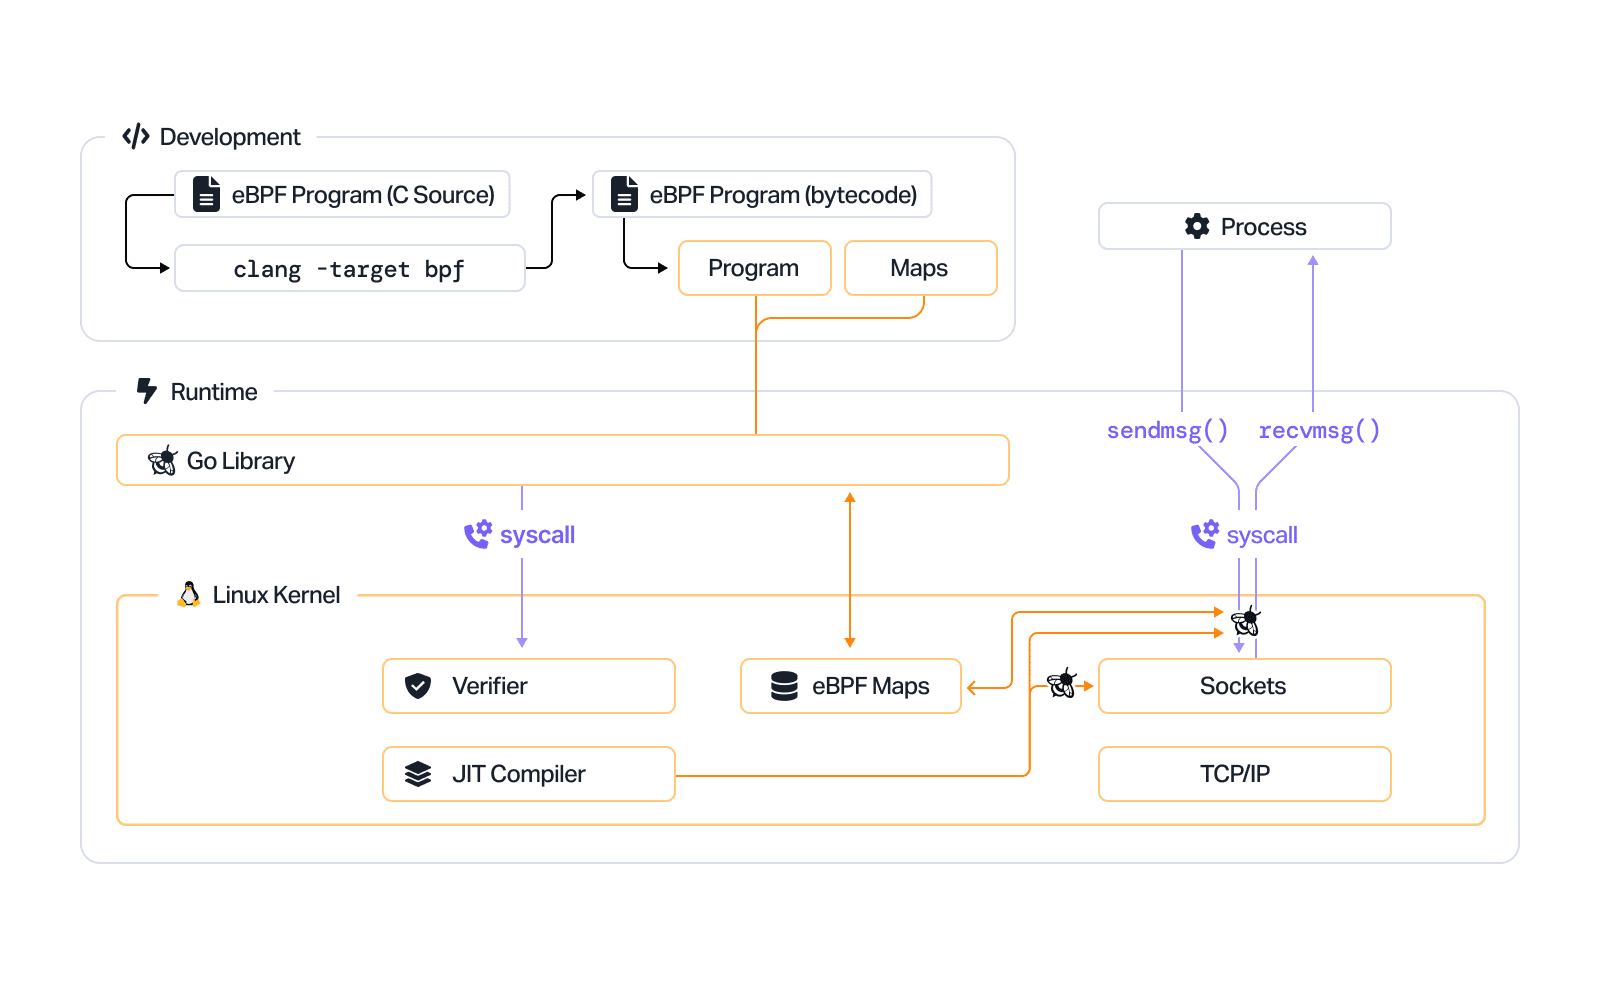
Additionally, all eBPF programs loaded by Upwind are statically verified by the kernel, ensuring safety, bounded execution, and resilience – even under high workloads or bursty traffic patterns. This makes Upwind an ideal solution for dynamic, high-density environments, from multi-cloud Kubernetes clusters to hybrid deployments with complex compliance needs.
From Kernel Signals to Complete Security Context
Perhaps the most powerful feature of Upwind’s approach is how it transforms low-level system signals into high-context security intelligence. This allows Upwind to do things most tools can’t:
- Trace incidents across ephemeral workloads, even after the container is gone.
- Administer policy based on workload identity and behavior rather than just static IPs or ports.
- Investigate and respond faster, with full visibility into the system call, the user, the image, and the associated cloud service.
Real eBPF Use Case
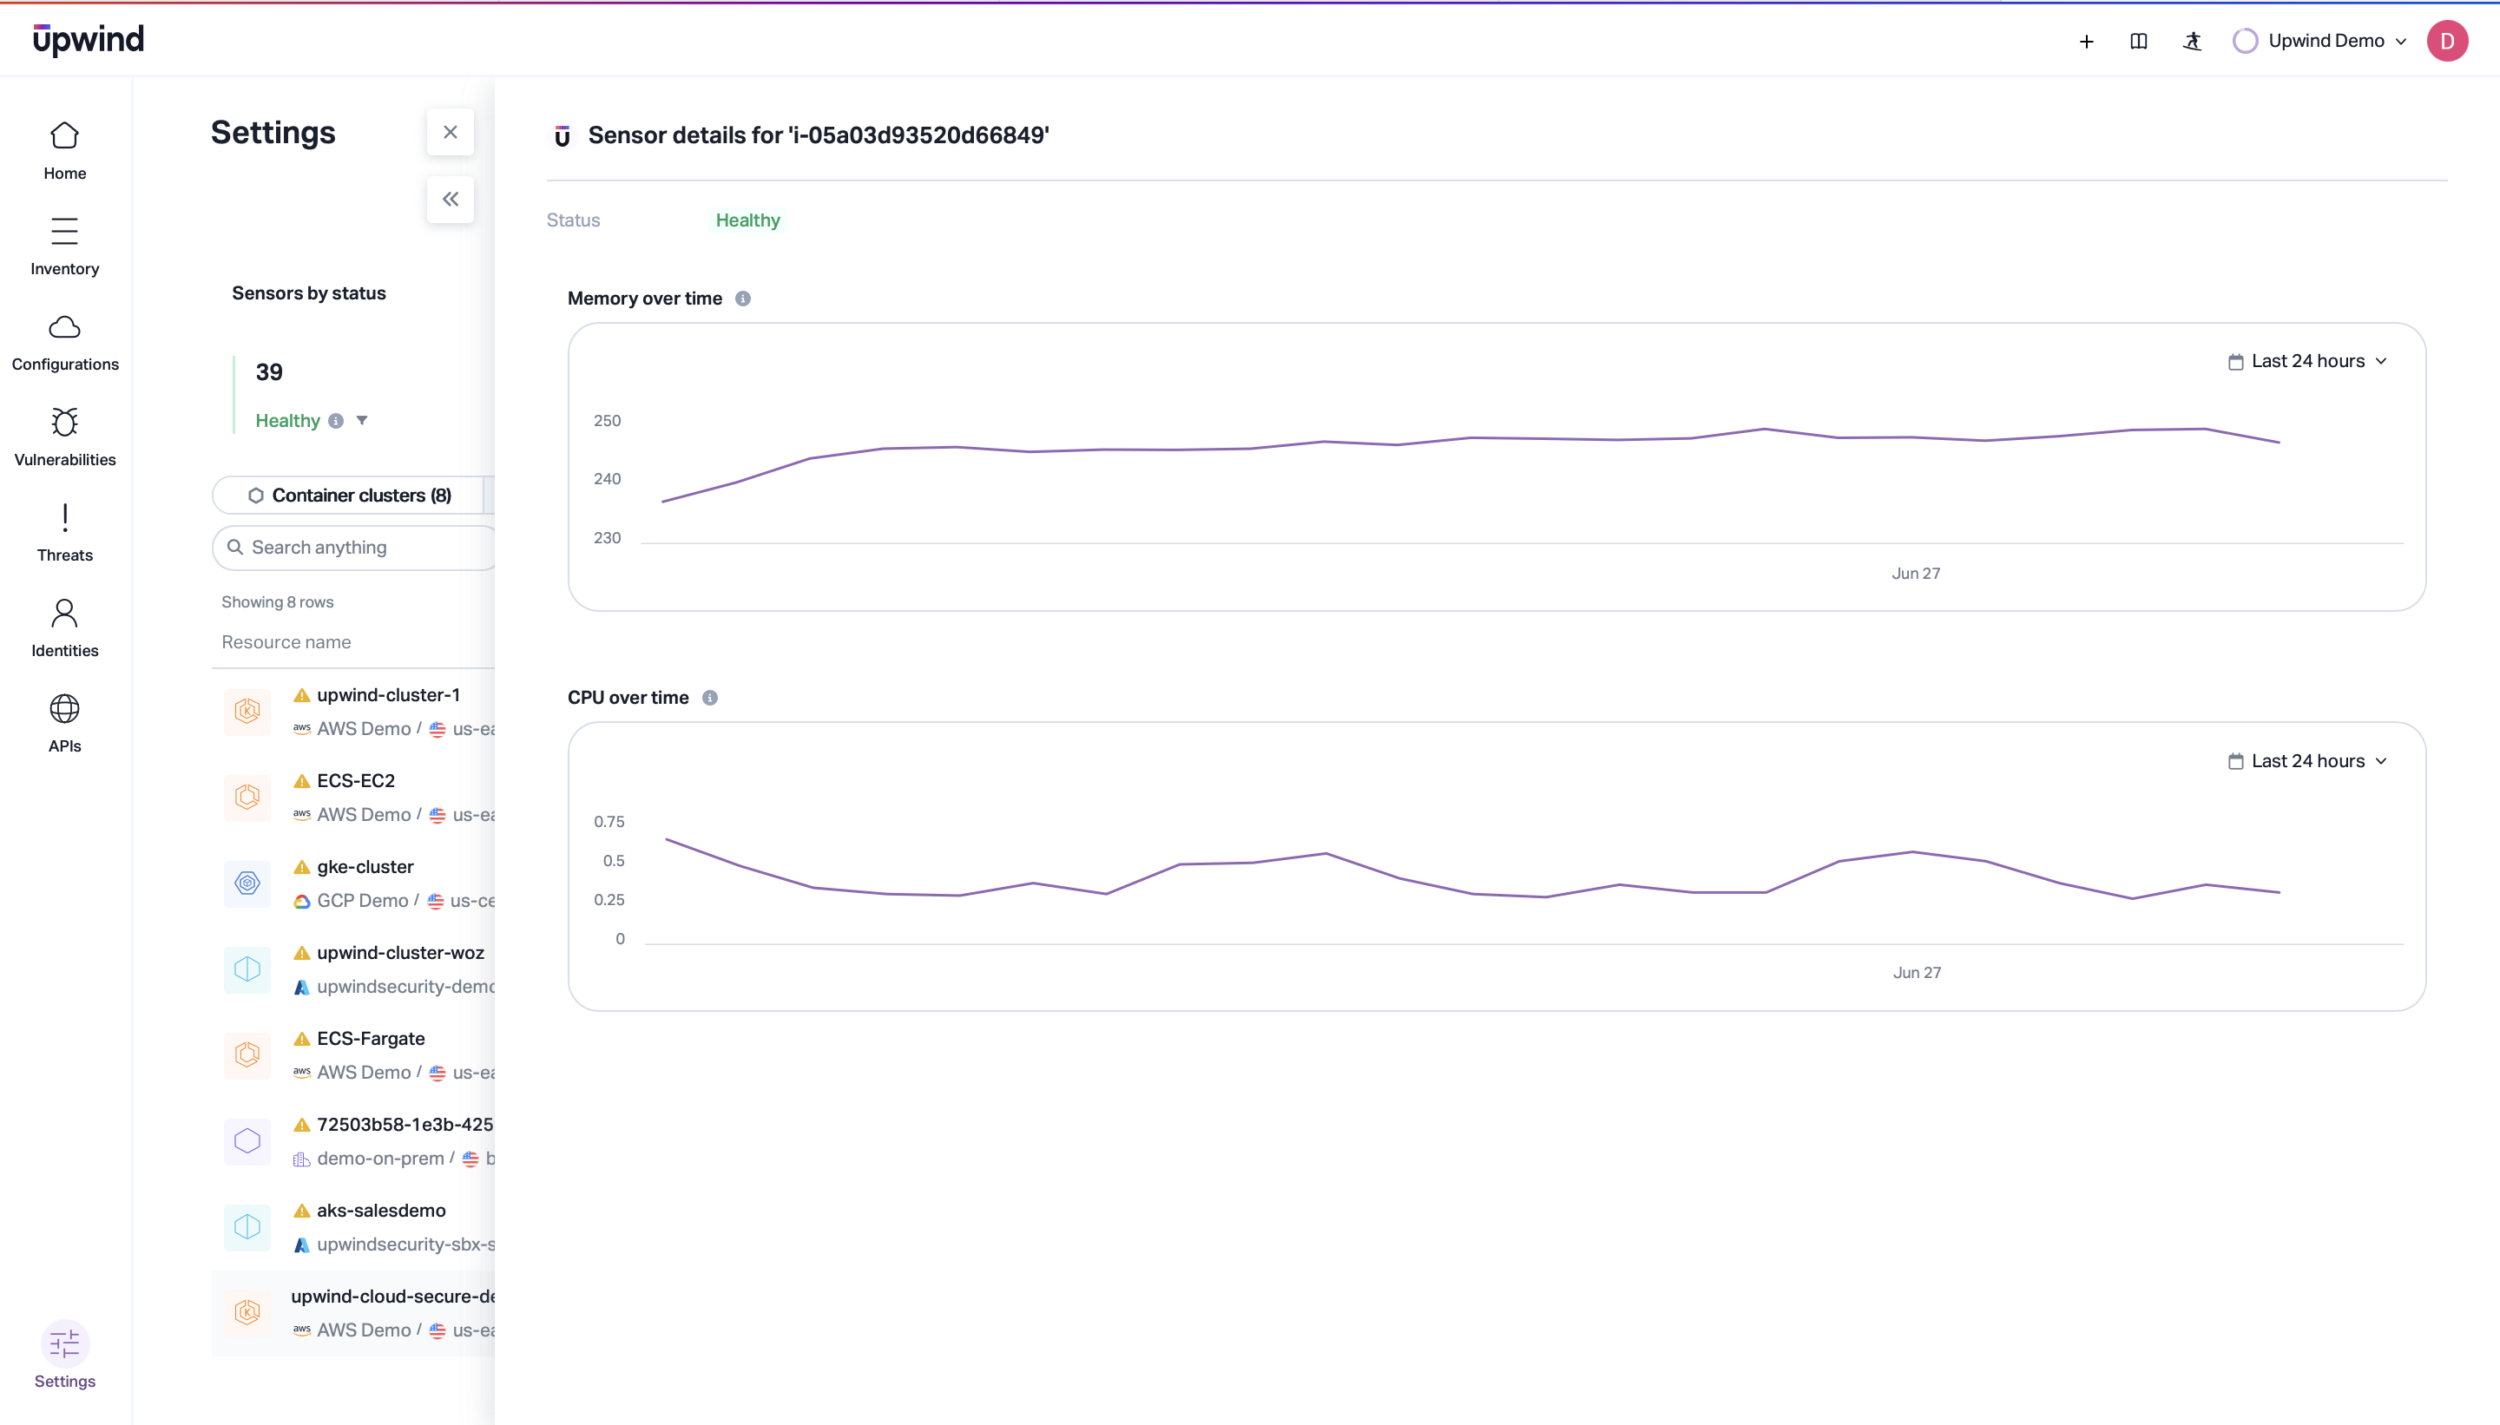
The Upwind eBPF-based sensors are high-performance, lightweight and easy to deploy and monitor. Data aggregated across the Upwind customer base has shown that the average Upwind sensor CPU usage is less than 1% – with many nodes showing sensor CPU usage of under 0.1%. Upwind customer H2O.ai reported that when scanning a 30GB container image with multiple dependencies, the Upwind sensor consumed less than 1GB of RAM, about 3% of the image size, demonstrating how Upwind ensures comprehensive runtime security coverage with a lightweight footprint.
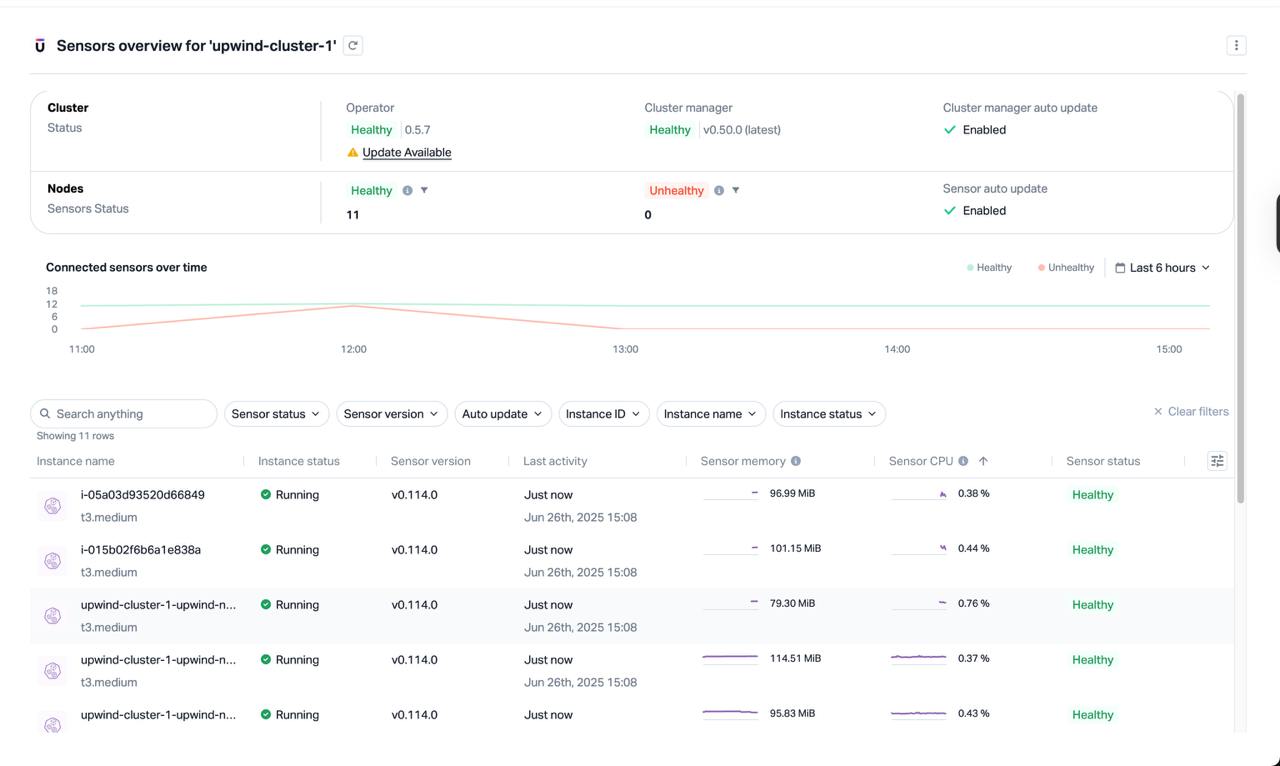
Beyond high performance metrics, the Upwind sensor provides deep runtime protection and context, including:
- Threat detection
- Process instrumentation
- Memory instrumentation
- File access
- API inspection and security
- Vulnerability scanning
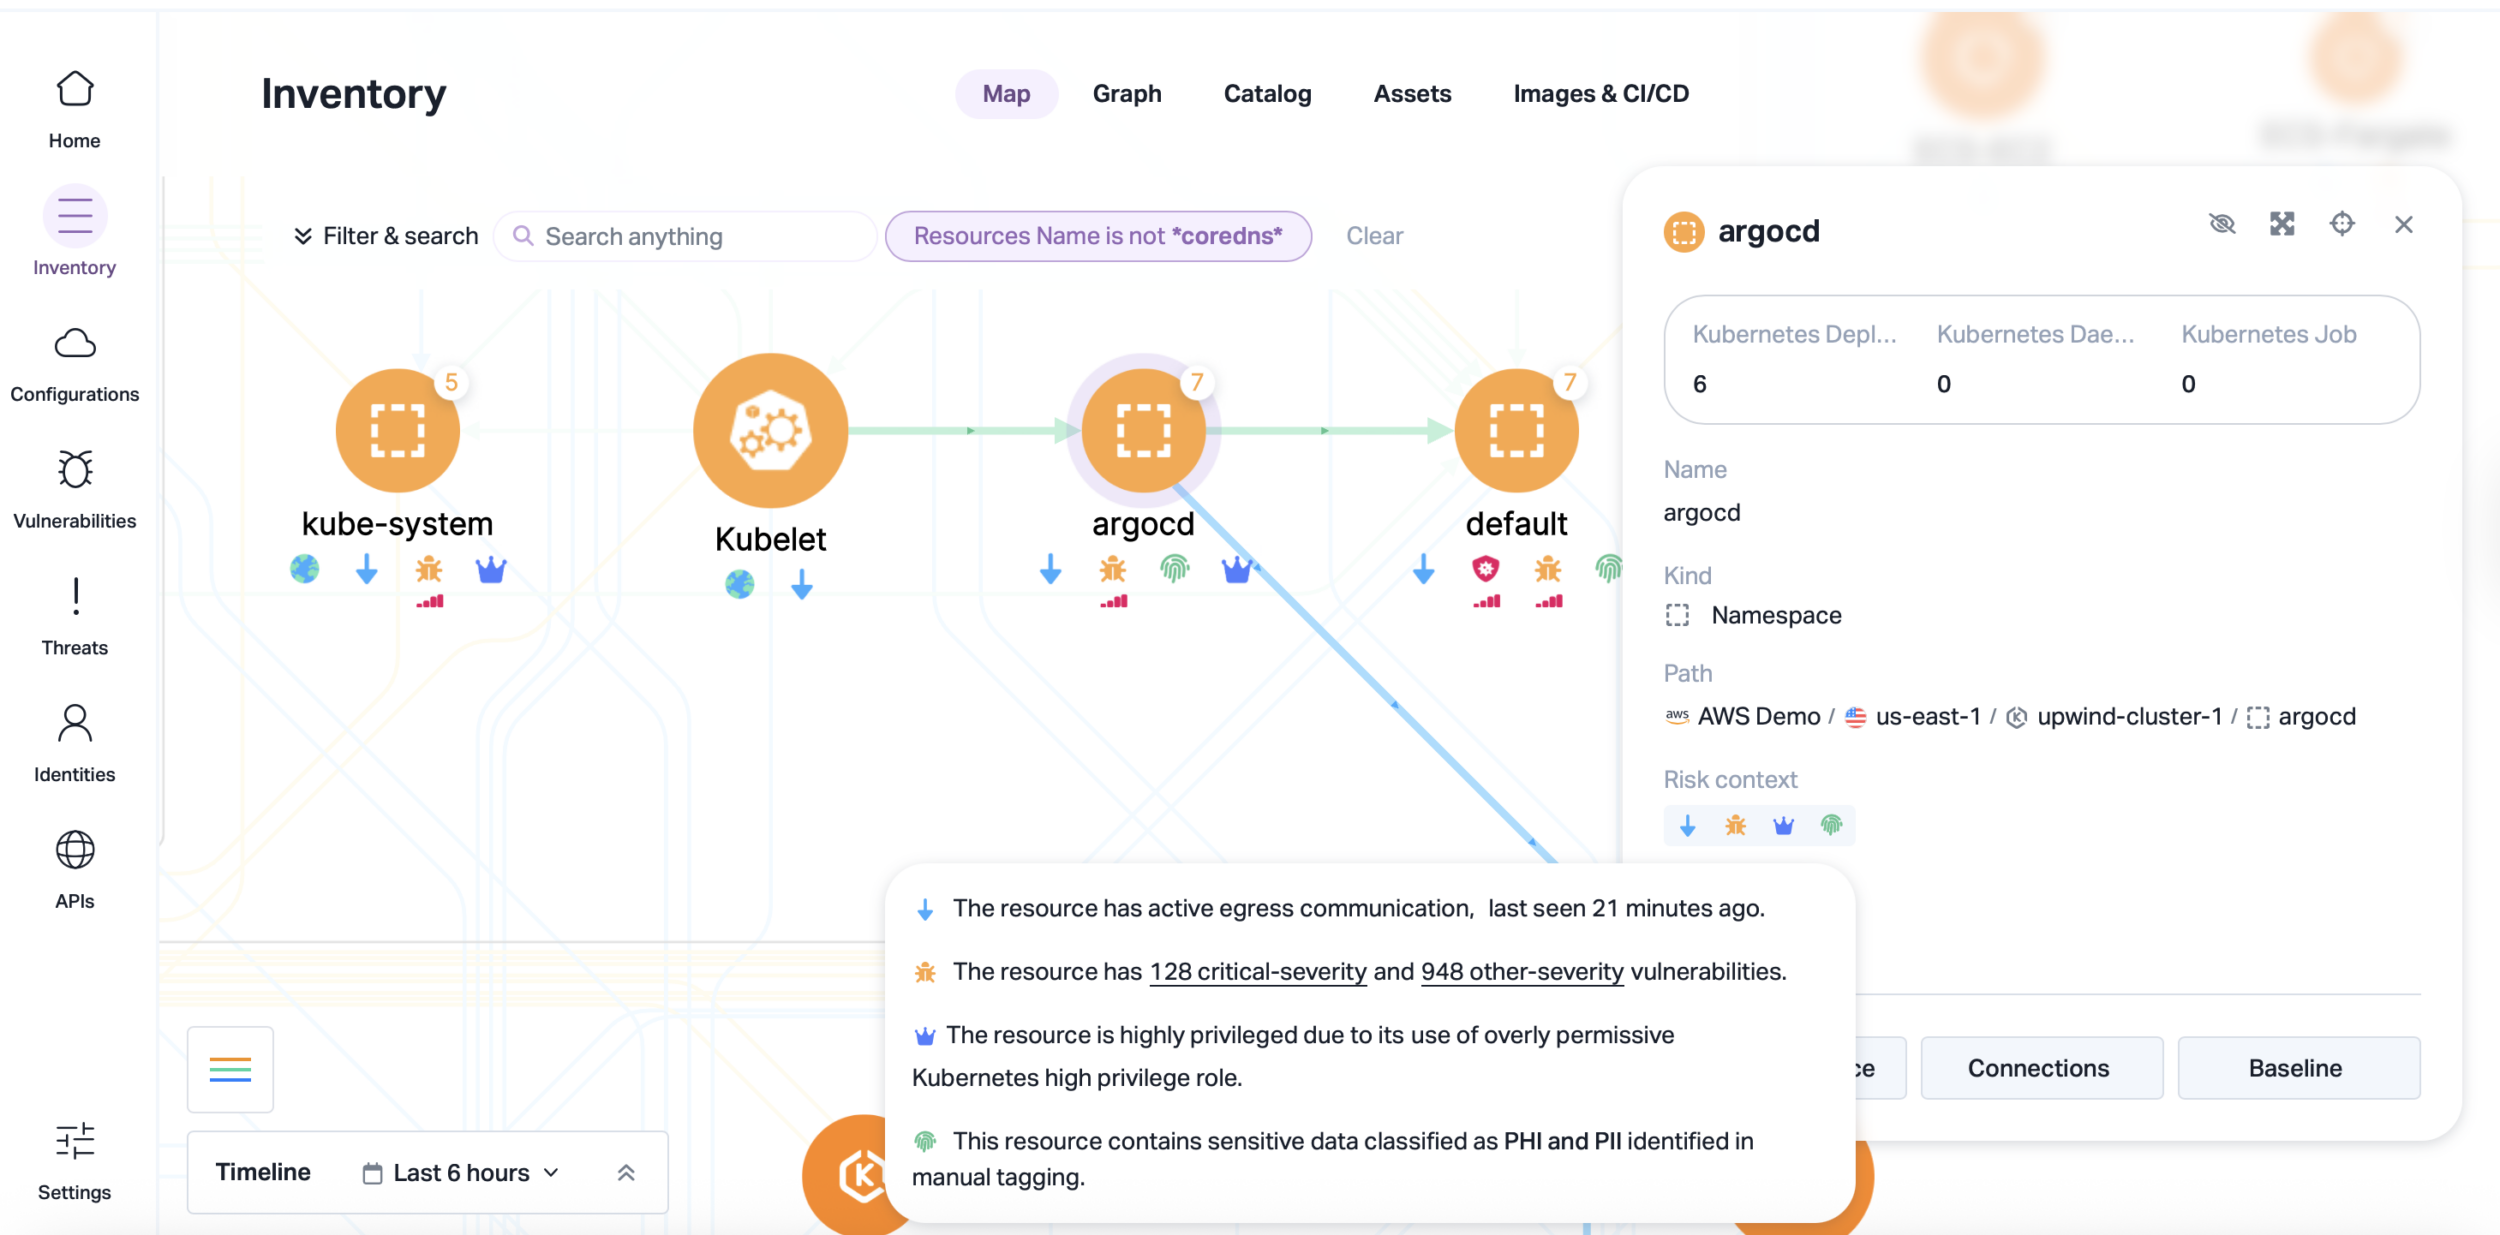
By leveraging the Upwind eBPF sensor, organizations can seamlessly monitor and correlate insights from layers 3, 4 and 7 of the network stack – providing unified visibility into cloud infrastructure and applications.
Want to Learn More?
To dive deeper into how Upwind uses eBPF to unlock kernel-level observability and real-time threat detection, download our white paper on eBPF or schedule a live demo with our team.