
We are excited to announce support for a new detection type: identification of malicious port scans.
Port scanners are applications that probe a host or server to find open ports or “weak points” in your network. These can be used by malicious actors to exploit vulnerabilities and identify network or security services running on a host.
Port Scanning
There are a variety of TCP ports, numbered from 0 to 65535, with the standard ports occupying numbers 0 to 1023. A standard port that is left open can indicate an infected or vulnerable port.
Commonly used ports include:
- Port 20 (UDP): File Transfer Protocol (FTP) for data transfer
- Port 22 (TCP): Secure Shell (SSH) protocol for secure logins, FTP, and port forwarding
- Port 23 (TCP): Telnet protocol for unencrypted text commutations
- Port 53 (UDP): Domain Name System (DNS) translates names of all computers on internet-to-IP addresses
- Port 80 (TCP): World Wide Web HTTP
Port scans are not always malicious – they can also occur when security services are deployed on virtual machines in your environment. This occurs because the services conduct port scans to alert you to potentially misconfigured ports that have been left open.
Indicators of Compromise
Potentially malicious port scans are detected through their suspicious access patterns – including repeated attempts to connect to multiple ports over a short period of time, or connecting a resource or host to multiple ports over a short period of time. A port scan attack aims to locate open ports to discover which services the machine is running and to identify its operating system, to inform which vulnerabilities to exploit.
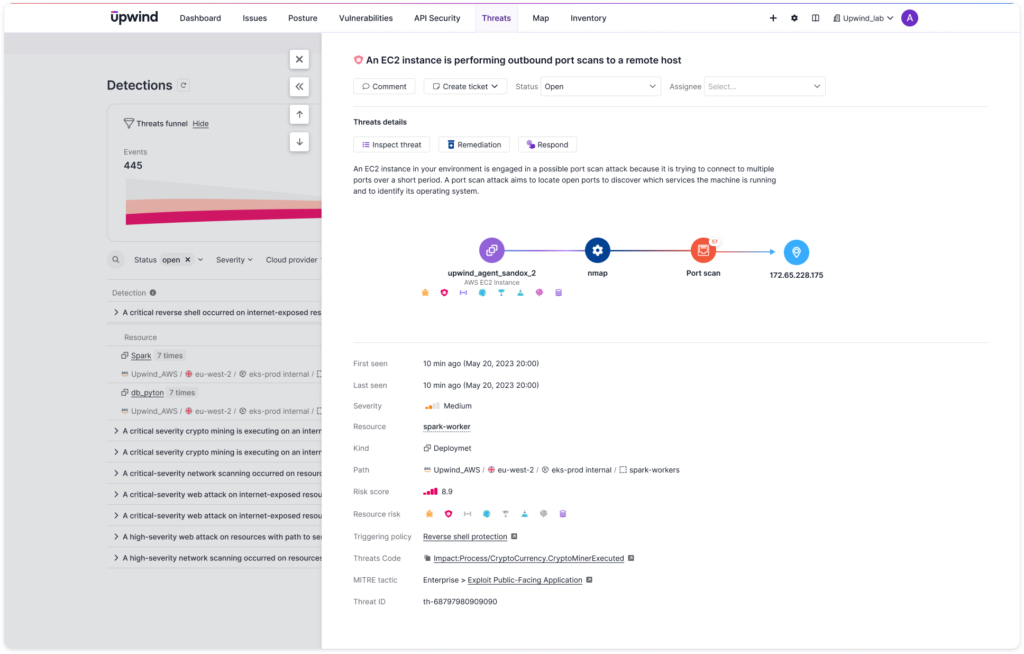
A port scan can provide useful information about a network environment, including:
- Existing network defenses, such as firewalls
- Running applications
- Machines that are online
- Information about the targeted system
- Information about vulnerable networks and servers
Attackers can then use this information to conduct an attack on a virtual machine.
Port Scan Attack Methods
In a port scanning attack, attackers generally do one of the following:
- Leverage a resource to perform outbound port scans to a remote host
- Use a remote host to port scan a resource
- Use an internal source to port scan a resource
- Leverage a remote host using UDP to port scan a resource
Upwind leverages runtime data to rapidly identify unusual port scanning and immediately alert you to suspicious activity. Read more about port scanning detections in the Upwind Documentation Center.