
We recently announced the release of Upwind’s Identity Security, designed to provide real-time protection for human and non-human identities with a comprehensive Cloud Identity Entitlement Management (CIEM) offering.
In this blog post, we will dive deeper into Upwind’s protection for non-human identities (NHI), which provide machine-to-machine access and authentication within your software environment and cloud infrastructure environment. This capability not only helps you to identify and resolve excessive permissions and risky configurations, but also gives you the ability to maintain robust identity security across all cloud platforms.
What are Non-Human Identities (NHI)?
Non-human identities refers to all identities that are associated with non-human entities, including IAM roles, IAM users, machine identities and Kubernetes Service Accounts. Non-human identities are crucial for controlling how cloud resources, such as EC2 instances and EKS nodes, can act on behalf of other entities via cross-account and execution roles. Management of non-human identities and their associated privileges is crucial for organizational security, and doing this properly requires deep, real-time context into identity behaviors, permissions and usage.
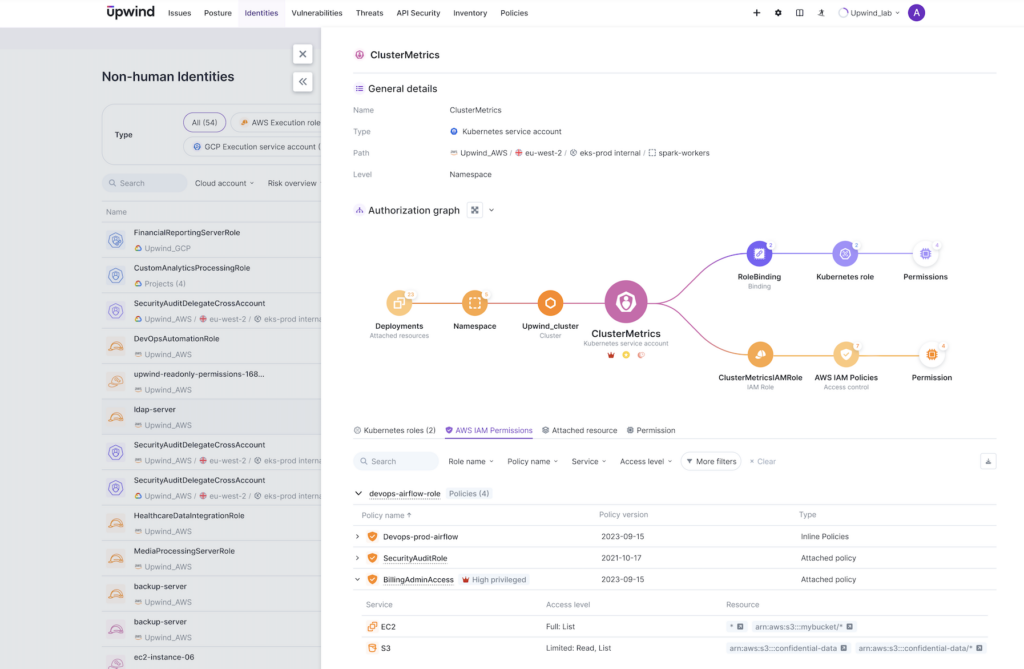
Many organizations find it difficult to monitor “who has access to what,” particularly as their operations grow. Managing non-human identities can be even more complex and challenging than human identities, as there are often thousands of non-human identities across multiple cloud environments. To solve this issue, Upwind provides enhanced visibility and control over all your cloud identities, giving users a way to simplify the complex landscape of both human and non-human identity management, which can often pose significant security risks if not managed properly with appropriate provisioning and permissioning.
How Upwind Protects Non-Human Identities (NHI)
Upwind Identity Security provides a centralized platform where all human and non-human identity service accounts and their specific permissions for associated cloud resources are visible in a single, intuitive tab. This capability, combined with human identities, not only simplifies but also enhances the management of identities, access rights, and entitlements across all cloud-based resources, streamlining the process and ensuring clear visibility and control.
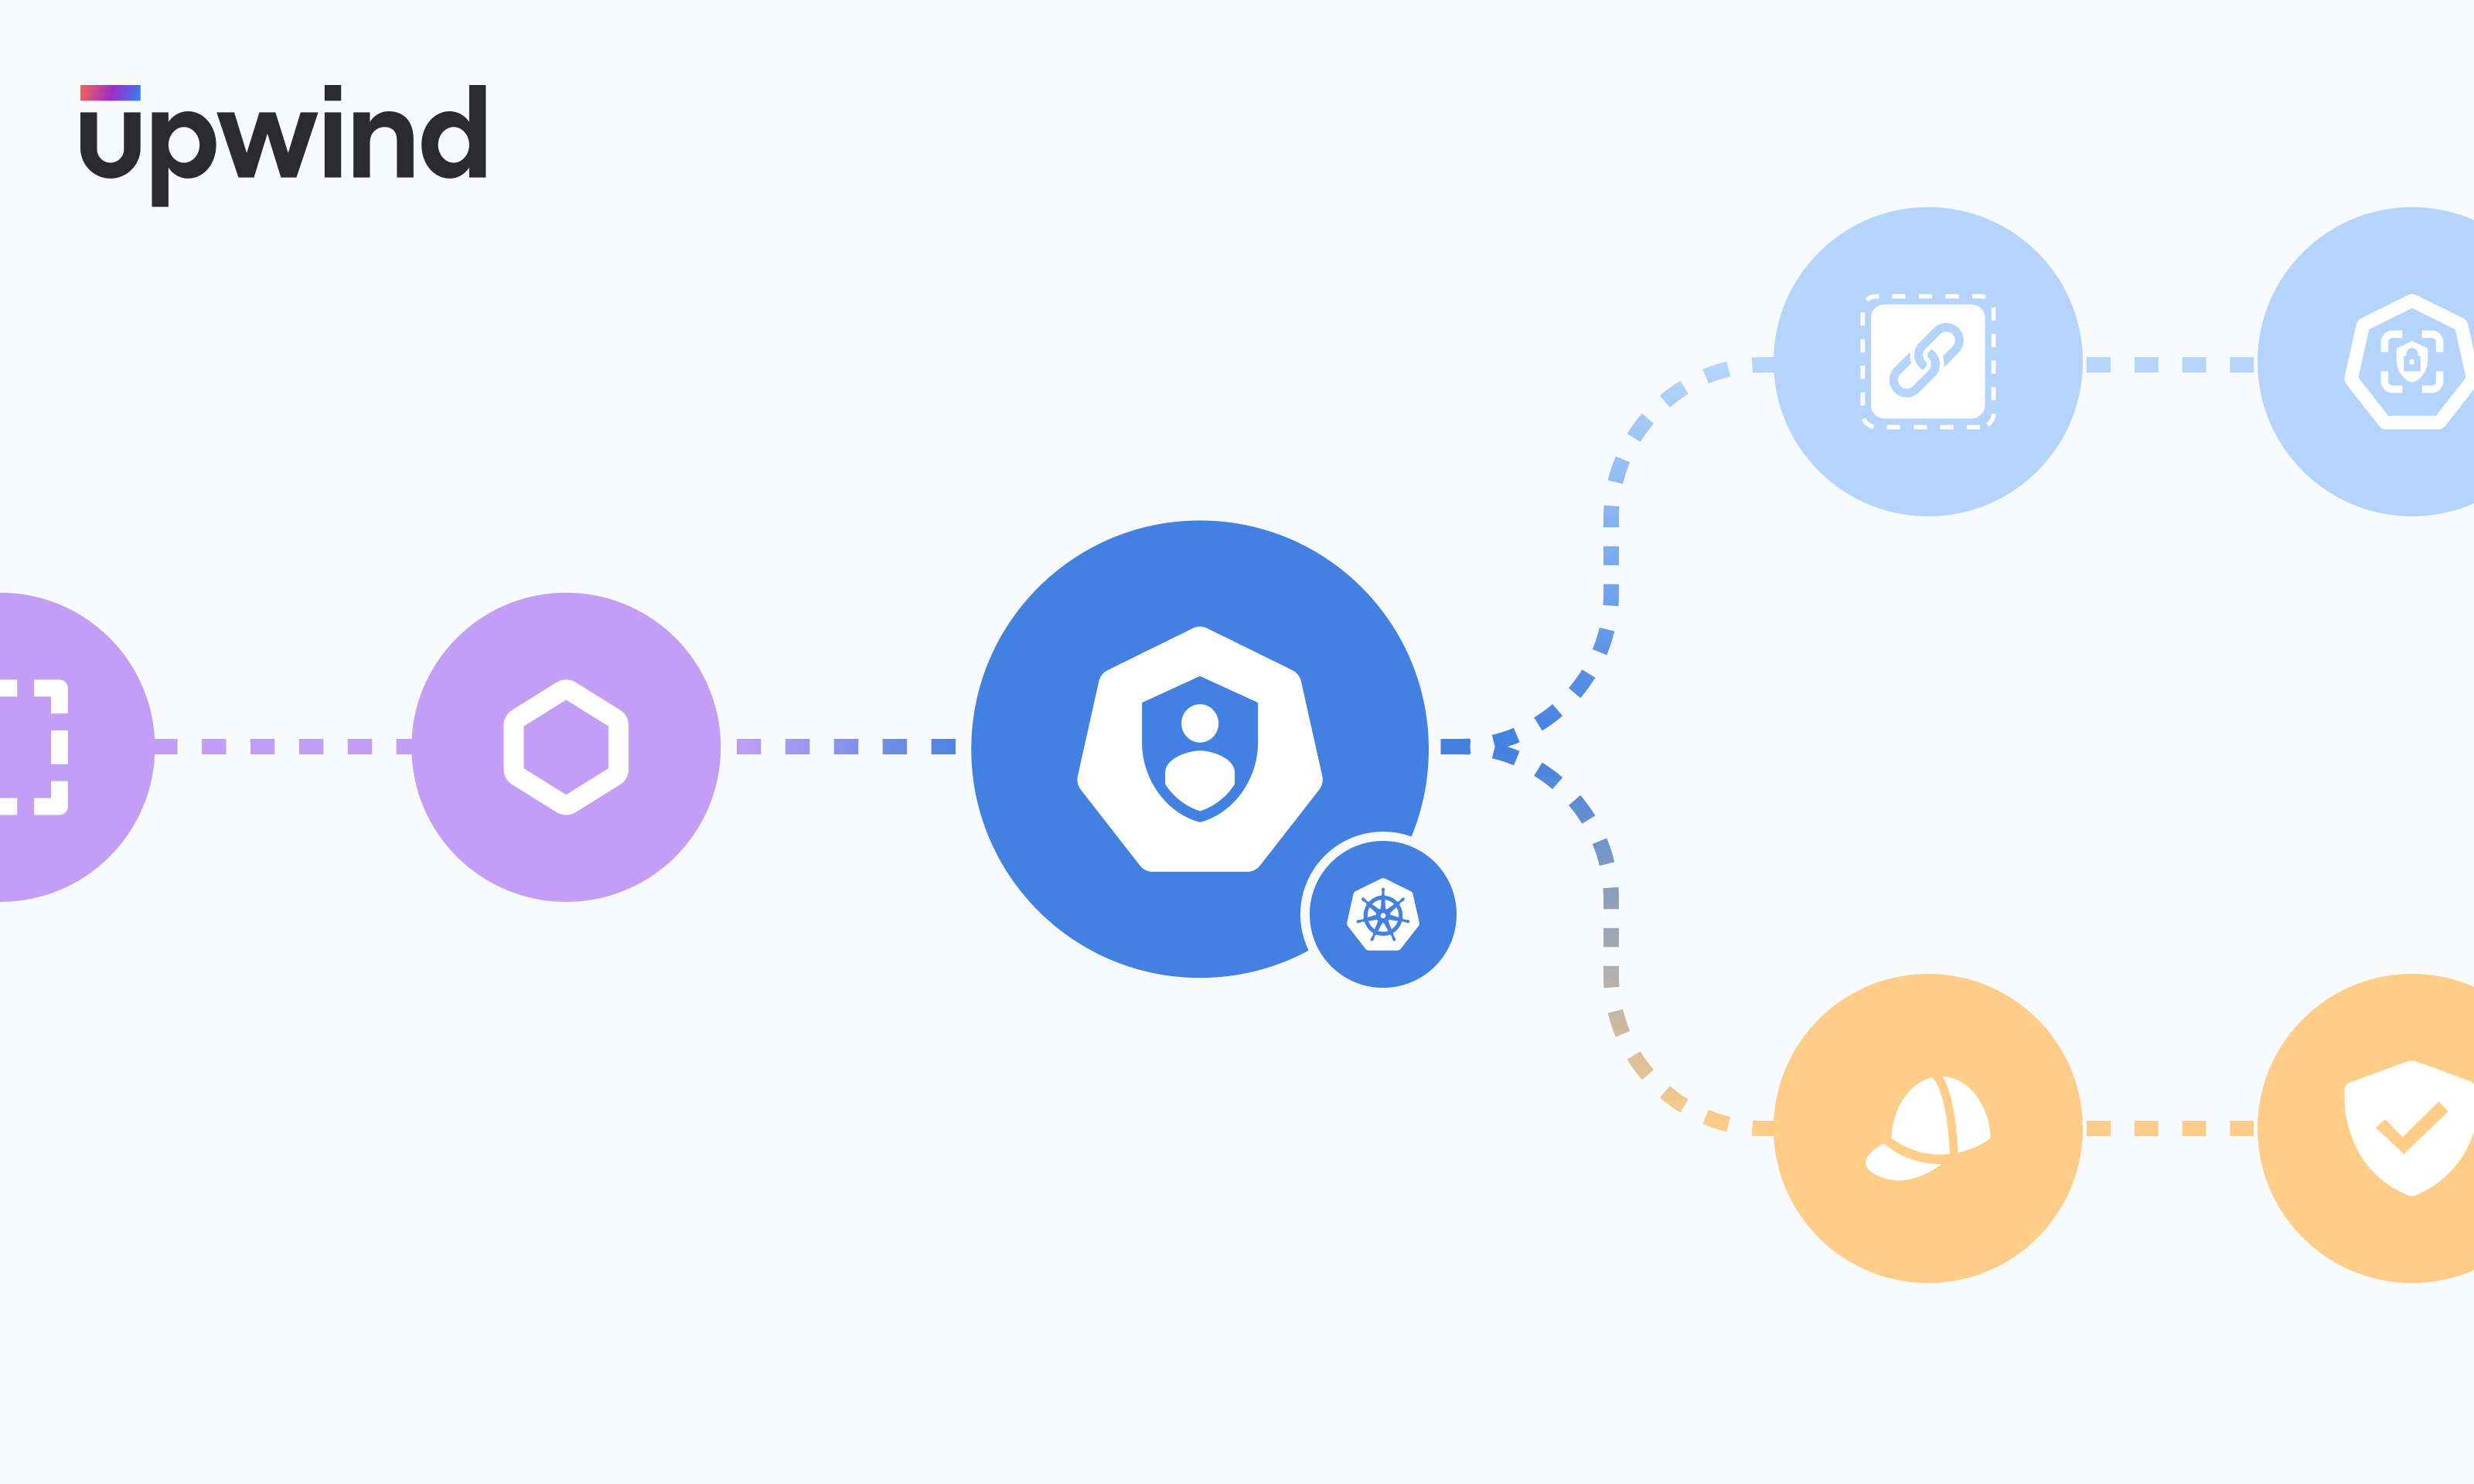
What makes this capability unique and especially valuable is our authorization graph-based approach, offering a comprehensive view and answering all the expected questions, such as “who has access to what?”.
In the “Non-Human Identities” section of Upwind Identity Security, you can view and manage the permissions associated with non-human role types, such as:
- Execution Roles: View execution roles that grant permissions to cloud services such as AWS EC2 and AWS Lambda, to perform actions on behalf of a user or another service. This consists of permissions defined by IAM policies and a trust policy specifying which entity is allowed to assume the role. This allows services to securely access resources without needing permanent credentials.
- Kubernetes Service Accounts: View all Kubernetes resources associated with service accounts, as well as relevant Kubernetes permissions within the cluster and the IAM permissions on AWS resources.
- Cross-Account Role: View IAM roles that enable an IAM user or AWS service in one AWS account to access resources in another AWS account.
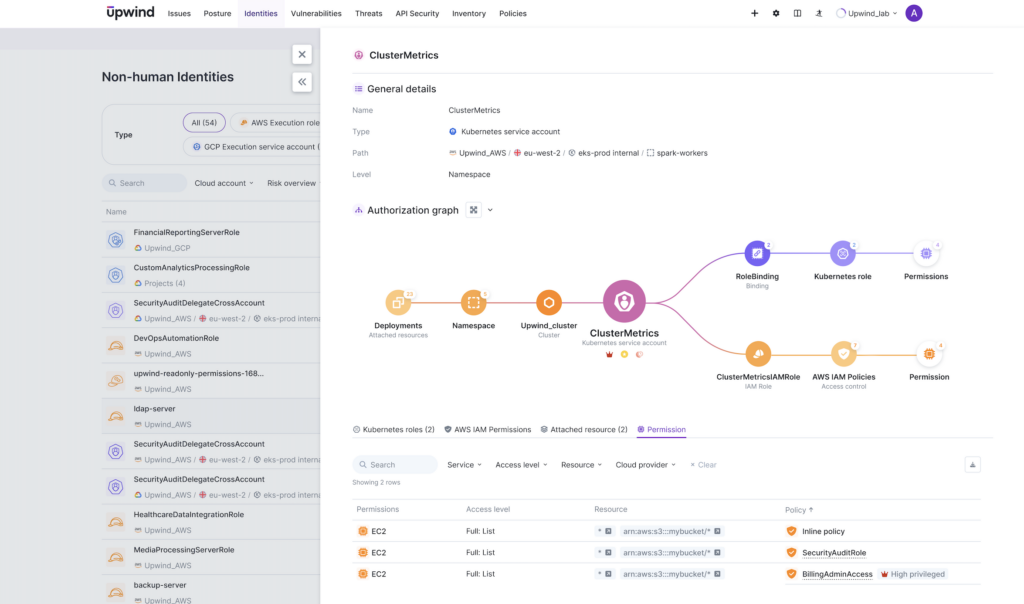
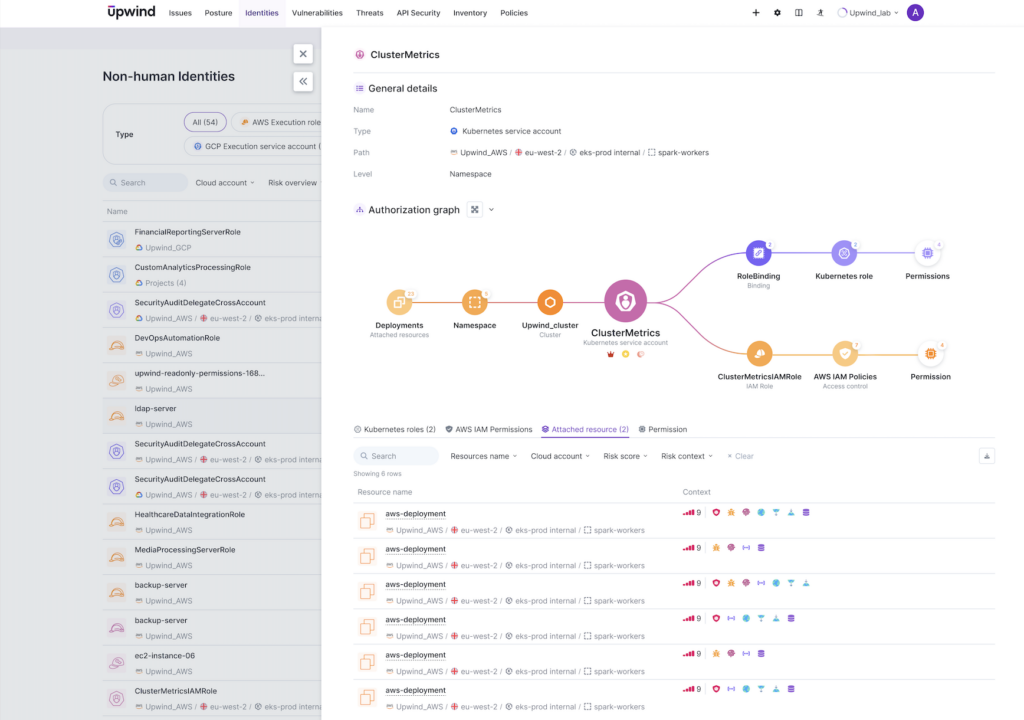
Upwind’s Non-Human Identities management also makes it easy to quickly view relevant role information for each non-human user, including:
- General Details: the non-human user’s role name, account, and time of creation.
- Authorization Graph: who can assume a role and what permissions they will have on which resources.
- Trusted Entities: a list of the entities that are trusted to assume a particular IAM role.
- IAM Permissions: role permissions divided into policies.
- Resources Using Current Role: a list of all the resources that use this role.
- Kubernetes Permissions: specific permissions for a Kubernetes service account
- Kubernetes Resources: all Kubernetes resources using a Kubernetes service account
- High Privilege: indicates high privilege on a permission policy.
Upwind’s Non-Human Identity capabilities provide you with comprehensive visibility into all organizational identities and their associated permissions across both Kubernetes and Cloud Provider environments. This unified view enables effective access management from one accessible location, reducing the risk of unauthorized breaches.
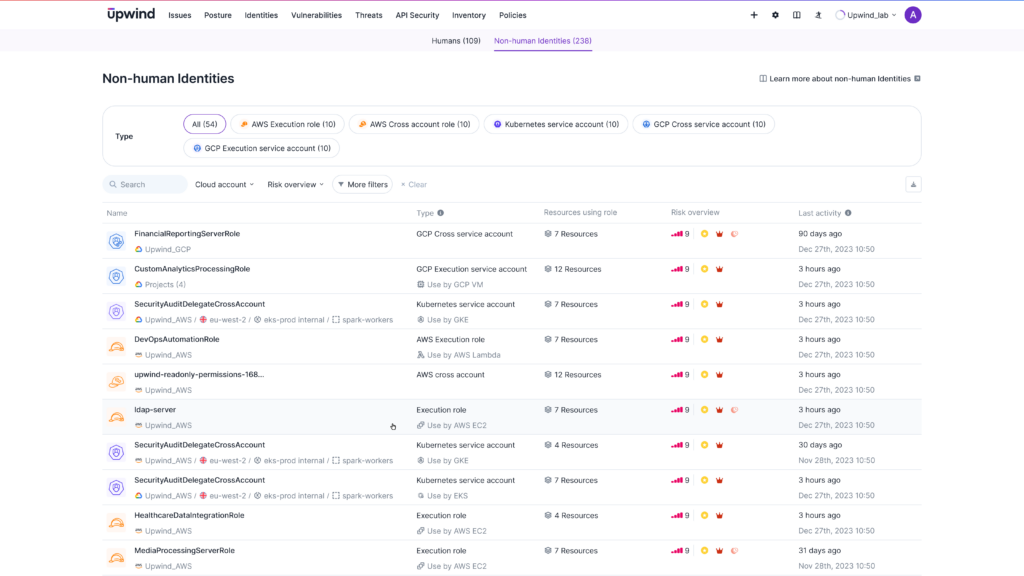
In addition, this deep visibility and context also provides valuable insights into the attack landscape, highlighting vulnerabilities when specific service roles are compromised. Armed with this knowledge, you can proactively address vulnerabilities and strengthen identity security posture.
How Upwind Identity Security Strengthens Your Cloud Security
Upwind Identity Security’s Non-Human Identity capabilities provide you with real-time non-human identity context and visibility, providing a streamlined understanding of “who has access to what.” By integrating Identity Security into the Upwind Cloud Security Platform, Upwind gives you the ability to understand how both human and non-human identities interact with your overall cloud environment and proactively address identity-related vulnerabilities and threats.
Use Upwind Identity Security’s non-human identity capabilities for a holistic view of access control across your entire infrastructure, strengthening your overall cloud security.
Learn More
For more information on Upwind Identity Security and non-human user management, visit the Upwind Documentation Center (login required), or request a demo.