Blog
Upwind Blog
Feed
Grid
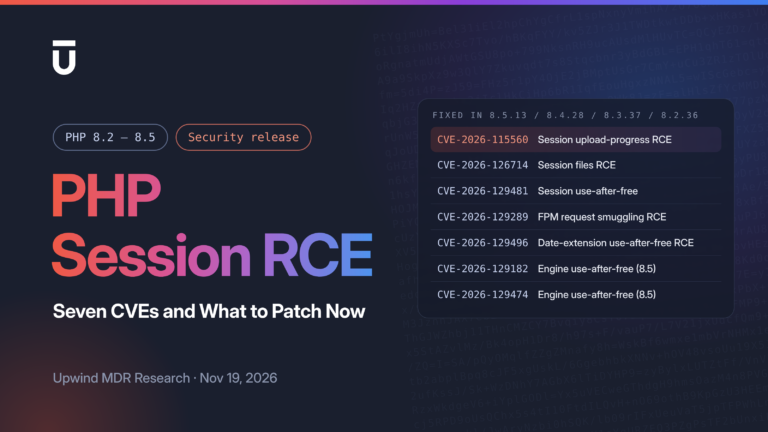
PHP Critical Vulnerabilities: Affected Versions and Mitigations
PHP fixed seven Critical vulnerabilities in today's security releases, across session handling, the engine, the date extension, and PHP-FPM. What we found: the most direct route to code execution is the PHP-FPM request smuggling bug, not the session bug that drew attention in October. The session serializer bug is far broader than October's advisory suggested,…
Remote Code Execution in NGINX HTTP/2: CVE-2026-123007 and CVE-2026-123633
F5 shipped fixes on 18 November 2026 for two HTTP/2 remote code execution flaws in NGINX, CVE-2026-123007 and CVE-2026-123633. What we found: the serious one is real but expensive, about 128 GB on a single connection to reach code execution, and the most exposed deployments are community ingress-nginx clusters, which have HTTP/2 on by default…
Upwind Now Follows Every Container Image From Pull Request to Runtime

Upwind now scans the container images in your cloud registries and follows every image from the pull request that changed it to the workloads running it. You catch risky images before they ship, and because Upwind also sees runtime, you know which of the running ones matter. Key takeaways When an agent's pull request adds…
Java4Shell: What We Know Now and What Comes Next
Update: OpenJDK, Oracle, and Calif have now published. This post reflects the official advisories, Calif's full write-up, and our own lab results. Java4Shell (CVE-2026-114938) is a heap out-of-bounds write in OpenJDK's hardware-accelerated Base64 decoder. It leaked before its patch, and it is now confirmed by OpenJDK and fixed in Oracle's 17 November builds. Calif's write-up…
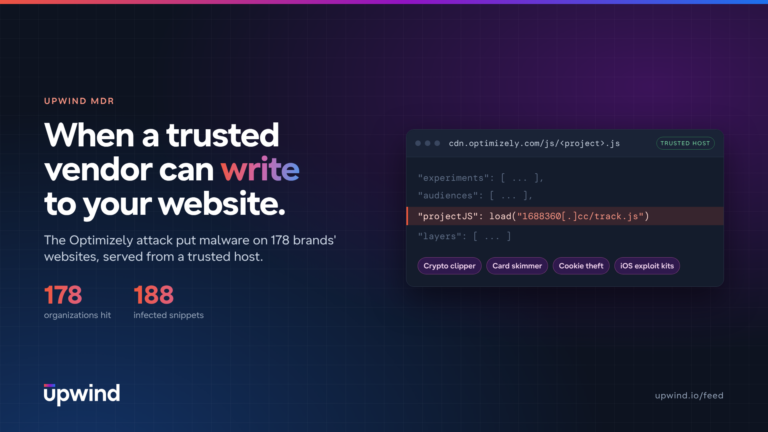
The Optimizely Attack: When a Trusted Vendor Can Write to Your Website
On 16 November 2026, malicious JavaScript was served to visitors of 178 organisations through Optimizely Web, including Zoom, the BBC, CNN, Salesforce, GitLab and HSBC. What we found: nobody hacked a CDN, the attacker only needed write access to customer projects, and that is exactly why trusting the vendor's domain protected no one. TL;DR The…
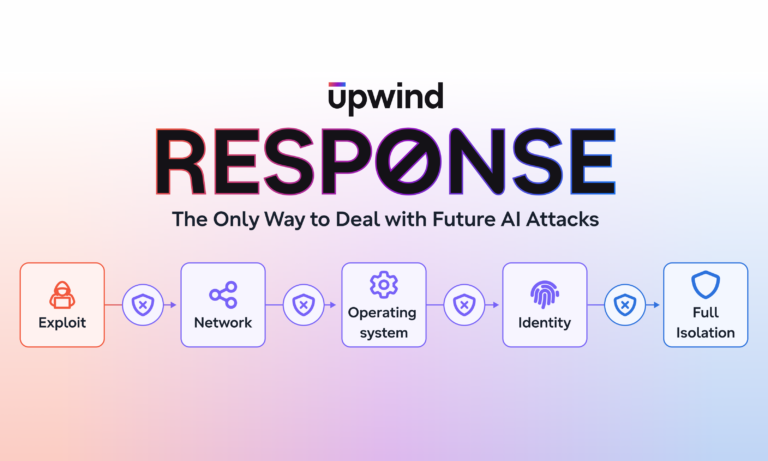
Exploits Now Arrive in Hours, So Upwind Stops the Attacker While Your Service Stays Up

In the past year, my team and I have dealt with hundreds of incidents, more than in any year before. I no longer think detection alone can protect a company. So we built Upwind Response to contain an attacker in your cloud in near real time, without disrupting your services. Key Takeaways Anyone with an…
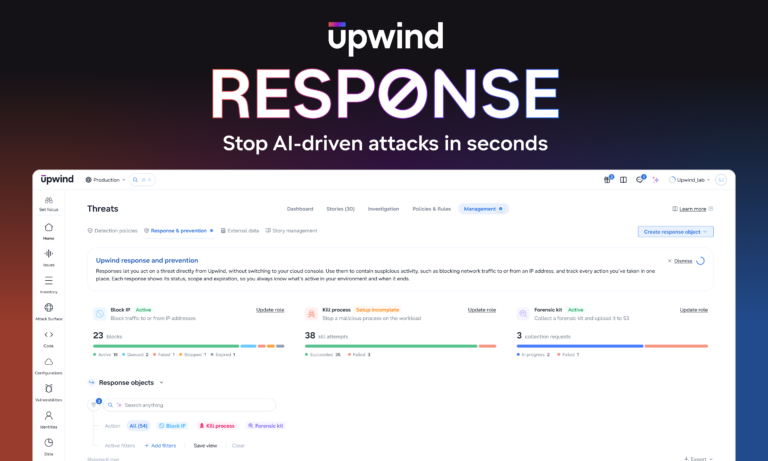
Introducing Upwind Response – The Next Wave in Cloud & AI Security

The CVE Tsunami is here, Vulnpocalypse if you will. In recent weeks, enterprises around the world have suffered real breaches. Our MDR heroes have spent weekends, days and nights with customers helping them to detect fast and contain their attacks. We came to a realization that detection, even the fastest detection, is no longer enough.…
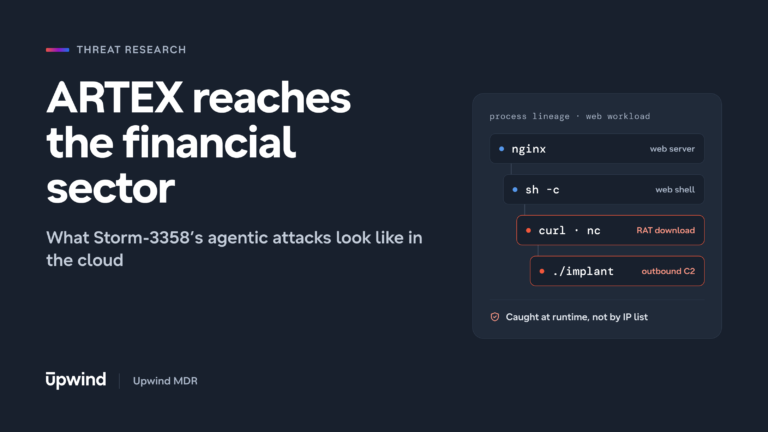
ARTEX Reaches the Financial Sector: What Storm-3358’s Agentic Attacks Look Like in the Cloud
A financially motivated actor that Microsoft tracks as Storm-3358 is now running the ARTEX agentic attack framework against banks and other financial organizations. What we found in the public record: the techniques are not new, the tooling is noisy, and in cloud workloads the most useful signal is not an IP address but a web…
GHSA-xqc2-xf4c-x3h3: What the React Server Components Typed-Array RCE Means for Your Next.js Apps
React fixed a critical, unauthenticated remote code execution flaw in its Server Components packages on 14 October 2026 (GHSA-xqc2-xf4c-x3h3, CVSS v4 9.5). What we found: the trigger is narrow and this is not React2Shell 2.0, but the flaw is easy to miss because it has no CVE, it hides in a copy of React that…
sshole: Alpine/musl OpenSSH accepts any 257+ character password
OpenSSH 10.6p2, released on 5 November 2026, works around a password bypass in sshd on Linux systems that use musl libc without PAM, with Alpine as the main case. What we found: the package count badly overstates exposure, the deciding question is whether a musl sshd is actually running, and some of the conditions that…
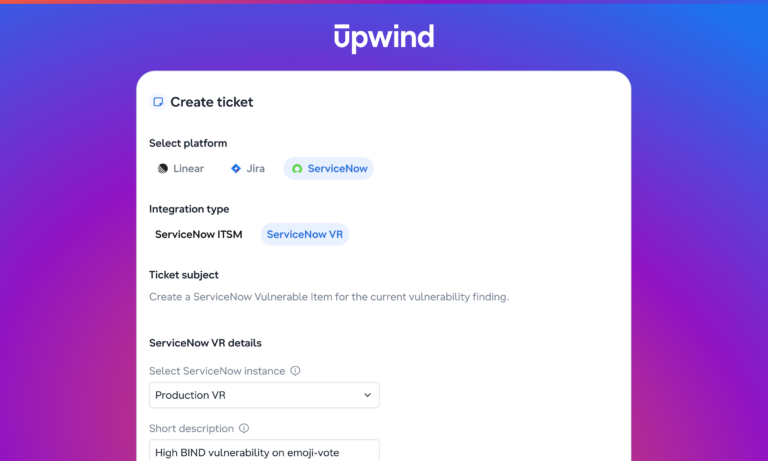
Upwind + ServiceNow VR: Only real findings reach the ticket queue

Send vulnerability findings straight into your VR queues, and let Upwind verify every fix before a ticket stays closed. Key Takeaways Upwind now integrates with ServiceNow Vulnerability Response (VR), the ServiceNow module where remediation teams track and fix vulnerabilities. The integration is generally available. It sends Upwind findings into VR as native Vulnerable Items and…
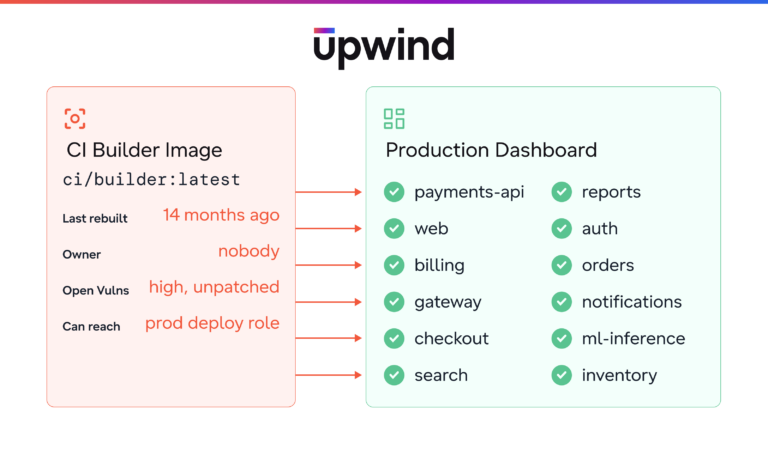
Your CI Runner Image Can Deploy to Prod. Who’s Scanning It?
How to find, rank, and trace the most privileged containers in your cloud before an attacker does Key Takeaways Every recent supply-chain attacks hit the build path Someone reports a compromise in a popular CI dependency, and security asks one question in the incident channel: "Are we affected?" Production dashboards are green, runtime alerts are…
The Next Wave Is Here: Upwind’s $400M Series C to Build The Cloud & AI Security Platform
Today, we are marking an important milestone in our incredible journey. Less than 9 months since we announced our $250M Series B, we are thrilled to announce our $400M Series C funding led by Bessemer Venture Partners with participation from each and every Upwind's investor: Greylock Partners, Cyberstarts, Craft, Salesforce Ventures, Alta Park, Picture Capital,…
Latest
November 19, 2026
PHP Critical Vulnerabilities: Affected Versions and Mitigations
PHP fixed seven Critical vulnerabilities in today's security releases, across session handling, the engine, the date extension, and PHP-FPM. What we found: the most direct route to code execution is the PHP-FPM request smuggling bug, not the session bug that drew attention in October. The session serializer bug is far broader than October's advisory suggested,…
November 18, 2026
Remote Code Execution in NGINX HTTP/2: CVE-2026-123007 and CVE-2026-123633
F5 shipped fixes on 18 November 2026 for two HTTP/2 remote code execution flaws in NGINX, CVE-2026-123007 and CVE-2026-123633. What we found: the serious one is real but expensive, about 128 GB on a single connection to reach code execution, and the most exposed deployments are community ingress-nginx clusters, which have HTTP/2 on by default…
November 18, 2026
Upwind Now Follows Every Container Image From Pull Request to Runtime
Upwind now scans the container images in your cloud registries and follows every image from the pull request that changed it to the workloads running it. You catch risky images before they ship, and because Upwind also sees runtime, you know which of the running ones matter. Key takeaways When an agent's pull request adds…
November 17, 2026
Java4Shell: What We Know Now and What Comes Next
Update: OpenJDK, Oracle, and Calif have now published. This post reflects the official advisories, Calif's full write-up, and our own lab results. Java4Shell (CVE-2026-114938) is a heap out-of-bounds write in OpenJDK's hardware-accelerated Base64 decoder. It leaked before its patch, and it is now confirmed by OpenJDK and fixed in Oracle's 17 November builds. Calif's write-up…
November 17, 2026
The Optimizely Attack: When a Trusted Vendor Can Write to Your Website
On 16 November 2026, malicious JavaScript was served to visitors of 178 organisations through Optimizely Web, including Zoom, the BBC, CNN, Salesforce, GitLab and HSBC. What we found: nobody hacked a CDN, the attacker only needed write access to customer projects, and that is exactly why trusting the vendor's domain protected no one. TL;DR The…
November 16, 2026
Exploits Now Arrive in Hours, So Upwind Stops the Attacker While Your Service Stays Up
In the past year, my team and I have dealt with hundreds of incidents, more than in any year before. I no longer think detection alone can protect a company. So we built Upwind Response to contain an attacker in your cloud in near real time, without disrupting your services. Key Takeaways Anyone with an…
November 12, 2026
Introducing Upwind Response – The Next Wave in Cloud & AI Security
The CVE Tsunami is here, Vulnpocalypse if you will. In recent weeks, enterprises around the world have suffered real breaches. Our MDR heroes have spent weekends, days and nights with customers helping them to detect fast and contain their attacks. We came to a realization that detection, even the fastest detection, is no longer enough.…
November 8, 2026
ARTEX Reaches the Financial Sector: What Storm-3358’s Agentic Attacks Look Like in the Cloud
A financially motivated actor that Microsoft tracks as Storm-3358 is now running the ARTEX agentic attack framework against banks and other financial organizations. What we found in the public record: the techniques are not new, the tooling is noisy, and in cloud workloads the most useful signal is not an IP address but a web…
November 8, 2026
GHSA-xqc2-xf4c-x3h3: What the React Server Components Typed-Array RCE Means for Your Next.js Apps
React fixed a critical, unauthenticated remote code execution flaw in its Server Components packages on 14 October 2026 (GHSA-xqc2-xf4c-x3h3, CVSS v4 9.5). What we found: the trigger is narrow and this is not React2Shell 2.0, but the flaw is easy to miss because it has no CVE, it hides in a copy of React that…
November 5, 2026
sshole: Alpine/musl OpenSSH accepts any 257+ character password
OpenSSH 10.6p2, released on 5 November 2026, works around a password bypass in sshd on Linux systems that use musl libc without PAM, with Alpine as the main case. What we found: the package count badly overstates exposure, the deciding question is whether a musl sshd is actually running, and some of the conditions that…
November 4, 2026
Upwind + ServiceNow VR: Only real findings reach the ticket queue
Send vulnerability findings straight into your VR queues, and let Upwind verify every fix before a ticket stays closed. Key Takeaways Upwind now integrates with ServiceNow Vulnerability Response (VR), the ServiceNow module where remediation teams track and fix vulnerabilities. The integration is generally available. It sends Upwind findings into VR as native Vulnerable Items and…
November 3, 2026
Your CI Runner Image Can Deploy to Prod. Who’s Scanning It?
How to find, rank, and trace the most privileged containers in your cloud before an attacker does Key Takeaways Every recent supply-chain attacks hit the build path Someone reports a compromise in a popular CI dependency, and security asks one question in the incident channel: "Are we affected?" Production dashboards are green, runtime alerts are…