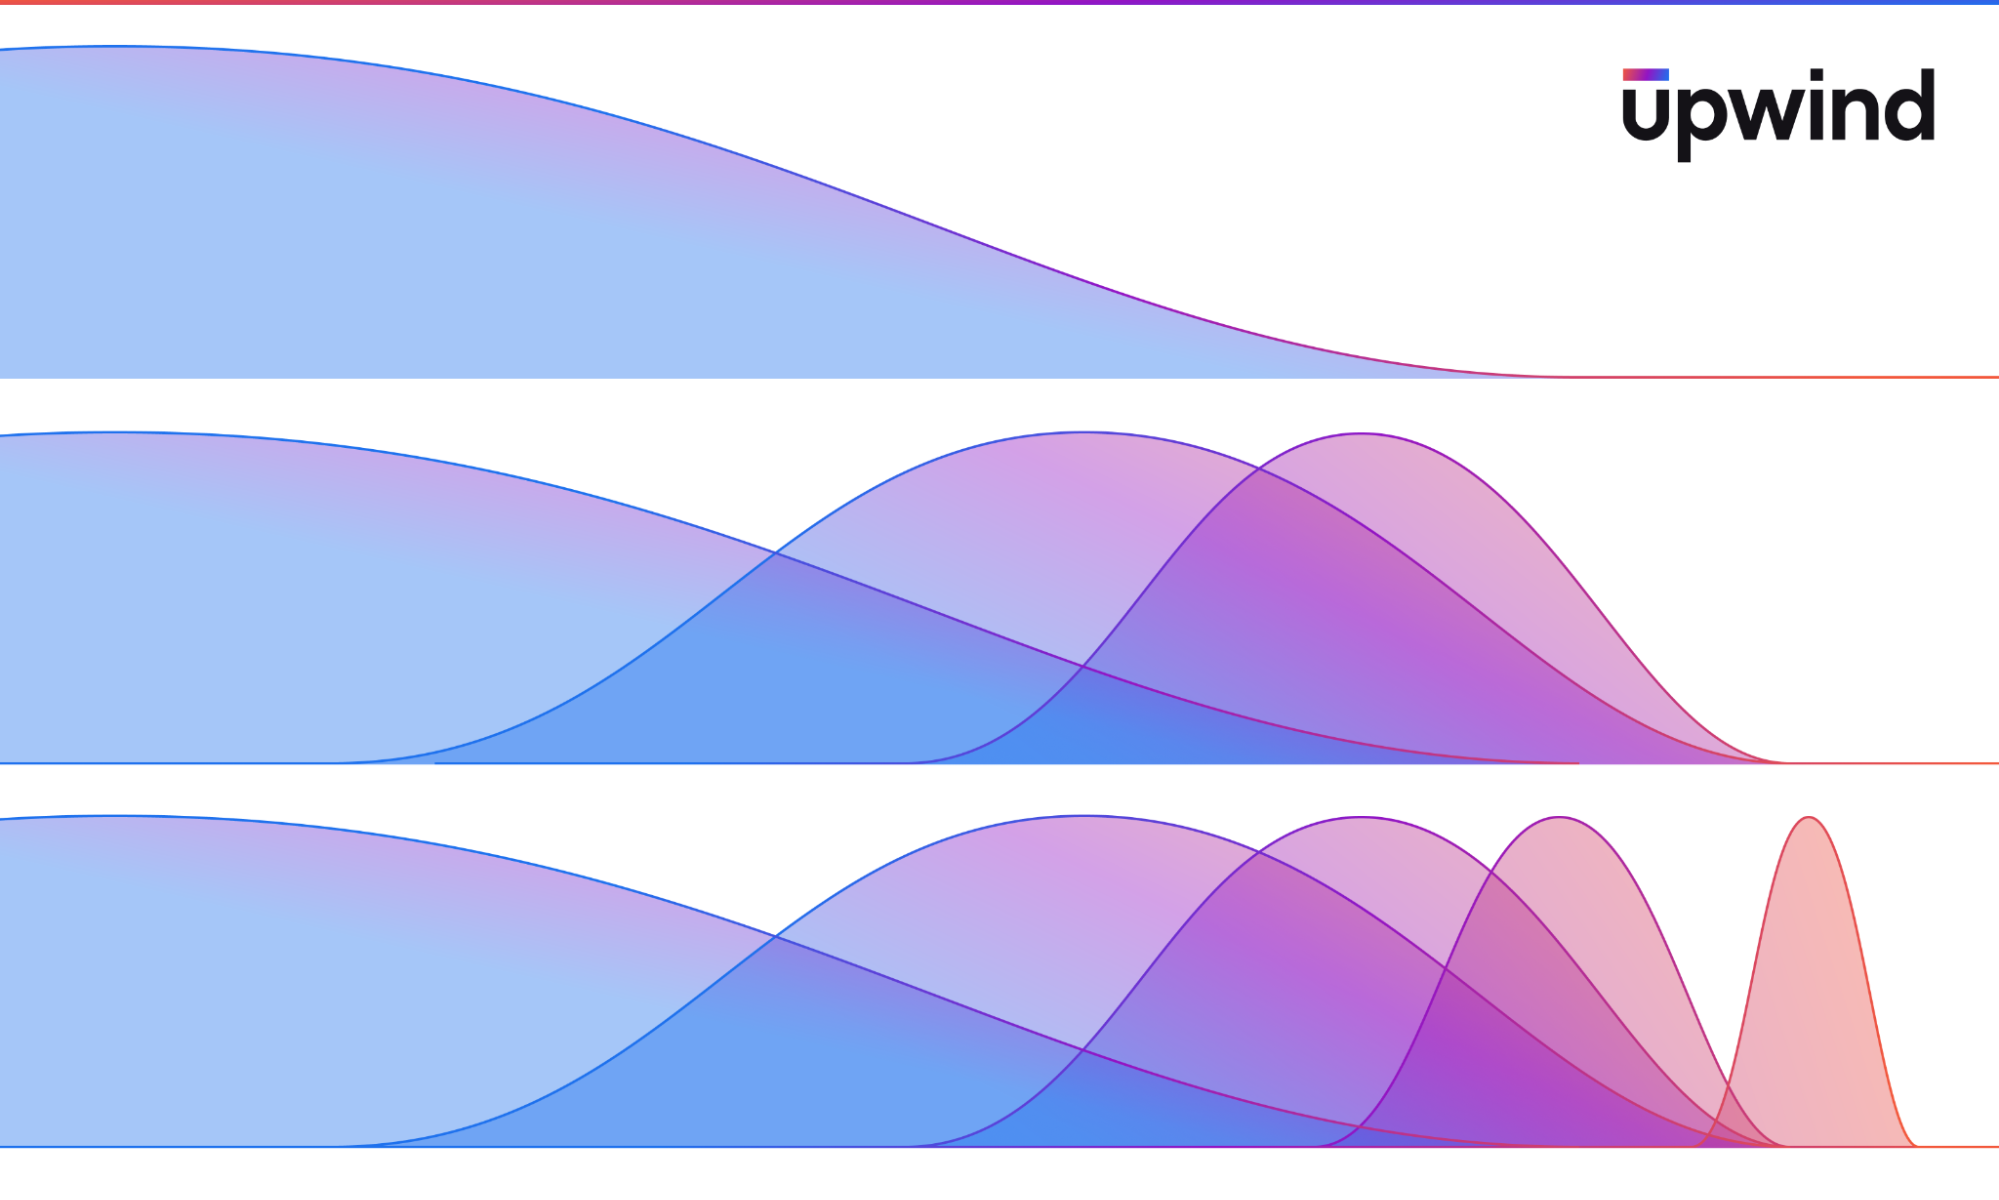

Back to school season is here, which makes this a good moment to look at what changed in the threat landscape over the summer. AI-assisted attackers haven’t climbed toward the top of the field so much as filled in the middle of it and the middle is the population almost no security program was designed against. Most programs are built for two tails, with preventive hygiene stopping the low-skill bottom while threat intelligence and incident response handle the well-resourced top. Those two tails haven’t changed much this year, but what sits between them has.
Why I think the class average moved
Threat populations have always been bimodal. At one end sits volume: opportunistic scanning, credential stuffing, commodity ransomware affiliates working from playbooks they didn’t write and can’t modify. At the other end sits a small number of operators with budget, patience and original tooling. Between those two groups, historically, there wasn’t much. Becoming competent at intrusion took years of failed attempts, forum lurking, mentorship you had to earn and a high tolerance for tools that broke without explanation.
Security programs mirror that shape whether or not anyone planned it that way. Preventive controls, patching cadence, posture management and baseline hardening handle the bottom, because volume attacks fail against hygiene by design. Threat intelligence, detection engineering, IR retainers and tabletop exercises handle the top, because well-resourced actors leave documented tradecraft you can build detections around. The middle never needed a program of its own for the straightforward reason that there wasn’t much middle to program against.
AI collapses the apprenticeship by handing over its slowest part, which is troubleshooting. When a technique failed, a less-experienced attacker used to stall out entirely, because the error message meant nothing and nobody was around to explain it. Now they paste the error and receive a plausible next step. Multiply that across every failure point in a chain and the time to competence compresses from years into months.
I built these five predictions from watching what attackers do rather than from what anyone says is coming. Nobody runs a census on attacker skill so treat this as a read and not a measurement.
1. AI accelerates attackers long before it replaces security teams
A force multiplier does nothing for a force of zero, which is why the acceleration lands unevenly.
AI is most effective right now at researching targets, finding exposed assets, adapting phishing campaigns to a specific company’s language, generating code and automating the repetitive steps that used to eat an operator’s week. Humans still choose targets and set objectives. What rises sharply is the machine-to-human ratio inside the attack itself and that ratio doesn’t rise at the same rate everywhere.
Operators at the top automated years ago. They wrote their own tooling, built their own infrastructure and solved their own repetitive-work problem long before a model could do it for them. A model saves them a moderate amount of time on work they’d already handled. The attacker who never had tooling now has something close to it. That’s where the ratio moves fastest and it happens to be the same place the population is growing.
Before anyone reads this as a doom argument, the same acceleration is available to defenders. The uncomfortable part is permission rather than capability. Adopting an autonomous capability on the defensive side requires approval, audit trails and blast-radius review. An attacker running the same class of tooling answers to nobody.
2. The skill floor rose while the ceiling stayed where it was
No model will turn a novice into an elite operator this year. I know how that sounds coming from a vendor blog so let me be more precise.
What AI does for a less-experienced attacker is help them move faster, recover from failures that would previously have ended the attempt and combine techniques they couldn’t previously chain together. The result is greater attack volume, faster iteration between attempts and social engineering that reads as though someone who works at your company wrote it. None of that requires elite skill. All of it requires the kind of workmanlike competence that used to take years and now takes a productive afternoon.
The consequence sits in your detection tuning. Every threshold, every suppression rule and every “this is probably noise” judgment encodes an assumption about the population generating the traffic. Your environment was probably tuned on the premise that an attack is either obvious enough for hygiene to stop or distinctive enough for intel to name. The middle is neither obvious nor distinctive so it passes through the seam between those two assumptions. That seam was narrow when the middle was thin. It’s wider now.
The tell I look for is an attempt chain that shows persistence without polish. Someone tries a technique, fails in a way that would have stopped them a year ago, adjusts within minutes and tries a variant that’s close but not identical. That pattern used to indicate a skilled operator working from experience. Now it indicates somebody with a model open in another window.
3. Identity and permissions become the leading AI-related cloud risk
Identity abuse rewards competence over sophistication, which is exactly why the new middle goes there first.
AI agents need access to data, tools, APIs and infrastructure to do anything worth deploying them for. Excessive permissions, exposed credentials and poorly governed service identities turn what looks like a minor mistake into a path toward a serious cloud compromise. An attacker or a manipulated agent reaches a role, reads what the role can touch, moves to the next one and repeats until something interesting appears.
Notice what that path doesn’t require. No zero day, no custom implant, no evasion research and no original tooling. It requires reading permission policies carefully, understanding what a role can reach transitively and having the patience to follow the chain. Those are competence problems and competence is the thing that became abundant this year.
Published ratios of non-human to human identities this year run anywhere from 45 to 1 up to 144 to 1 depending on who did the counting and what they counted as an identity. When credible estimates of the same quantity vary by a factor of three, nobody has a reliable inventory, which means an attacker patiently enumerating your roles ends up holding better data about your identity surface than you do.
Most organizations still review service account permissions the way schools review a fire evacuation plan, which is to say annually and on paper. The permission set that was reasonable when the account was created has drifted for eighteen months and the drift is almost always additive because nobody removes a permission that might be load-bearing.
4. Prompt injection stops being a model problem and becomes a system problem
Prompt injection is a confused deputy problem and we’ve solved that class of problem before.
A confused deputy is a program with legitimate privileges that someone without those privileges tricks into acting for them. Cross-site request forgery works exactly this way, and so does a large share of server-side request forgery. The pattern is old enough that the industry has a settled answer for how it ends, which makes it useful for predicting where AI security goes next.
The risk worth planning around is manipulation of an AI system into disclosing data or misusing the tools and privileges attached to it. Making a model produce an inappropriate sentence is nothing more than the demo version. As agents take on more autonomy and reach more tools, the interesting question stops being what the model says and becomes what the system does with the credentials it holds while the model is confused about who it’s serving.
This is where I’d bet against the current default response. Filtering-first defenses against prompt injection are the WAF answer to SQL injection. That approach bought the industry a decade of partial coverage and it never solved the problem, because you can’t reliably separate instruction from data by inspecting the data. What solved SQL injection was parameterization, which is an architectural boundary rather than a smarter filter. Expect the same arc here, with the durable controls turning out to be authorization boundaries around what an agent can invoke, isolation between untrusted input and privileged context, monitoring of what the agent does rather than what it reads and human approval gates on high-impact actions. We walked through how that chain runs in practice in an earlier piece on multi-step AI attack chains.
5. Runtime security becomes a default rather than an add-on
A larger competent middle breaks preventive-only security for two reasons that have nothing to do with each other, which is what makes it hard to patch around.
The first reason is speed. A misconfiguration that would have sat unexploited for months because nobody had bothered to look now surfaces in days, since looking became cheap. Preventive review cycles were calibrated against how long it used to take an attacker to find things. That calibration is stale and quarterly review against a threat that iterates weekly is a losing arithmetic problem no matter how good the reviewers are.
The second reason is attribution. The middle doesn’t produce named actors, TTP writeups or IOC feeds, because a few thousand moderately competent people working independently don’t form a group anyone bothers to name. Intel-driven detection has nothing to key on. You can’t build a detection around tradecraft that nobody has documented and nobody documents tradecraft that isn’t distinctive.
What the middle can’t avoid is running. Every attack that matters eventually executes something on your infrastructure, reaches for a credential, calls an API or moves data somewhere it shouldn’t go. All of that is observable regardless of how the attacker learned to do it. Runtime behavior carries no information about the attacker’s skill level and it doesn’t need to. That property is the whole argument for making runtime a default, because it’s the one layer whose effectiveness doesn’t degrade as the population shifts.
In practice that means two things worth naming. AI-NHI maps which non-human identities exist and what each one can reach, which turns permission review from an annual paper exercise into a live picture you can act on. AI-DR correlates runtime signals so that anomalous behavior surfaces as a detection while it’s still happening rather than in a postmortem. Preventive controls remain necessary and none of this replaces them. The argument is about what happens in the window between a mistake existing and someone finding it and AI compressed that window considerably.
Grading your program against the new curve
Every control you own was tuned against a threat population whether or not anyone wrote the assumption down. That’s the piece worth revisiting before the year runs away from you.
The permission audit is the highest-value place to start and the useful version asks what each role can reach transitively rather than what it was granted on paper. Agent tool access deserves the same treatment as a privilege boundary rather than a configuration detail, because an agent with a broad token is a standing offer to anyone who can confuse it. And the misconfiguration you haven’t found yet will be found faster this year than last, which argues for shortening the distance between something going wrong and someone noticing rather than for adding another preventive layer on top of the ones that already exist.
None of these five predictions needs an elite adversary, which is what makes them worth planning around. Most security programs are ready for the students who fail and the ones who set the curve. The problem this year is everyone in between.
Key Takeaways
- AI raises the attacker skill floor without moving the ceiling, which fills in a previously thin middle of the threat population.
- Most security programs are built for two tails, with hygiene handling low-skill volume and threat intelligence handling well-resourced actors, leaving the middle unaddressed.
- Identity and permissions become the leading AI-related cloud risk, because identity abuse rewards patient competence rather than novel exploitation.
- Prompt injection is a confused deputy problem and input filtering will fail against it the same way it failed against SQL injection.
- Runtime security becomes a default because runtime behavior is observable regardless of attacker skill, which is not true of preventive or intelligence-driven controls.