Blog
Upwind Blog
Feed
Grid
Upwind Researcher Spotlight: Dan Gansel

"You have to map the core logic and syntax of the system before you can find the interesting primitives." This June 1st, Dan Gansel will walk on stage at fwd:cloudsec 2026 in North America to demonstrate a fully functional command-and-control channel that operates inside the AWS Data Perimeter, the cloud-native gold standard for keeping sensitive…
Scale AI Adoption Securely With Upwind AI Security


AI is entering production faster than many security teams can keep up. As teams embed AI into applications, developer workflows, and cloud operations, security teams need to know where AI runs, what it can access, and which risks need action. Upwind AI Security connects AI usage to realtime cloud context, giving teams a practical way…
Refuse the Seat: Why Modern CISO Leadership Advice Is Failing the Profession

Key Takeaways The single most repeated piece of advice in security leadership is also the one doing the most damage to the profession. Earn your seat at the table. Become a business translator. Integrate into the operator class. The CISOs who follow that advice end up burned out, legally exposed, and stuck in five-jobs-in-one roles…
Upwind AI Security: Securing your AI stack from the inside-out


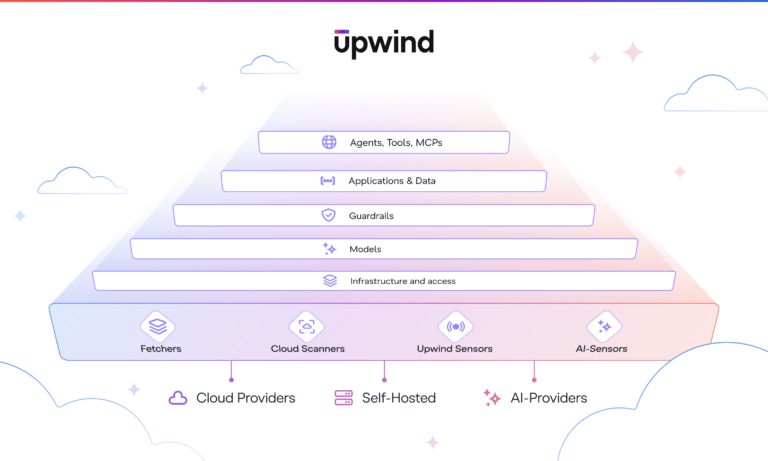
AI is changing how we build, work, and operate. It is moving from experimentation into production applications, customer experiences, developer workflows, and cloud operations. As AI moves closer to the core of the business, it is gaining access to the systems that matter most: sensitive data, internal tools, cloud services, and non-human identities. AI changed…
Newly Discovered durabletask Malware Targeted Kubernetes, Cloud Secrets, and CI/CD Infrastructure

Executive Summary Upwind identified a critical supply chain compromise involving durabletask==1.4.1, 1.4.2, and 1.4.3, three consecutive malicious releases of Microsoft's Azure Durable Task Python SDK published to PyPI. The malicious release contains a lightweight dropper embedded directly into durabletask/init.py. On import, the package downloads and executes a remote payload named rope.pyz from attacker-controlled infrastructure. The…
The New Face of Supply Chain Attacks: npm Malware Built for CI/CD and Cloud Compromise
Executive Summary Upwind is tracking an active software supply chain campaign impacting multiple npm packages commonly used across developer tooling, frontend frameworks, CI/CD pipelines, and cloud-native application environments. We identified malicious payloads designed specifically to target CI/CD systems, cloud identities, GitHub credentials, npm publishing workflows, developer machines, and AI developer tooling. The campaign includes install-time…
Validate Real Cloud Risk with Red, the Validation Agent


After teams identify the risks that matter, the next challenge is proving which ones are actually exploitable. Severity scores, exposure labels, and long lists of findings can point teams in the right direction, but they do not always show whether an attacker has a viable path to impact. In cloud environments, that path often depends…
The Supply Chain Strikes Again: Credential-Stealing Malware Hidden in node-ipc
Executive Summary On May 14, 2026, malicious versions of the widely used node-ipc npm package were published through a legitimate maintainer account, introducing a sophisticated credential-stealing payload into a package with approximately 3.35 million monthly downloads. The malicious payload was hidden inside the CommonJS bundle (node-ipc.cjs) and silently executed whenever applications loaded the package through…
Accelerate Cloud Security Investigations with Blue, the SecOps Agent
The AI threat landscape is moving faster on both sides. Attackers are using AI to scale campaigns, accelerate exploit development, and move faster from discovery to execution. Defenders need AI that helps them keep pace without adding noise or pulling teams away from the work that matters most. Prioritization helps teams focus on the risks…
The AI Threat Landscape Demands a New Cloud Security Model
This week, the Shai-Hulud npm campaign showed how quickly a compromised package can move through the software supply chain, jumping across trusted dependencies and reaching build pipelines before many teams even knew what they were looking at. But this is not just an npm story, and it is not just a story about one campaign.…
Move Faster From Cloud Risk to Remediation With Upwind Agentic Pack
Cloud security works best when teams can move from context to action in one place. Upwind already brings together runtime-powered security context across cloud infrastructure, applications, identities, workloads, APIs, and AI systems. Now, the Upwind Agentic Pack helps teams use that context faster across investigation, validation, and remediation workflows. Grounded in Upwind’s runtime-first platform, the…

The next wave of AI is here. Upwind becomes Agentic.
One of the most fascinating technologies I've encountered in my personal life over the past few years is autonomous driving. It started as a curiosity, “can my car really drive itself?” Can it actually make decisions with enough necessary context, and not rely solely on static things it sees like trees and roads? Can it…
Latest
May 28, 2026
Scale AI Adoption Securely With Upwind AI Security
AI is entering production faster than many security teams can keep up. As teams embed AI into applications, developer workflows, and cloud operations, security teams need to know where AI runs, what it can access, and which risks need action. Upwind AI Security connects AI usage to realtime cloud context, giving teams a practical way…
May 22, 2026
Refuse the Seat: Why Modern CISO Leadership Advice Is Failing the Profession
Key Takeaways The single most repeated piece of advice in security leadership is also the one doing the most damage to the profession. Earn your seat at the table. Become a business translator. Integrate into the operator class. The CISOs who follow that advice end up burned out, legally exposed, and stuck in five-jobs-in-one roles…
May 20, 2026
Upwind AI Security: Securing your AI stack from the inside-out
AI is changing how we build, work, and operate. It is moving from experimentation into production applications, customer experiences, developer workflows, and cloud operations. As AI moves closer to the core of the business, it is gaining access to the systems that matter most: sensitive data, internal tools, cloud services, and non-human identities. AI changed…
May 19, 2026
Newly Discovered durabletask Malware Targeted Kubernetes, Cloud Secrets, and CI/CD Infrastructure
Executive Summary Upwind identified a critical supply chain compromise involving durabletask==1.4.1, 1.4.2, and 1.4.3, three consecutive malicious releases of Microsoft's Azure Durable Task Python SDK published to PyPI. The malicious release contains a lightweight dropper embedded directly into durabletask/init.py. On import, the package downloads and executes a remote payload named rope.pyz from attacker-controlled infrastructure. The…
May 19, 2026
The New Face of Supply Chain Attacks: npm Malware Built for CI/CD and Cloud Compromise
Executive Summary Upwind is tracking an active software supply chain campaign impacting multiple npm packages commonly used across developer tooling, frontend frameworks, CI/CD pipelines, and cloud-native application environments. We identified malicious payloads designed specifically to target CI/CD systems, cloud identities, GitHub credentials, npm publishing workflows, developer machines, and AI developer tooling. The campaign includes install-time…
May 15, 2026
Validate Real Cloud Risk with Red, the Validation Agent
After teams identify the risks that matter, the next challenge is proving which ones are actually exploitable. Severity scores, exposure labels, and long lists of findings can point teams in the right direction, but they do not always show whether an attacker has a viable path to impact. In cloud environments, that path often depends…
May 14, 2026
The Supply Chain Strikes Again: Credential-Stealing Malware Hidden in node-ipc
Executive Summary On May 14, 2026, malicious versions of the widely used node-ipc npm package were published through a legitimate maintainer account, introducing a sophisticated credential-stealing payload into a package with approximately 3.35 million monthly downloads. The malicious payload was hidden inside the CommonJS bundle (node-ipc.cjs) and silently executed whenever applications loaded the package through…
May 14, 2026
Accelerate Cloud Security Investigations with Blue, the SecOps Agent
The AI threat landscape is moving faster on both sides. Attackers are using AI to scale campaigns, accelerate exploit development, and move faster from discovery to execution. Defenders need AI that helps them keep pace without adding noise or pulling teams away from the work that matters most. Prioritization helps teams focus on the risks…
May 13, 2026
The AI Threat Landscape Demands a New Cloud Security Model
This week, the Shai-Hulud npm campaign showed how quickly a compromised package can move through the software supply chain, jumping across trusted dependencies and reaching build pipelines before many teams even knew what they were looking at. But this is not just an npm story, and it is not just a story about one campaign.…
May 13, 2026
Move Faster From Cloud Risk to Remediation With Upwind Agentic Pack
Cloud security works best when teams can move from context to action in one place. Upwind already brings together runtime-powered security context across cloud infrastructure, applications, identities, workloads, APIs, and AI systems. Now, the Upwind Agentic Pack helps teams use that context faster across investigation, validation, and remediation workflows. Grounded in Upwind’s runtime-first platform, the…
May 13, 2026
The next wave of AI is here. Upwind becomes Agentic.
One of the most fascinating technologies I've encountered in my personal life over the past few years is autonomous driving. It started as a curiosity, “can my car really drive itself?” Can it actually make decisions with enough necessary context, and not rely solely on static things it sees like trees and roads? Can it…

May 12, 2026
Introducing Upwind AI Security: One platform, built for the agentic era
Key takeaways: Cloud security and AI security stop being two things For the last couple of years, a lot of the security industry has been quietly insisting that AI security has to be its own thing. Keep tools, teams, budgets, and dashboards separate or else… Well, we disagree. We listened to our customers, and what…