Up & Up
The best talent is global
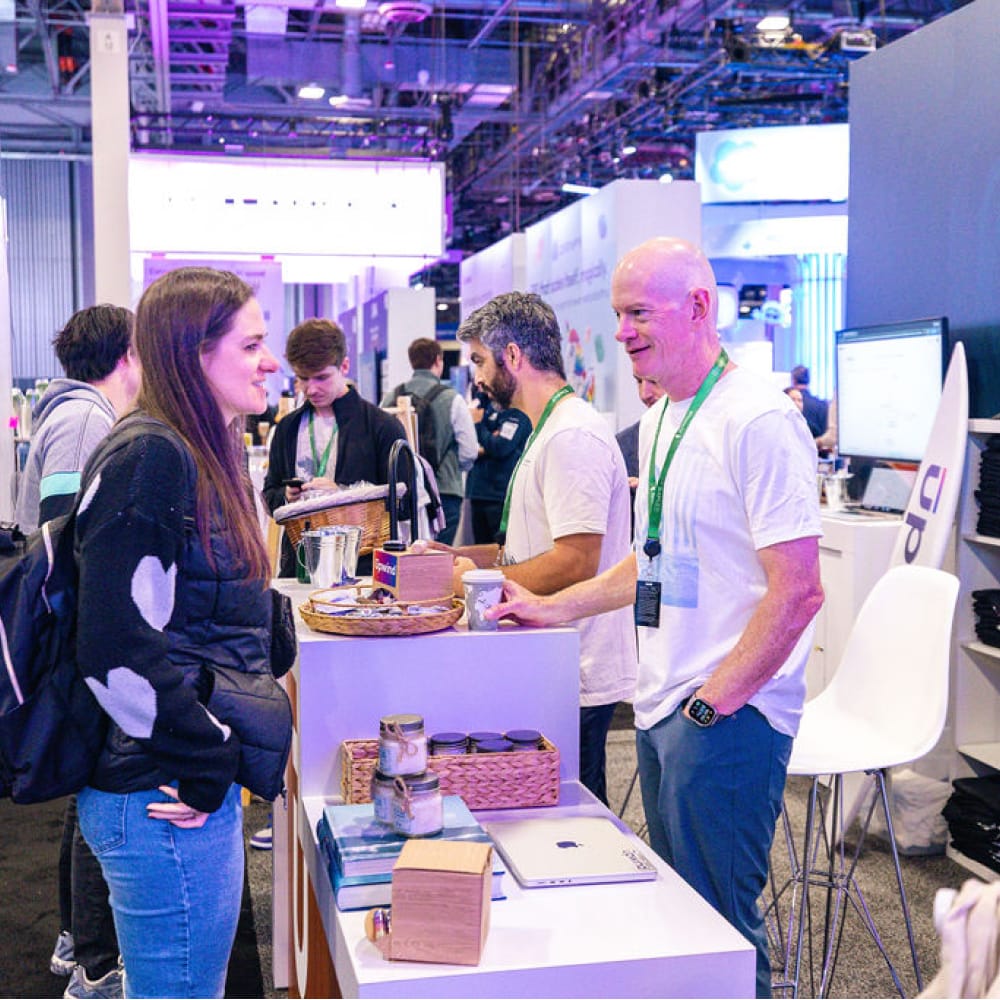
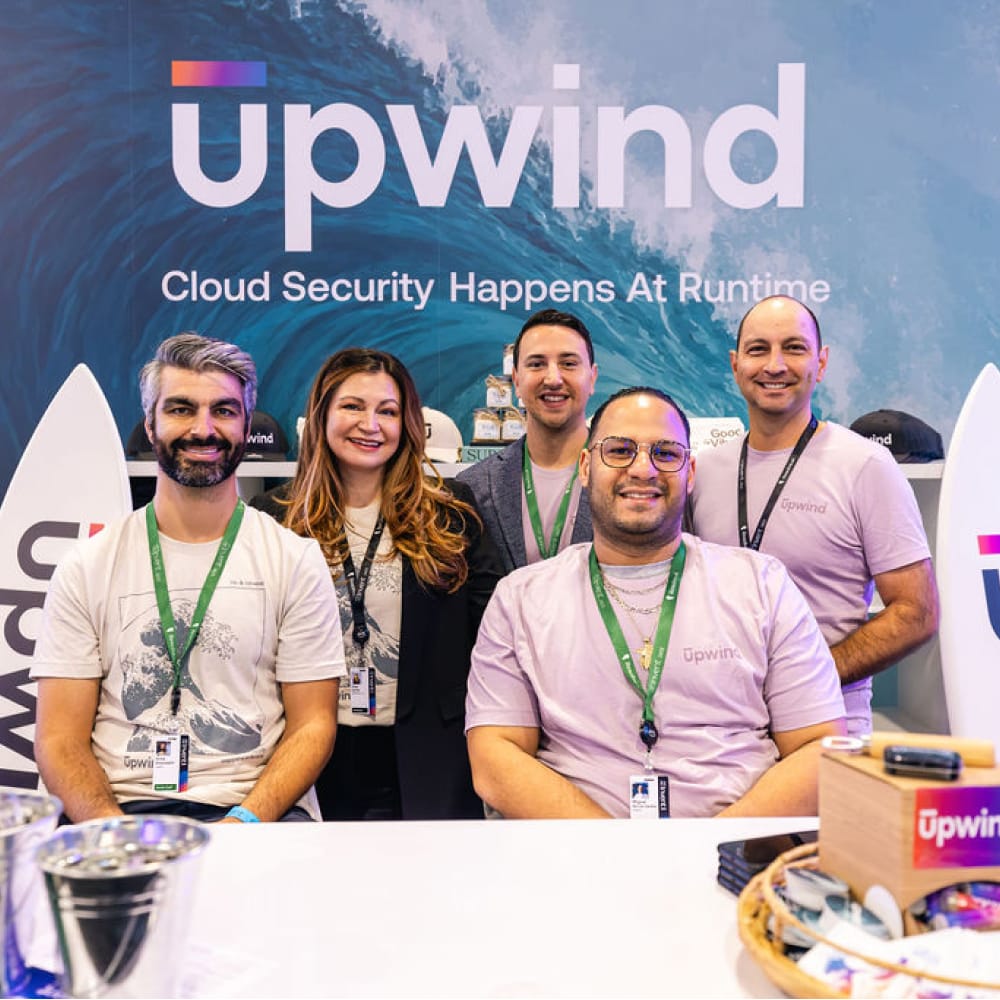
Moments that bring us together
Open positions
GRC Analyst
About The Position
About Upwind
Upwind is a next-generation Cloud Security Platform that leverages runtime context to identify and prioritize critical risks, providing precise insights and efficient cloud security management. With industry-leading efficiency and eBPF-powered sensors, Upwind delivers comprehensive capabilities including agentless cloud posture discovery, real-time threat protection, and integrated API security. We are one of the fastest-growing companies in cloud and AI security, and we're building the GTM engine to match.
The Opportunity
We are looking for a motivated and resourceful GRC Analyst to join our growing Security & Compliance team.
This is a hands-on role for someone who enjoys solving problems, takes ownership of their work, and is comfortable operating in a fast-paced environment where processes are continuously evolving and improving. We are looking for someone who is curious, willing to dig into unfamiliar topics, and comfortable finding practical ways to solve compliance and security challenges.
The GRC Analyst will support our core GRC functions - including risk assessments, internal audits, policy governance, third-party risk, customer trust and assurance, and compliance programs - while also serving as a practical partner to teams across the company. This role should be able to move beyond identifying a gap or requirement and help teams understand what good remediation looks like and how to build sustainable processes to address it. We also want someone who is comfortable using modern cloud-based security, compliance, automation, and AI-enabled tools to make GRC work more effective and scalable.
We also value people who have experience in using AI and automation to make GRC work smarter and more scalable, while applying appropriate judgment and validation to the output.
What You'll Do
- Operate and improve Upwind's GRC and security compliance programs
- Support compliance work across SOC 2, ISO 27001, NIST, and FedRAMP, including control implementation, evidence collection, documentation, remediation tracking, continuous monitoring, and audit readiness
- Coordinate audit and compliance evidence from Engineering, IT, Security, Legal, and HR
- Translate compliance requirements into clear actions for technical and business teams
- Perform control assessments, gap analyses, and risk assessments, and recommend how to fix what you find
- Work with process owners to build remediation that holds up over time and can be evidenced
- Track vulnerabilities, risks, audit findings, and POA&Ms through completion
- Handle customer security questionnaires, due diligence requests, and security documentation
- Support third-party risk management and vendor security assessments
- Write and maintain policies, standards, procedures, and control documentation
- Maintain GRC systems, evidence repositories, and risk registers
- Research new regulatory and customer requirements and determine how they apply to us
- Use AI and automation to speed up research, documentation, evidence organization, and workflow, with appropriate validation and data handling
- Raise gaps and issues early, with a proposed fix
Requirements
What We're Looking For
- 3 to 5 years in GRC, cybersecurity, risk management, compliance, or audit. We'll consider less conventional backgrounds if the relevant experience is there.
- Familiarity with NIST 800-53, SOC 2, ISO 27001, NIST CSF, or similar frameworks
- Experience supporting audits, assessments, security questionnaires, or evidence collection
- Strong written communication and documentation skills
- Enough technical fluency to work effectively with Engineering, IT, and Security
- Ability to turn audit findings into remediation plans that process owners will actually adopt
- Comfort working in a fast-moving environment where priorities shift
- Ownership. You drive assigned work to a conclusion and flag blockers rather than waiting.
- Curiosity. You can research an unfamiliar requirement and figure out the right questions to ask.
- Demonstrated use of technology to improve GRC work: risk analysis, evidence collection, control monitoring, remediation tracking, research, customer trust, or workflow automation
- Organized and detail-oriented
Nice to Have
- FedRAMP, NIST 800-53, or other U.S. government compliance experience, including POA&Ms, continuous monitoring, or assessment activities
- Experience working with external assessors on formal readiness or assessment activities
- Cloud security experience, particularly AWS or AWS GovCloud
- Background in SaaS, cloud security, or a high-growth technology company
- Experience with a global, distributed workforce across time zones
- Hands-on experience with cloud-based GRC, compliance automation, or AI-enabled workflow platforms
- Experience building GRC automations, integrations, or dashboards
- Familiarity with Jira, GitHub, or similar tools
- Certifications such as Security+, CISA, CRISC, CISM, CGRC, or ISO 27001
- Relevant certifications such as Security+, CISA, CRISC, CISM, CGRC, ISO 27001, or similar.