
CVE: CVE-2024-3094
Affected versions: 5.6.0, 5.6.1
Affected Distributions: Fedora 41, Fedora Rawhide, Alpine, openSUSE, Debian experimental distributions versions 5.5.1alpha-0.1 to 5.6.1-1.
On March 29, 2024, CISA warned of a malicious backdoor in the popular data compression software library XZ Utils. The vulnerability has been designated as CVE-2024-3094, and has been assigned a CVSS (Common Vulnerability Scoring System) score of 10.0.
CVE-2024-3094: the Linux Backdoor
The malicious actor injected code into the authentication process, allowing attackers to gain remote backdoor access via OpenSSH and systemd. The XZ utility includes a library called liblzma, used by SSHD, a core service of Linux servers in the cloud infrastructure used for remote access. When liblzma is loaded, CVE-2024-3094 affects SSHD authentication and could potentially allow bad actors remote access.
The backdoor was discovered by AndresFreundTec by email to the oss-security mailing list: backdoor in upstream xz/liblzma leading to SSH server compromise, announcing this discovery and explaining the exploit chain.
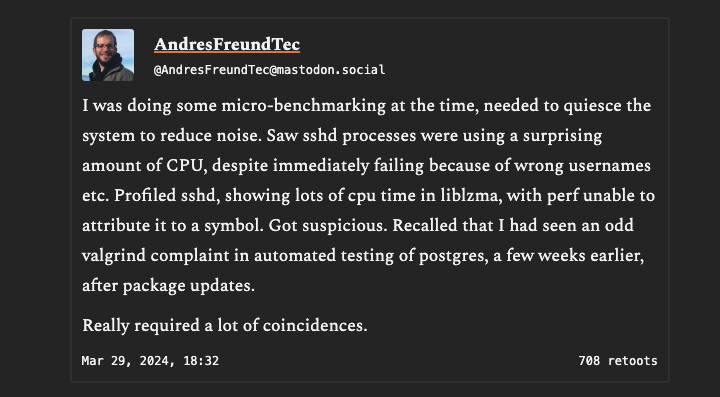
The backdoor works as follows – Linux machines install the backdoored xz library (liblzma, xz, or xz-utils) and the dependency is used by the OpenSSH daemon. When SSHD loads the malicious library, the backdoored xz library interacts with the daemon and redirects the authentication flow during the RSA key checking. Once the XZ library has control over the authentication flow, it can grant access based on an attacker’s criteria and allow them to gain remote control.
Impacted Linux Distros
Red Hat: vulnerable packages are present in Red Hat Fedora 41 and Red Hat Fedora Rawhide. Red Hat Enterprise Linux (RHEL) does not have any affected versions. Red Hat has recommended that all users stop using the affected versions until they can change the xz version.
SUSE: There is an update available for openSUSE (Tumbleweed or MicroOS).
Debian Linux: No stable versions of the distribution have been affected, but compromised packages were present for other versions (testing, unstable, experimental). Debian users should update XZ Utils.
Kali Linus: For those who updated systems between March 26-29, 2024, they should update again for the fix. If you have not updated Kali since before the 26th, it is not affected by the backdoor.
How to Find and Mitigate CVE-2024-3094
CVE-2024-3094 is present in XZ Utils versions 5.6.0 and 5.6.1. The US Cybersecurity and Infrastructure Security Agency (CISA) is advising users to downgrade UZ Utils to an earlier version (5.4.6 or a previous stable version) to avoid compromise.
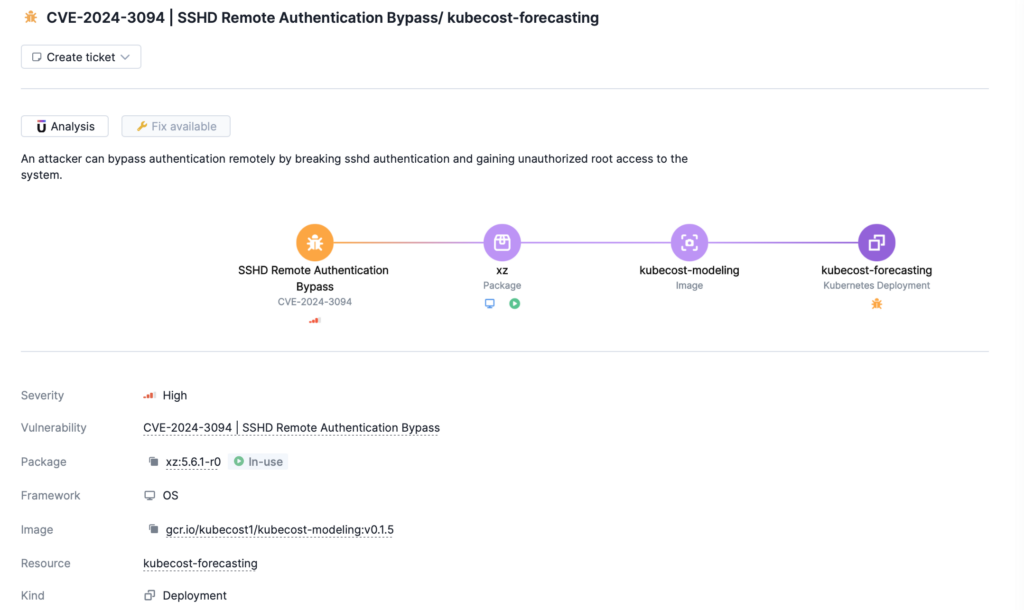
Upwind automatically identifies XZ Ultils running in your environment through several ways:
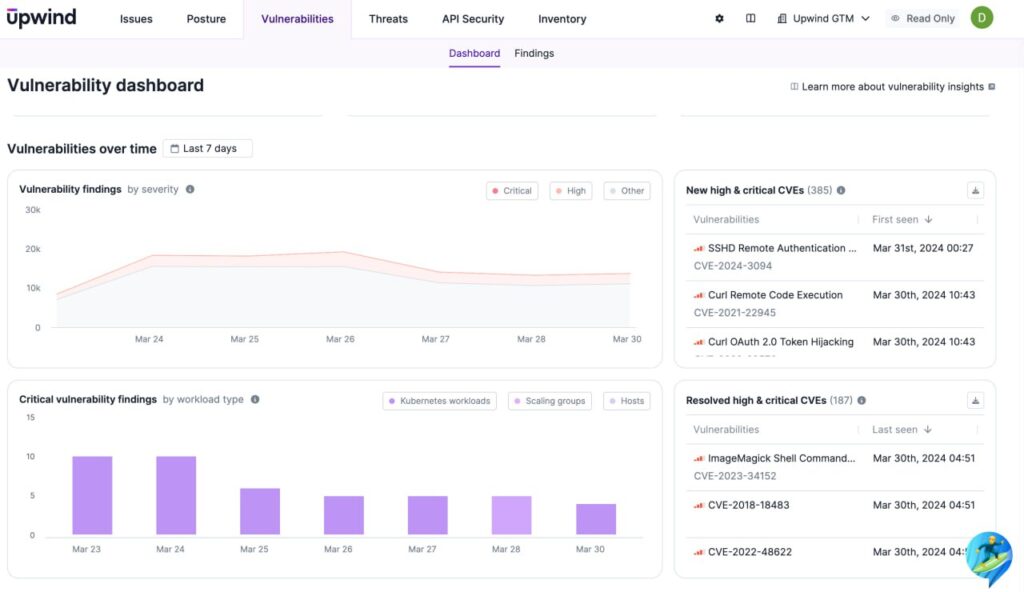
Upwind Vulnerability Dashboard
Upwind’s vulnerability management capabilities immediately identify vulnerabilities in your environment, including XZ Utils. This is based on real-time, runtime data – alerting you immediately to critical risks such as XZ Utils in your environment. This is shown as a critical vulnerability that should be mitigated immediately, along with recommended fixes.
SSH Sessions Monitoring
Upwind’s SSH Sessions page shows you every action performed during an SSH session, which is a key aspect of exploitations involving the XZ Utils vulnerability. Upwind Packages Tab
Upwind’s Packages tab immediately shows you all packages running in your environment, allowing you to find vulnerable packages running in your environment instantly. You can use the packages tab to find all XZ Utils instances and rapidly identify where they exist in your environment.
For more information on how Upwind identifies critical vulnerabilities, visit the Upwind Documentation Center (login required) or drop us a line at [email protected]