
Updated on November 11, 2026
Cybersecurity vulnerabilities have been tracked since 1999, when the Internet Category of Attack (ICAT) toolkit began compiling attack scripts and made them available to developers to look up easily. ICAT evolved into the National Vulnerability Database (NVD) of today, holding over 150,000 vulnerabilities and adding tens of thousands more annually, with CVE disclosure volumes having essentially tripled over a five-year span. Beyond the basics, we’re going over how complete the ever-expanding NVD is compared to other sources of cybersecurity intelligence, how quickly its threat scores are updated, and how to best use the NVD alongside multiple intelligence sources and behavioral analysis.
What is the National Vulnerability Database (NVD)?
The National Vulnerability Database (NVD) is a public repository maintained by the U.S. National Institute of Standards and Technology (NIST). It is a resource for cataloging and managing publicly disclosed cybersecurity vulnerabilities. Here are its core tasks:
- Cataloging all vulnerabilities that have been assigned a Common Vulnerabilities and Exposures (CVE) ID
- Providing threat ratings using the Common Vulnerability Scoring System (CVSS). For many entries, that rating now comes from the submitting CVE Numbering Authority (CNA), not a separate NIST score
- Adding data and analysis to CVEs, like weakness enumeration (CWE), mapping vulnerabilities to a known weakness class, patch information, or listing affected versions
- Offering an API gateway to connect NVD data to automation pipelines and vulnerability scanners for vulnerability management
The NVD does not discover vulnerabilities on its own. Instead, vulnerabilities are disclosed to the CVE system and MITRE, and CVE IDs are assigned through the work of researchers, vendors, and organizations that report them.
Further, the NVD does not track active threats or real-time exploit activity. Instead, it provides context to help organizations assess and prioritize vulnerabilities based on their severity, exploitability, and potential impact. That helps teams make more informed decisions in security workflows.
Prioritize Identifying Vulnerabilities with Runtime Scanning from Upwind
Upwind’s runtime-powered container scanning helps you prioritize CVEs effectively by providing real-time threat detection, contextualized analysis, and remediation insights. Understand which vulnerabilities matter most to your unique workloads and resolve them faster — up to 10X faster than traditional methods.
Get a DemoOn Vulnerability Discovery and Reporting with the NVD
The NVD is a foundational resource for cataloging vulnerabilities, assigning standardized scores (CVSS), and providing contextual information. As a U.S. government agency project, the NVD is part of how the National Institute of Standards and Technology (NIST) supports national security, critical U.S. infrastructure, economic stability, and, indirectly, private organizations.
That said, real-world vulnerability management often extends beyond what the NVD alone can provide, given a list of vulnerabilities to root out and eliminate may only create a checklist of tasks that extend beyond the capacity of teams but offer little in the way of improved security.
“Many customers report that they have experienced alert overload and a lack of prioritization in their security practice. At Upwind, we focus on real risk – cutting down noise by 95% and helping customers get to the root cause 10 times faster.”
–Joshua Burgin I CPO, Upwind
The NVD plays a significant role in cyber security. But its approach is cataloging, not action. So, teams will still need to identify the NVD’s listed vulnerabilities in their own systems and work to eliminate them efficiently, eliminating noise. They’ll also need to take note of the gaps in the NVD database. Let’s get a closer view of the vulnerability landscape of the NVD, looking at NVD challenges one at a time.
Timeliness and Delay in NVD Information
The NVD publishes CVE records as it ingests them, but since April 15, 2026, it no longer enriches every CVE by default. Lower-priority entries may sit in the NVD without NIST-added CVSS scores, product mappings, or CWE data for some time. Timeliness now depends on priority. NIST focuses enrichment on CVEs in CISA’s Known Exploited Vulnerabilities (KEV) Catalog, CVEs affecting software used by the U.S. federal government, and CVEs tied to “critical software” under Executive Order 14028. For KEV entries, the goal is enrichment within one business day. For everything else, vendor advisories or threat intelligence platforms may still move faster.
The solution is runtime security for real-time updates of exploits regardless of database timeliness or whether they’ve even been identified as vulnerabilities at the time of detection. Runtime security can also prioritize vulnerabilities actively being exploited in an organization’s environment, so less time is spent on vulnerabilities that aren’t critical.
Comprehensiveness of NVD Data
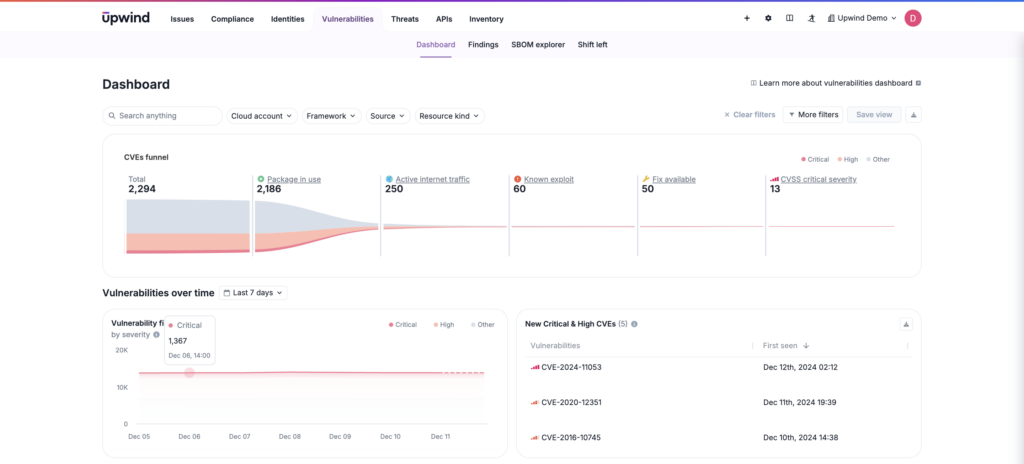
The NVD serves as a critical resource for cataloging vulnerabilities, but not all vulnerabilities are assigned CVE IDs, especially in niche or proprietary software. As an American-managed system, the NVD may also be biased toward U.S. software and disclosures, potentially leaving out vulnerabilities in regional or less-documented ecosystems. There are now gaps inside the NVD itself, too. In April 2026, NIST moved backlogged CVEs published before March 1, 2026 into a “Not Scheduled” category. Those entries may be enriched later, but only as resources permit and according to its new risk-based criteria.
These gaps mean relying solely on the NVD could leave blind spots in vulnerability management strategy. Some vulnerabilities are missing entirely, and others are listed but not yet enriched. When an NVD entry lacks scoring or product data, turn to CNA-supplied scores, the CISA KEV Catalog, and vendor advisories to fill in the picture.
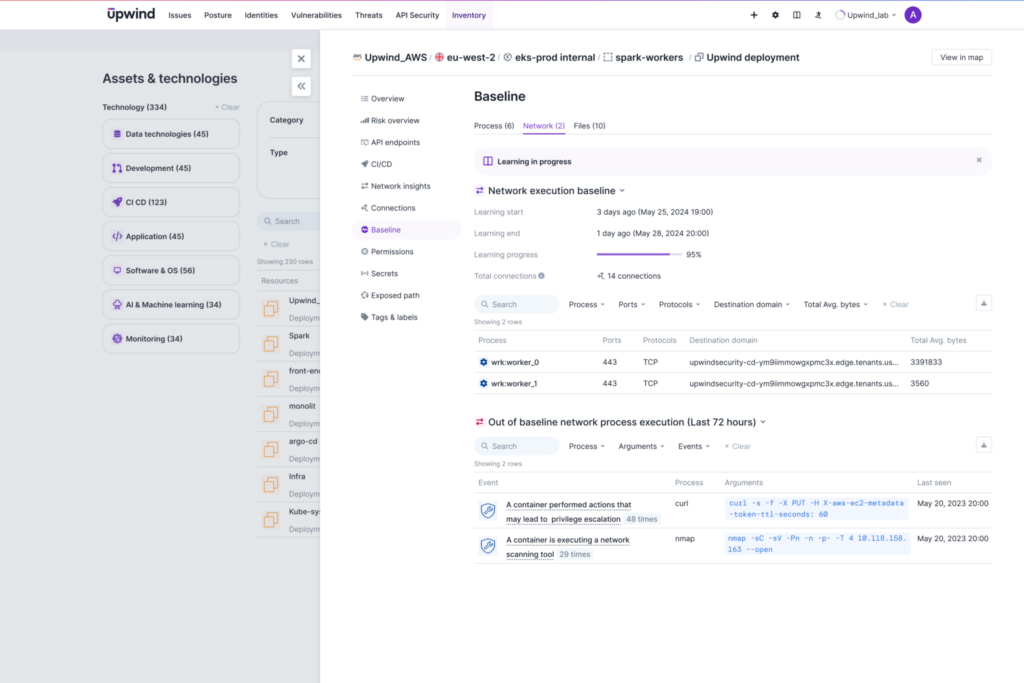
For instance, if an internal containerized application makes unexpected network connections or loads an unverified library during runtime, organizations would want to flag this behavior as a risk, even if there’s no corresponding CVE in the NVD.
Environment-Specific Threat Levels
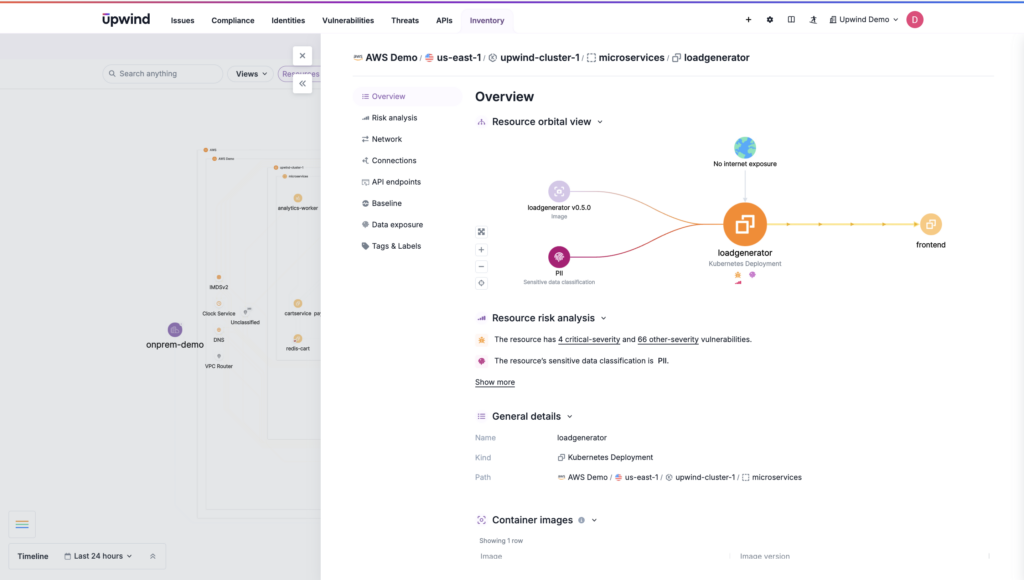
While the NVD provides standardized vulnerability data, it doesn’t inherently prioritize or contextualize risks for specific environments.
For personalized risk scores, organizations must correlate NVD data with runtime telemetry and attack path analysis, ensuring prioritized remediation.
Benefits and Limitations of the NVD for Vulnerability Security
The NVD provides a foundational layer for vulnerability management with broad coverage and simple integration into pipelines.
Let’s break down its key features, benefits, and limitations to help organizations understand how to maximize its use while addressing potential gaps.
| Facets of the NVD | Description | Strengths | Limitations |
| Scope | Catalogs vulnerabilities with CVE IDs across software and hardware. | Broad coverage of known vulnerabilities. | Excludes niche or proprietary software vulnerabilities. |
| Timeliness | Updates vulnerability data after CVEs are assigned and enriched with CVSS scores. | Standardized updates for many common vulnerabilities. | May lag behind vendor advisories or threat intelligence feeds, especially during active exploitation. |
| CVSS Scores | Assigns severity scores based on the Common Vulnerability Scoring System (CVSS). | Consistent framework for evaluating impact and prioritization. | Scores lack environment-specific context. |
| Dependency Analysis | Does not inherently analyze software stack dependencies. | N/A | Misses transitive vulnerabilities in layered dependencies. |
| Regional Coverage | Primarily based on disclosures from American organizations. | Excellent for widely used software with global reporting. | Regional biases may exclude vulnerabilities reported in non-U.S. contexts or languages. |
| Ease of Integration | Provides APIs for automated integration with security tools (e.g., SIEMs, SOAR platforms). | Enables integration into automated workflows. | Limited by static data and requires enrichment for dynamic environments. |
Organizations serious about vulnerability management often supplement the NVD with data from other large, reputable vulnerability databases to ensure comprehensive coverage and timeliness. So what are those, and how do they plug known gaps in the NVD? Here’s a breakdown of notable open-source and non-commercial databases:
1. MITRE CVE System
- What It Is: The foundational database that assigns unique CVE IDs to publicly disclosed vulnerabilities.
- Why It’s Important: The NVD relies on CVE entries as its primary data source, so MITRE is critical for initial vulnerability disclosure.
- Strengths:
- It’s universally recognized and foundational for vulnerability tracking.
- It covers the most widely reported vulnerabilities.
- Limitations:
- It contains minimal metadata compared to NVD (e.g., lacks CVSS scores or detailed references).
- It is not designed for prioritization or real-time threat assessment.
2. Exploit Database (Exploit-DB)
- What It Is: A free archive of publicly available exploits maintained by a private organization, Offensive Security (OffSec).
- Why It’s Important: It focuses on exploitation rather than just vulnerabilities, offering practical insights into attack methods.
- Strengths:
- It tracks active exploits for vulnerabilities, enabling organizations to assess real-world risk.
- It’s useful for red team exercises and security training.
- Limitations:
- It does not catalog all CVEs.
- It’s primarily a tool for penetration testing rather than full vulnerability management.
4. OSV (Open Source Vulnerabilities) Database
- What It Is: The OSV is a public-service vulnerability database focused on open-source software and maintained by Google.
- Why It’s Important: It addresses gaps in NVD coverage for open-source dependencies.
- Strengths:
- It’s tailored to developers and DevOps teams using open-source projects.
- It is integration-ready with tools like GitHub and open-source package managers.
- Limitations:
- The open-source focus may leave out proprietary software vulnerabilities.
- It is still evolving and not as comprehensive as the NVD.
5. CISA Known Exploited Vulnerabilities Catalog
- What It Is: It’s a curated list of actively exploited vulnerabilities published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
- Why It’s Important: It highlights high-risk vulnerabilities with a focus on active threats.
- Strengths:
- It focuses on actionable risks.
- It’s regularly updated to reflect new exploitation trends.
- Limitations:
- It’s limited in scope compared to NVD, prioritizing actively exploited CVEs.
- The U.S.-centric focus may omit relevant threats from other regions.
6. GitHub Security Advisories
- What It Is: A security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
- Why It’s Important: It targets open-source repositories, making it valuable for tracking vulnerabilities in widely used libraries.
- Strengths:
- It’s directly tied to GitHub, with alerts for repository users.
- It comes with a focus on developer-friendly remediation steps.
- Limitations:
- The narrow focus on GitHub-hosted projects.
- It does not cover broader ecosystems or proprietary software.
How Organizations Can Maximize the Value of the NVD
The National Vulnerability Database catalogs cybersecurity risks, but it is most effective as part of a broader vulnerability management strategy. But how? Here’s how organizations can make the most of the NVD:
1. Pair NVD Data with Active Threat Intelligence
The NVD focuses on cataloging vulnerabilities, not tracking active exploit trends. Organizations must integrate the NVD with tools that track active exploitation, such as the CISA Known Exploited Vulnerabilities Catalog or real-time threat intelligence platforms.
The result? Organizations gain the ability to Identify which NVD-listed vulnerabilities are currently being exploited in their ecosystems and prioritize patching accordingly.
2. Use Runtime Monitoring to Identify Environment-Specific Risks
The NVD provides static threat scores (CVSS) but does not factor in unique environmental contexts, such as misconfigurations or layered dependencies. Runtime security is the key here, too. Deploy runtime monitoring tools to detect risks tied to your specific configurations, even if those risks aren’t directly linked to CVEs.
3. Supplement the NVD with Additional Databases
No single database is entirely comprehensive. Use complementary sources like:
- Exploit-DB for exploit details.
- OSV Database for open-source vulnerabilities.
- Vendor-specific advisories for proprietary software.
4. Automate Vulnerability Management with NVD APIs
Automation reduces manual overhead and ensures consistent application of NVD data in security workflows. Use the NVD API to feed data into SIEM, SOAR, or use CNAPP tools that leverage NVD data for automated prioritization and remediation.
Have a specific use case? Here’s how to augment the NVD’s strengths for complete coverage:
| Use Case | NVD Role | Complementary Action | Example Tool |
| Identifying known vulnerabilities | Catalogs CVEs and provides standardized metadata | Use vendor advisories for faster updates | Microsoft Security Advisories |
| Prioritizing high-risk vulnerabilities | Shows CVSS scores and enriches KEV, federal-use, and EO 14028 critical software CVEs first | Correlate with runtime exploit activity | CISA Known Exploited Vulnerabilities Catalog |
| Addressing open-source dependencies | Includes some open-source vulnerabilities | Integrate with the OSV database | GitHub Security Advisories |
| Detecting misconfigurations | NVD does not track configuration issues | Use runtime monitoring for real-time risk assessment | CSPM or a comprehensive CNAPP |
| Automating vulnerability workflows | Provides API access | Enrich with attack path analysis | SIEM or SOAR tools |
Organizations can create a more holistic vulnerability management strategy by combining the NVD’s foundational data with dynamic tools and complementary databases. This approach not only fills gaps in the NVD but also ensures timely and context-aware responses to evolving threats.
How to Handle New NVD Statuses in Automation
The NVD’s April 2026 workflow came with new CVE statuses. New lower-priority CVEs are flagged “Lowest Priority,” older backlog entries sit in “Not Scheduled,” and CVEs marked “deferred” in 2025 were moved to a “Modified After Enrichment” status.
Review your SIEM, SOAR, scanner, and reporting logic to make sure CVEs in these buckets don’t silently disappear from dashboards or SLA tracking. A CVE without NIST enrichment can still be a real risk in your environment, so it should still be counted, routed, and tracked.
NIST has also said it will only re-examine later CVE modifications when they materially affect enrichment data. Updates to a CVE won’t always trigger a full NVD re-analysis, so teams should watch vendor advisories and CNA data more closely for changes the NVD may not reflect.
Upwind Superpowers Vulnerability Detection
It’s not just about listing vulnerabilities. It’s about knowing about them quickly, identifying zero days and those outside the scope of the NVD, and assessing criticality — not just overall, but for an organization’s specific, unique ecosystem.
Upwind makes identifying and mitigating vulnerabilities easier. See how. Schedule a demo today.
FAQ
What is the difference between NIST and the NVD?
NIST (National Institute of Standards and Technology) is a U.S. government agency that develops standards, guidelines, and tools to improve cybersecurity.
One of their projects is the NVD (National Vulnerability Database).
It’s a specific program operated by NIST that catalogs publicly disclosed vulnerabilities, enriches them with CVSS scores and other metadata, and provides tools for organizations to integrate that data into their security workflows.
Which is better? ISO or NIST?
Both are prominent frameworks for cybersecurity. Which one is right for you to adopt for compliance and certification? That depends.
ISO is best for global, high-level frameworks and certification (e.g., ISO 27001). It spans countries and industries, so it’s favored by multinational corporations.
NIST is more detailed and technical, widely used in U.S.-based organizations and industries like government and critical infrastructure. Companies choose NIST for detailed and flexible technical controls, especially in U.S. contexts.
How frequently is the NVD updated?
The NVD is updated multiple times per day as new CVE entries are published. Since April 15, 2026, however, NIST no longer enriches every CVE with additional data like CVSS scores, CWE mappings, and affected software details. Enrichment is prioritized, and many entries carry only the severity score supplied by the CNA.
However, the timeliness of updates depends on when CVEs are disclosed and processed by MITRE and NIST.
When would you use the NVD?
Teams use the NVD to:
- Identify Known Vulnerabilities: Look up vulnerabilities by CVE ID to assess their details, severity (CVSS score), and affected software versions.
- Prioritize Remediation: Use CVSS scores and exploitability data to focus on addressing the most critical vulnerabilities.
- Integrate into Security Tools: Automate vulnerability management by feeding NVD data into vulnerability scanners.
- Support Compliance: Leverage NVD data to meet regulatory or industry standards requiring vulnerability assessments (e.g., PCI DSS, HIPAA).
- Research Vulnerability Trends: Analyze historical and emerging vulnerabilities to improve long-term security strategies.
It’s common for security solutions to use the NVD to enhance detection and analysis capabilities. Incorporating known vulnerabilities with runtime intelligence means companies can focus on critical risks and remediate vulnerabilities more efficiently, knowing they’re addressing those that make a difference in their own environments.
What is the difference between CVE and NVD?
A CVE is the identifier for a specific vulnerability, giving it a unique ID so everyone refers to the same flaw. The NVD is the National Vulnerability Database. It lists CVEs and adds extra information, such as severity scores and affected product lists, to help with prioritization. In simple terms, the CVE tells you what the vulnerability is, and the NVD tells you how severe it is and what it affects.
How do you search the NVD by CVE or product?
You can search for a specific vulnerability directly by its CVE ID. You can also search by product, using the affected software details, which the NVD represents with CPE data and version information. If you work with the NVD API in Python, the nvdlib library supports keyword searches. It also supports product searches using a CPE match string, with optional version ranges and CVSS severity filters.
Is the National Vulnerability Database free to use?
Yes. The NVD is a public U.S. government resource, available at nvd.nist.gov.
What is the NVD API, and do you need an API key?
The NVD API is NIST’s programmatic interface to National Vulnerability Database data. Integrations such as ServiceNow’s NIST NVD integration use it to pull CVE data into security tools. An API key is technically optional, but requests without one face much more aggressive rate limiting, and using a valid key greatly reduces errors and failed requests.