Feed
Upwind Feed
Feed
Grid
Product
December 3, 2025
Expanding CSPM with Runtime Advantage: Deep Data Scanning & Multi-Cloud Parity

We are excited to announce a major expansion of the Upwind Runtime Attack Surface Management. This release extends support for GCP, OCI, and Azure resources, bringing true multi-cloud parity while deepening AWS support with expanded support for AWS Lambda, SNS, Elasticache, and Redis. Beyond coverage, we are introducing Deep Data Scanning - a new ASM…
December 3, 2025
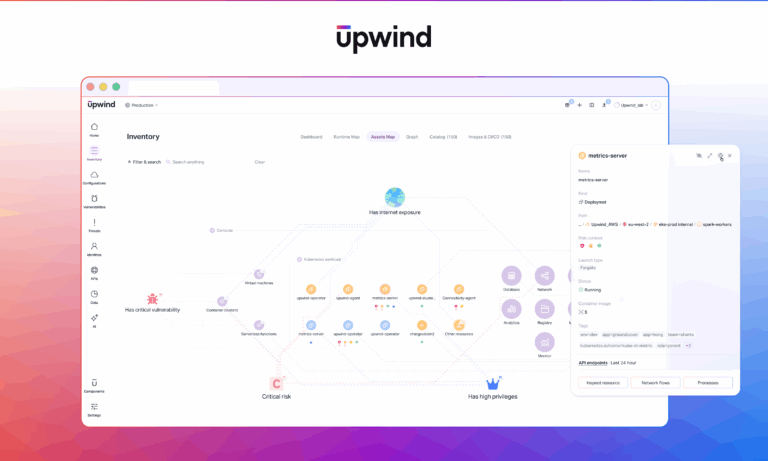
Introducing the Upwind Asset Map: Complete Visibility into Cloud Architecture, Exposure, and Risks

Cloud risks arise across multiple layers and dimensions: (1) infrastructure such as compute, networks, storage, and identities; (2) applications and their API or service-to-service communications; and (3) the dependencies that link them together, including vulnerabilities, secrets, and sensitive data flows. Upwind’s Graph Inventory overlays cloud assets, configurations, SBOMs, runtime sensor & cloud activity logs signals,…
December 2, 2025
Securing the Next Generation of AI Infrastructure at Runtime

Artificial intelligence is rapidly transforming the enterprise landscape, powering everything from autonomous agents to large-scale LLM applications. However, as organizations adopt AI infrastructure at scale, they face an urgent challenge: ensuring the integrity, safety, and trustworthiness of their AI operations in the face of increasingly sophisticated cyber threats. Moreover, a new set of threats comes…
December 1, 2025
Introducing Upwind’s Unified AI Protection, Built for Modern Cloud Environments
Today, we’re expanding the Upwind CNAPP with Upwind AI, a set of tightly integrated capabilities that take AI security far beyond configuration checks or endpoint monitoring. As AI becomes embedded in every layer of cloud infrastructure, security teams need a way to understand not just where AI is running, but how it behaves, what it…
November 21, 2025
The Hidden Costs of Agentless Cloud Scanning
A deep dive into architectures, trade-offs, and total cost of ownership Agentless cloud scanning has become a foundational capability for cloud-native security. By connecting directly to cloud provider APIs, organizations gain near-instant visibility into configurations, assets, and vulnerabilities without deploying agents or modifying workloads. The operational appeal is clear: agentless scanning reduces friction for DevOps,…
November 20, 2025
Upwind Delivers Security Feedback where Developers Already Work, in GitLab

We’re thrilled to announce that Upwind now automatically posts concise, runtime-informed vulnerability feedback directly on GitLab merge requests when enabled in your CI/CD pipeline. Developers spend most of their time in merge requests, where they also need security context. As part of our Shift Left capabilities, Upwind brings prioritized, contextual findings into the GitLab review…
November 18, 2025
Automate Cloud Risk Management, Mitigation and Response with Tines and Upwind
Modern cloud environments generate an overwhelming volume of configuration and security alerts, leaving teams struggling to separate signal from noise. Manually investigating and remediating critical risks slows response times and increases exposure. Together, Upwind and Tines solve this by combining Upwind’s runtime-powered insights, findings, and detections with Tines’ intelligent workflow platform—allowing teams to detect, prioritize,…
November 12, 2025
End-to-End Application Risk Management with Upwind and Endor Labs
Organizations today face mounting pressure to manage vulnerabilities across increasingly complex cloud environments and software supply chains. According to Gartner, 45% of organizations worldwide will have experienced attacks on their software supply chains by 2025, a threefold increase from 2021. This surge highlights the need for proactive, integrated security solutions that not only uncover vulnerabilities…
November 10, 2025
Introducing Upwind’s ‘Open Source Security’ Model for Extreme Ownership of Cloud Risks
In today’s fast-paced cloud environments, risks and threats evolve by the minute, and teams closest to the code and infrastructure need the ability to understand their security posture, but also the flexibility of taking ownership of how to prioritize and remediate any given risk. In order to do so, security professionals need a way to…
November 4, 2025
Upwind Accelerates Time-to-Value for NIST Compliance
We’re excited to announce that Upwind now supports the NIST Cybersecurity Framework, giving organizations a faster and more effective path to achieving compliance across their environments. With this release, all Upwind customers can map their entire cloud and containerized infrastructure to NIST controls in a single day, gaining instant visibility into alignment, gaps, and risk.…
October 30, 2025
Upwind Named to Fortune’s Cyber 60 for 2025-26
We’re thrilled to announce that Upwind has once again earned a spot on the prestigious Cyber 60 list, the definitive ranking of the 60 fastest-growing cybersecurity companies worldwide, compiled by Lightspeed Venture Partners in partnership with Fortune and AWS. This list recognizes the 60 fastest-growing cybersecurity startups, highlighting our commitment to innovation and delivering an…
October 30, 2025
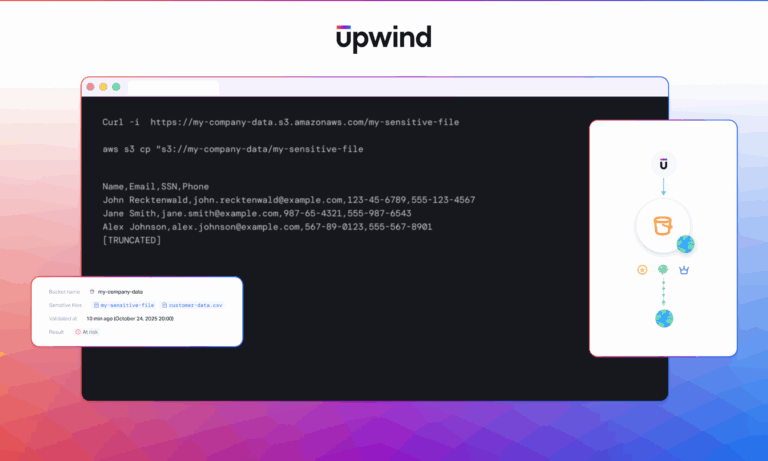
Reinventing CSPM with Dynamic Testing of Security Risks
In modern cloud environments, risk moves between developers pushing new code, operations managing infrastructure, and security teams overseeing the broader threat landscape. In addition to the shared risk and collaboration challenges, teams are also often inundated with thousands of configuration alerts on a daily basis, making it difficult to prioritize truly critical risks with evidence…
Expanding CSPM with Runtime Advantage: Deep Data Scanning & Multi-Cloud Parity
We are excited to announce a major expansion of the Upwind Runtime Attack Surface Management. This release extends support for GCP, OCI, and Azure resources, bringing true multi-cloud parity while deepening AWS support with expanded support for AWS Lambda, SNS, Elasticache, and Redis. Beyond coverage, we are introducing Deep Data Scanning - a new ASM…
Introducing the Upwind Asset Map: Complete Visibility into Cloud Architecture, Exposure, and Risks
Cloud risks arise across multiple layers and dimensions: (1) infrastructure such as compute, networks, storage, and identities; (2) applications and their API or service-to-service communications; and (3) the dependencies that link them together, including vulnerabilities, secrets, and sensitive data flows. Upwind’s Graph Inventory overlays cloud assets, configurations, SBOMs, runtime sensor & cloud activity logs signals,…
Securing the Next Generation of AI Infrastructure at Runtime
Artificial intelligence is rapidly transforming the enterprise landscape, powering everything from autonomous agents to large-scale LLM applications. However, as organizations adopt AI infrastructure at scale, they face an urgent challenge: ensuring the integrity, safety, and trustworthiness of their AI operations in the face of increasingly sophisticated cyber threats. Moreover, a new set of threats comes…
Introducing Upwind’s Unified AI Protection, Built for Modern Cloud Environments
Today, we’re expanding the Upwind CNAPP with Upwind AI, a set of tightly integrated capabilities that take AI security far beyond configuration checks or endpoint monitoring. As AI becomes embedded in every layer of cloud infrastructure, security teams need a way to understand not just where AI is running, but how it behaves, what it…
The Hidden Costs of Agentless Cloud Scanning
A deep dive into architectures, trade-offs, and total cost of ownership Agentless cloud scanning has become a foundational capability for cloud-native security. By connecting directly to cloud provider APIs, organizations gain near-instant visibility into configurations, assets, and vulnerabilities without deploying agents or modifying workloads. The operational appeal is clear: agentless scanning reduces friction for DevOps,…
Upwind Delivers Security Feedback where Developers Already Work, in GitLab
We’re thrilled to announce that Upwind now automatically posts concise, runtime-informed vulnerability feedback directly on GitLab merge requests when enabled in your CI/CD pipeline. Developers spend most of their time in merge requests, where they also need security context. As part of our Shift Left capabilities, Upwind brings prioritized, contextual findings into the GitLab review…
Automate Cloud Risk Management, Mitigation and Response with Tines and Upwind
Modern cloud environments generate an overwhelming volume of configuration and security alerts, leaving teams struggling to separate signal from noise. Manually investigating and remediating critical risks slows response times and increases exposure. Together, Upwind and Tines solve this by combining Upwind’s runtime-powered insights, findings, and detections with Tines’ intelligent workflow platform—allowing teams to detect, prioritize,…
End-to-End Application Risk Management with Upwind and Endor Labs
Organizations today face mounting pressure to manage vulnerabilities across increasingly complex cloud environments and software supply chains. According to Gartner, 45% of organizations worldwide will have experienced attacks on their software supply chains by 2025, a threefold increase from 2021. This surge highlights the need for proactive, integrated security solutions that not only uncover vulnerabilities…
Introducing Upwind’s ‘Open Source Security’ Model for Extreme Ownership of Cloud Risks
In today’s fast-paced cloud environments, risks and threats evolve by the minute, and teams closest to the code and infrastructure need the ability to understand their security posture, but also the flexibility of taking ownership of how to prioritize and remediate any given risk. In order to do so, security professionals need a way to…
Upwind Accelerates Time-to-Value for NIST Compliance
We’re excited to announce that Upwind now supports the NIST Cybersecurity Framework, giving organizations a faster and more effective path to achieving compliance across their environments. With this release, all Upwind customers can map their entire cloud and containerized infrastructure to NIST controls in a single day, gaining instant visibility into alignment, gaps, and risk.…
Upwind Named to Fortune’s Cyber 60 for 2025-26
We’re thrilled to announce that Upwind has once again earned a spot on the prestigious Cyber 60 list, the definitive ranking of the 60 fastest-growing cybersecurity companies worldwide, compiled by Lightspeed Venture Partners in partnership with Fortune and AWS. This list recognizes the 60 fastest-growing cybersecurity startups, highlighting our commitment to innovation and delivering an…
Reinventing CSPM with Dynamic Testing of Security Risks
In modern cloud environments, risk moves between developers pushing new code, operations managing infrastructure, and security teams overseeing the broader threat landscape. In addition to the shared risk and collaboration challenges, teams are also often inundated with thousands of configuration alerts on a daily basis, making it difficult to prioritize truly critical risks with evidence…