Feed
Upwind Feed
Feed
Grid
Product
October 28, 2025
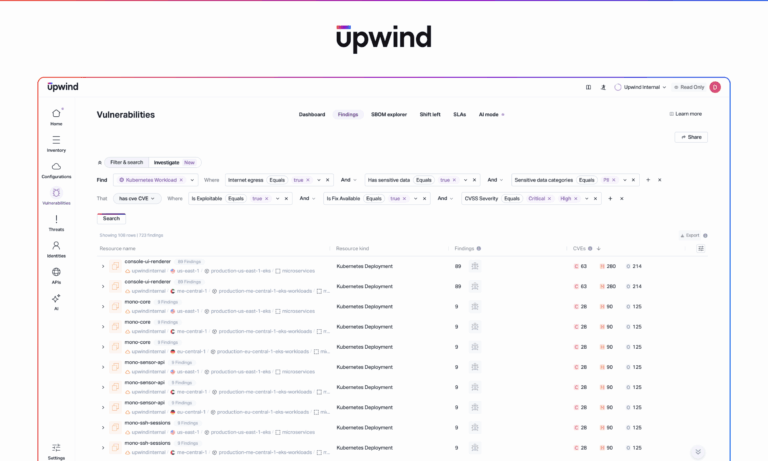
Accelerate Vulnerability Investigations with Visual Contextualized Queries


Modern cloud environments generate a constant stream of vulnerability information across thousands of assets, frameworks, and packages. While filters are essential to navigate this data, they can quickly become overwhelming as environments grow. Upwind’s new Investigate tab introduces a more efficient and guided way to explore vulnerabilities. Instead of relying on long lists of filters,…
October 22, 2025
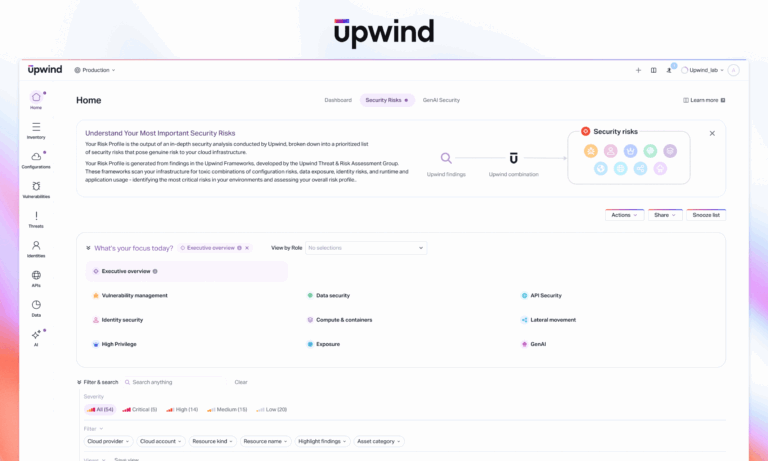
Introducing Security Risks: A Unified Model for Understanding Cloud Risks

Cloud security teams face an overwhelming amount of data. Misconfigurations, vulnerabilities, identity risks, and exposures often live in separate tools and dashboards, making it difficult to see how they connect. The real challenge is understanding how these signals intersect to create true risk. That's why we are excited to introduce Upwind Security Risks - a unified…
October 21, 2025
Upwind Strengthens Cloud Identity Security with New Microsoft Entra ID Detection Coverage
We are thrilled to announce that Upwind has expanded its Microsoft Entra ID (formerly Azure Active Directory) detection coverage to provide deeper visibility into identity changes, privilege escalation, and credential misuse across Azure environments. These new detections help security teams identify and respond to identity-driven threats faster, before they can compromise the tenant or persist…
October 13, 2025
Upwind Enables Smarter, More Efficient, Security with Sensor Improvements
We are excited to share the latest improvements to our eBPF-powered sensor, the foundation of our runtime security platform. By continuously enhancing how the sensor observes and protects Kubernetes environments, we’re making security both more effective and more efficient for our customers. As part of this advancement, we are introducing container image scan jobs, a…
October 9, 2025
Upwind Expands Threat Detection with Native Azure Log Analytics Integration
Upwind is excited to announce a new integration that brings deeper visibility and faster threat detection to Microsoft Azure environments. With native support for Azure Log Analytics and Activity Logs, customers can now detect risks and respond to threats across Azure with greater precision, especially around administrative activity, access patterns, and configuration changes. This release…
October 1, 2025
Upwind Modernizes PCI-DSS for Cloud-Native Security
We’re introducing the Upwind Framework for PCI-DSS to help organizations meet one of the most widely adopted security standards. This release is part of Upwind’s broader mission to make compliance continuous and directly tied to runtime environments. In this blog, we will explain what PCI-DSS is and why it matters, highlight the growing challenges of…
September 29, 2025
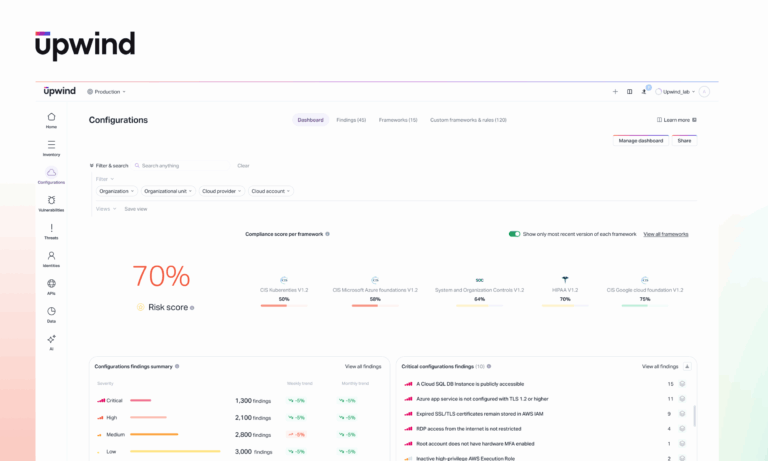
Streamline Compliance & Auditing with Upwind’s Configurations Dashboard
If you’re responsible for cloud security and compliance, you know the drill. Misconfigurations pile up across environments, frameworks keep updating, and leadership wants to see progress - all while your team is already stretched thin. The stakes are high. A single overlooked configuration can lead to major gaps in compliance, or worse, leave sensitive data…
September 25, 2025
Harbor Shift Left: Bringing Runtime Intelligence to Container Security

Picture this: your development team is racing to deploy a critical update, but security scanning brings everything to a halt. The scanner reports 47 vulnerabilities, but which ones actually matter? Which are exploitable in production? And most importantly, should you block the deployment or proceed? This is the daily reality for most DevOps teams. Traditional…
September 22, 2025
Upwind Now Supports CloudTrail Log Aggregation for More Accurate Detections
A security team at a large financial services company once spotted a troubling pattern: a low-privilege IAM role listed IAM users, created an inline policy, and then assumed a higher-privilege role. Each action looked routine on its own and slipped past their detection system, which analyzed events in isolation. Only later, during a manual review,…
September 16, 2025
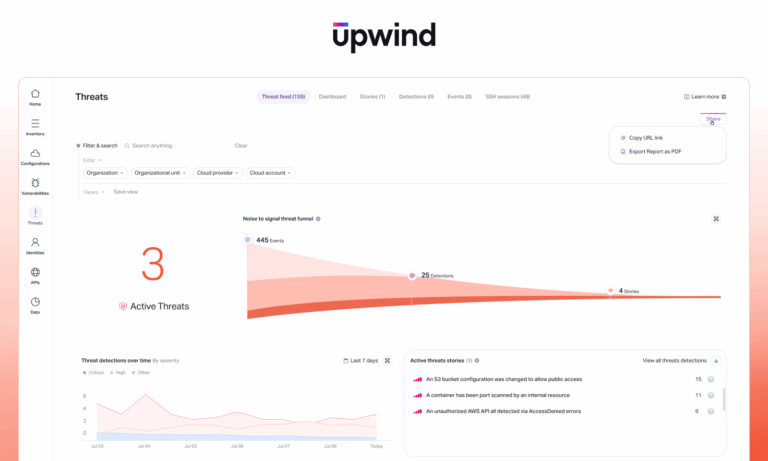
Introducing Upwind’s New Threat Dashboard: Simplifying Complexity to Drive Action
Today, we’re excited to announce the release of the enhanced Upwind Threat Dashboard, part of our ongoing commitment to continuously improving how we help security teams protect their environments. Threat landscapes are evolving rapidly, and so are we. This upgrade builds on what customers already rely on, introducing powerful new capabilities that make it easier…
September 12, 2025
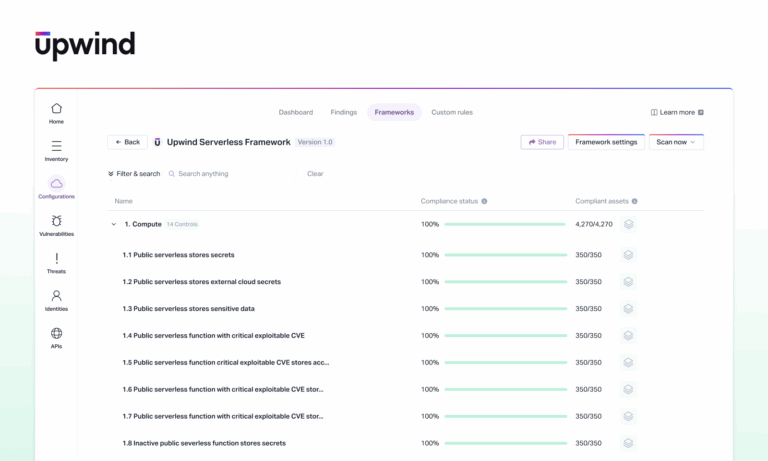
A New Standard for Serverless Security: The Upwind Serverless Framework
Today, we’re introducing the Upwind Serverless Framework, a new runtime-first compliance framework purpose-built for serverless environments. Upwind has long provided runtime visibility into serverless workloads; this framework builds on that foundation by aligning real-time behavior with compliance controls, making it easier to detect misconfigurations, enforce least privilege, and surface risks that matter. It helps security…
MURKY PANDA and the Blind Spot in Modern Cloud Security
August 21, 2025 - CrowdStrike disclosed ongoing activity by MURKY PANDA, a state-aligned Chinese espionage group purpose-built for the cloud. Unlike many threat actors who adapt legacy tactics, MURKY PANDA designs operations around cloud-native infrastructure from the ground up. Their latest campaign combines a Linux malware strain, a Commvault zero-day exploit, and identity abuse in Microsoft…
Accelerate Vulnerability Investigations with Visual Contextualized Queries
Modern cloud environments generate a constant stream of vulnerability information across thousands of assets, frameworks, and packages. While filters are essential to navigate this data, they can quickly become overwhelming as environments grow. Upwind’s new Investigate tab introduces a more efficient and guided way to explore vulnerabilities. Instead of relying on long lists of filters,…
Introducing Security Risks: A Unified Model for Understanding Cloud Risks
Cloud security teams face an overwhelming amount of data. Misconfigurations, vulnerabilities, identity risks, and exposures often live in separate tools and dashboards, making it difficult to see how they connect. The real challenge is understanding how these signals intersect to create true risk. That's why we are excited to introduce Upwind Security Risks - a unified…
Upwind Strengthens Cloud Identity Security with New Microsoft Entra ID Detection Coverage
We are thrilled to announce that Upwind has expanded its Microsoft Entra ID (formerly Azure Active Directory) detection coverage to provide deeper visibility into identity changes, privilege escalation, and credential misuse across Azure environments. These new detections help security teams identify and respond to identity-driven threats faster, before they can compromise the tenant or persist…
Upwind Enables Smarter, More Efficient, Security with Sensor Improvements
We are excited to share the latest improvements to our eBPF-powered sensor, the foundation of our runtime security platform. By continuously enhancing how the sensor observes and protects Kubernetes environments, we’re making security both more effective and more efficient for our customers. As part of this advancement, we are introducing container image scan jobs, a…
Upwind Expands Threat Detection with Native Azure Log Analytics Integration
Upwind is excited to announce a new integration that brings deeper visibility and faster threat detection to Microsoft Azure environments. With native support for Azure Log Analytics and Activity Logs, customers can now detect risks and respond to threats across Azure with greater precision, especially around administrative activity, access patterns, and configuration changes. This release…
Upwind Modernizes PCI-DSS for Cloud-Native Security
We’re introducing the Upwind Framework for PCI-DSS to help organizations meet one of the most widely adopted security standards. This release is part of Upwind’s broader mission to make compliance continuous and directly tied to runtime environments. In this blog, we will explain what PCI-DSS is and why it matters, highlight the growing challenges of…
Streamline Compliance & Auditing with Upwind’s Configurations Dashboard
If you’re responsible for cloud security and compliance, you know the drill. Misconfigurations pile up across environments, frameworks keep updating, and leadership wants to see progress - all while your team is already stretched thin. The stakes are high. A single overlooked configuration can lead to major gaps in compliance, or worse, leave sensitive data…
Harbor Shift Left: Bringing Runtime Intelligence to Container Security
Picture this: your development team is racing to deploy a critical update, but security scanning brings everything to a halt. The scanner reports 47 vulnerabilities, but which ones actually matter? Which are exploitable in production? And most importantly, should you block the deployment or proceed? This is the daily reality for most DevOps teams. Traditional…
Upwind Now Supports CloudTrail Log Aggregation for More Accurate Detections
A security team at a large financial services company once spotted a troubling pattern: a low-privilege IAM role listed IAM users, created an inline policy, and then assumed a higher-privilege role. Each action looked routine on its own and slipped past their detection system, which analyzed events in isolation. Only later, during a manual review,…
Introducing Upwind’s New Threat Dashboard: Simplifying Complexity to Drive Action
Today, we’re excited to announce the release of the enhanced Upwind Threat Dashboard, part of our ongoing commitment to continuously improving how we help security teams protect their environments. Threat landscapes are evolving rapidly, and so are we. This upgrade builds on what customers already rely on, introducing powerful new capabilities that make it easier…
A New Standard for Serverless Security: The Upwind Serverless Framework
Today, we’re introducing the Upwind Serverless Framework, a new runtime-first compliance framework purpose-built for serverless environments. Upwind has long provided runtime visibility into serverless workloads; this framework builds on that foundation by aligning real-time behavior with compliance controls, making it easier to detect misconfigurations, enforce least privilege, and surface risks that matter. It helps security…
MURKY PANDA and the Blind Spot in Modern Cloud Security
August 21, 2025 - CrowdStrike disclosed ongoing activity by MURKY PANDA, a state-aligned Chinese espionage group purpose-built for the cloud. Unlike many threat actors who adapt legacy tactics, MURKY PANDA designs operations around cloud-native infrastructure from the ground up. Their latest campaign combines a Linux malware strain, a Commvault zero-day exploit, and identity abuse in Microsoft…