Updated on November 11, 2026
It’s a challenge to stay on top of the proliferation of cloud security standards and frameworks today. In this article, we’ll cover the crucial foundations of cloud security standards, like what they are, how they differ, and what benefits and drawbacks you’ll encounter when adopting any framework. We’ll also dig deeper into the challenges that emerge beyond the basics. What are the top frameworks’ overlaps and gaps? Should they be combined? And how do the frameworks apply to modern architectures?
What are Cloud Security Standards and Frameworks: The Basics
Cloud security standards and frameworks provide structured guidelines and best practices to secure cloud environments, data, workloads, and configurations. The goal of frameworks is to standardize practices, build trust, reduce risk, and achieve compliance.
Frameworks can be grouped by their primary focus and origin:
1. Government and National Standards
- National Institute of Standards and Technology (NIST) Frameworks
- Cybersecurity Framework (CSF): U.S. federal guidelines for security and risk management.
- Special Publication (SP) 800-53: Comprehensive security and privacy controls.
- Special Publication (SP) 800-144: Security for public cloud environments.
2. Industry Standards and Compliance
- Payment Card Industry Data Security Standard (PCI DSS): Security requirements for organizations handling payment card data.
- Service Organization Control 2 (SOC 2): Standards for data privacy and security in service organizations.
- Control Objectives for Information and Related Technologies (COBIT): IT governance framework widely used across industries.
3. Technical and Hardening Guidelines
- Center for Internet Security (CIS) Benchmarks: Detailed technical controls for cloud providers and systems.
- Cloud Security Alliance (CSA) Cloud Control Matrix (CCM): Security controls tailored to cloud environments.
4. Privacy-Focused Frameworks and Regulations
- International Organization for Standardization (ISO) 27018: Guidelines for cloud data privacy.
- General Data Protection Regulation (GDPR): European Union regulation for data privacy.
- California Consumer Privacy Act (CCPA): California regulation for consumer data privacy.
5. Broad Organizational and Risk Management Frameworks
- International Organization for Standardization (ISO) 27001: Framework for information security management systems.
- National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF): Enterprise-wide risk management and resilience.
6. Cloud-Specific Frameworks
- CSA CCM (also listed above): A control set that covers both cloud providers and their customers.
- International Organization for Standardization (ISO) 27017: Cloud-specific security guidelines.
There are also frameworks that don’t prescribe controls, like MITRE ATT&CK, which details ways attackers operate so organizations can build defensive strategies against them.
All frameworks outline what needs to be done, but they often lack practical guidance for implementing and maintaining security in dynamic, complex cloud environments.
Turning Frameworks Into a Cloud Security Policy Framework
A cloud security policy framework is the set of internal policies, standards, and procedures that turns external frameworks and guidance into enforceable rules for how an organization uses cloud services. It is the layer where “what” becomes “how.”
Core Policy Domains
- IAM and least privilege
- Data classification and encryption
- Logging and monitoring
- Vulnerability and patch management
- Network segmentation
- Incident response
- Backup and recovery
- Third-party/SaaS use
Mapping Policy Statements to Framework Controls
Start with a policy statement that sets out the requirement in business terms. Next, translate it into a control objective, which is the security outcome you need. Then map that objective to the relevant controls in each framework you follow:
- NIST: Map to specific controls, such as AC-6 for least privilege, SC-28 for protecting information at rest, and SI-7 for integrity. Supporting guidance includes NIST SP 800-34 for backup and recovery planning, NIST SP 800-111 for stored-data encryption, and NIST SP 800-52 Rev. 2 for TLS configuration.
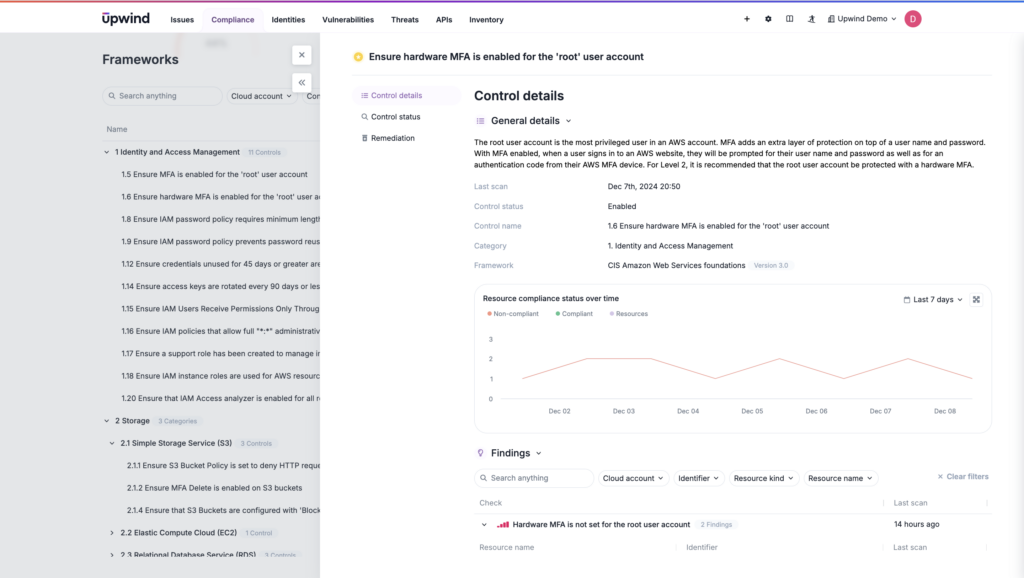
- CIS: Map to specific benchmark recommendations, such as CIS AWS Foundations Benchmark checks that restrict administrative IAM privileges and retain API and control plane logs, or CIS Kubernetes Benchmark checks for container hardening.
- ISO: Map internal policy statements to the applicable ISO requirement. Then verify enforcement continuously as the environment changes.
- CSA: Map to CSA CCM domains and control objectives, especially for IAM, cryptography, and virtualization and security operations.
From there, define the standard or procedure that shows how the requirement is applied. Then collect evidence that the control is operating, ready for audit.
A Simple Example Structure
Each policy area can follow the same five layers: policy (the high-level rule), standard (a measurable requirement), procedure (the step-by-step process), technical control (the tool or configuration that enforces it), and evidence for audit (records showing it is implemented and working).
- Policy: “Access to cloud resources must follow least privilege.” (Maps to identity and access management controls, including NIST AC-6.)
- Standard: Role-based access must be approved and reviewed.
- Procedure: Managers request access, security approves it, and access is reviewed periodically.
- Technical control: MFA, RBAC, conditional access, and periodic access reviews.
- Evidence for audit: Access review reports, approval tickets, and system logs.
The same structure works for data protection. A policy that “cloud data must be classified and encrypted” maps to data protection and cryptographic controls such as NIST SC-28 and NIST SP 800-111. Its standard requires sensitive data to be encrypted at rest and in transit, and its procedure classifies data before upload and applies approved encryption methods. The technical controls are encryption settings, key management, and TLS. Evidence comes from configuration screenshots, encryption reports, and key policy records.
Runtime and Container Scanning with Upwind
Upwind offers runtime-powered container scanning features so you get real-time threat detection, contextualized analysis, remediation, and root cause analysis that’s 10X faster than traditional methods.
Get a DemoBenefits and Challenges of Cloud Security Standards
Cloud security frameworks like CIS, NIST, and PCI DSS provide a solid foundation for organizations working to secure their environments and achieve compliance. They’re packed with detailed recommendations, checklists, and controls — but they’re far from plug-and-play solutions.
Though almost all organizations operate in the cloud, and many use cloud security frameworks, a large share acknowledge “significant” security gaps in their cloud infrastructures.
Frameworks set expectations but don’t do the heavy lifting. Organizations must tailor these guidelines to their specific cloud architectures, reckoning with multi-cloud security or the needs of hybrid-cloud architectures. They must also reconcile gaps between theory and practice and address challenges that frameworks alone can’t solve. Here are the core benefits that any framework provides, along with what organizations need to know to close the gaps.
Frameworks Give Organizations a Roadmap
Frameworks provide a structured roadmap for securing cloud-native architectures like Kubernetes, serverless, and containerized workloads.
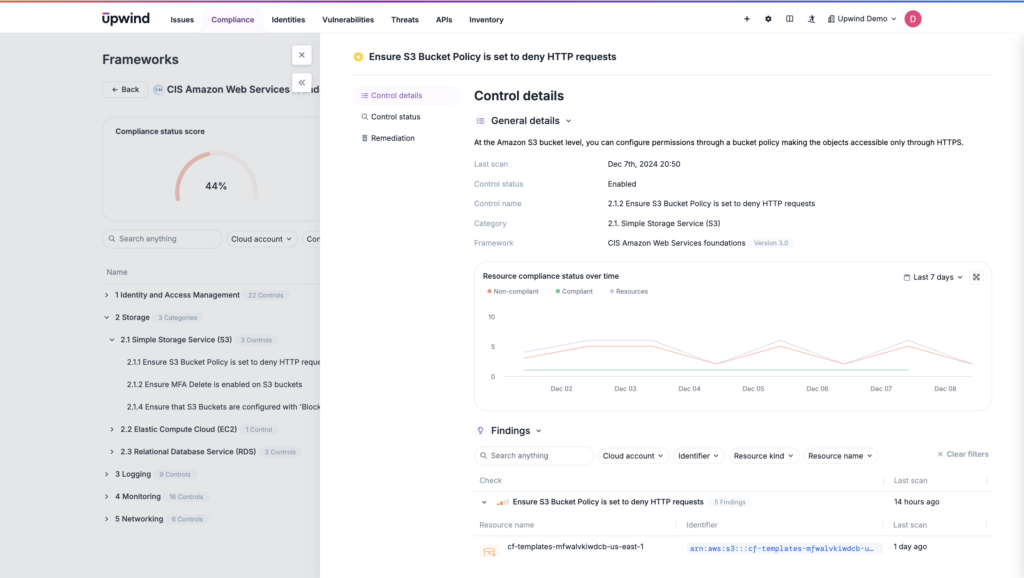
Frameworks define the "what" but leave the "how" to organizations. Companies must operationalize these frameworks on their own, often starting with static guidelines and checklists. To succeed, they’ll need to treat identity as the new perimeter, implement automation for security checks, enforce policies consistently, and monitor for risks in real time. This requires significant investment in tools and expertise to bridge the gap between theory and practical application.
Frameworks Call for Static Audits in an Environment of Dynamic Change
Frameworks offer audit-ready standards that help organizations demonstrate compliance.
Frameworks assume periodic, static audits, but today’s cloud environments are highly dynamic, with workloads and configurations constantly shifting. Organizations must implement continuous compliance monitoring and real-time risk assessments to keep pace with their workloads. Without these proactive measures, frameworks like CIS Benchmarks or NIST SP 800-53 risk becoming outdated snapshots that can’t reflect the current security posture.
Frameworks Often Compartmentalize Security, While Companies Need a Unified Approach
Frameworks address specific areas of security — such as data protection, workload security, or configuration hardening — which can guide focused efforts.
Security frameworks tend to work in silos, while companies operate in interconnected multi-cloud environments that require unified visibility. To fill this gap, organizations must integrate tools that provide holistic insights, ensuring they can simultaneously identify misconfigurations, vulnerabilities, and runtime threats across all their cloud assets.
Frameworks Set a Baseline, Not a Goal
Frameworks establish minimum standards for security, giving organizations a foundation to build on.
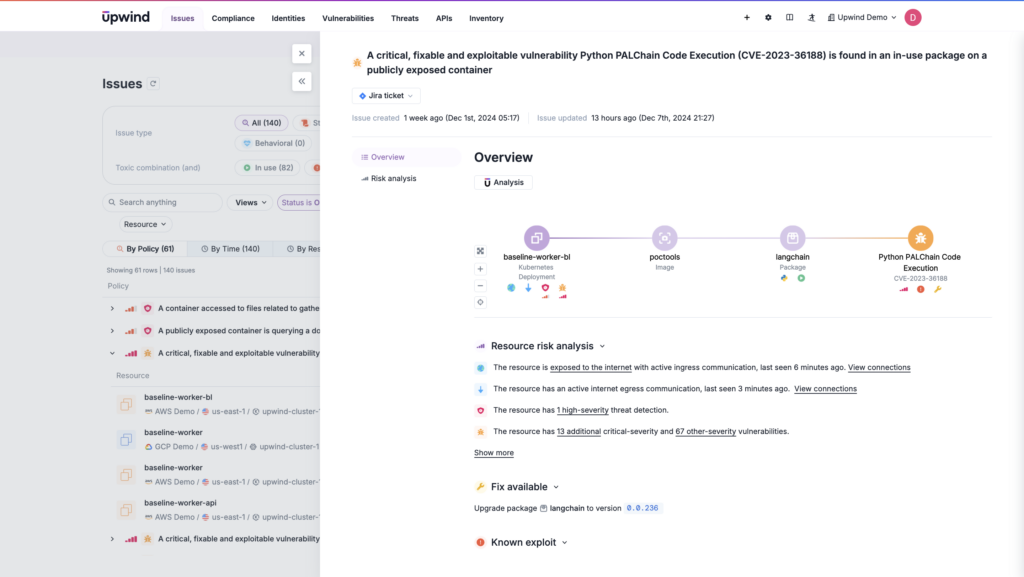
While frameworks ensure baseline protections, they often fail to address sophisticated, emerging threats. Supply chain attacks and runtime anomalies are part of that picture. So are AI-powered phishing campaigns that can run autonomously and real-time voice and video deepfakes used to impersonate trusted people. To move beyond compliance and achieve true security resilience, companies need proactive measures. Those include advanced threat detection, AI-driven anomaly detection, runtime monitoring, and zero-trust identity verification, such as multi-device sign-off, for sensitive actions.
Frameworks are Individual, Companies Must Combine Them
Each framework focuses on a specific regulatory or operational area, helping organizations meet their own distinct compliance needs.
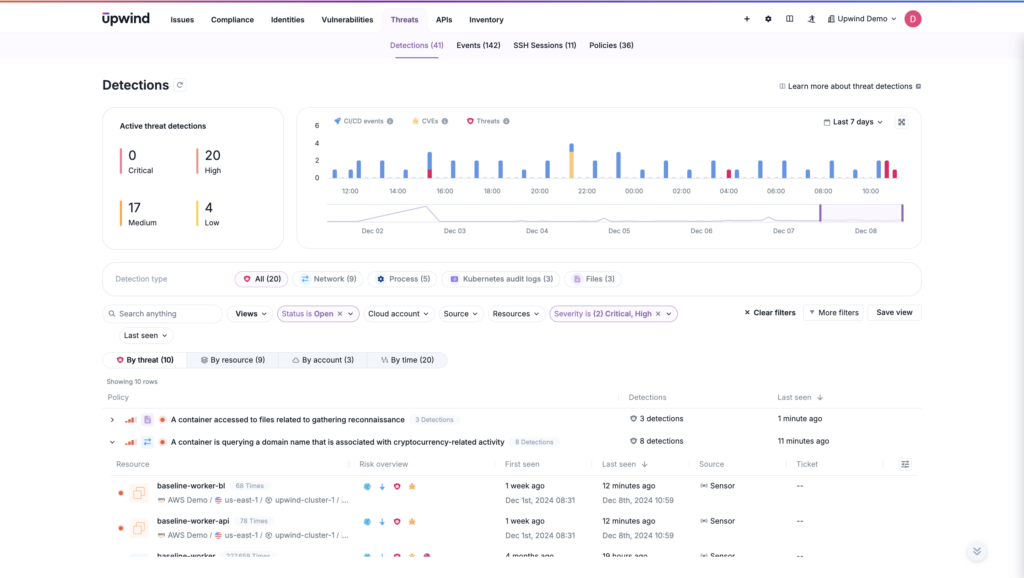
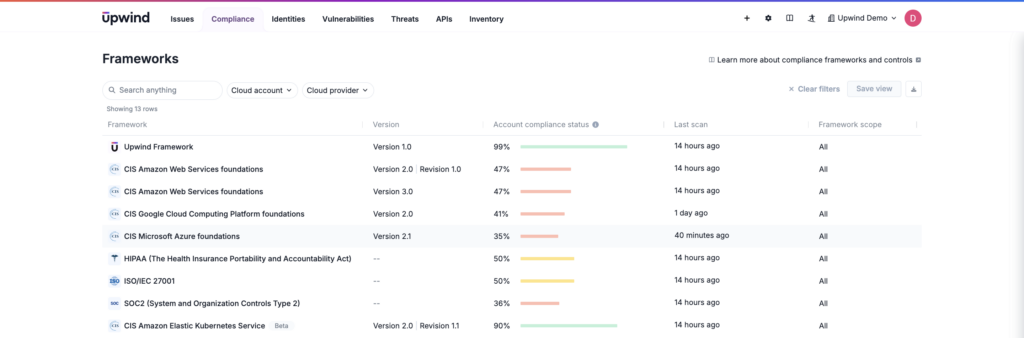
In reality, businesses often need to follow multiple frameworks simultaneously (e.g., CIS Benchmarks, NIST, and PCI DSS), which can result in overlapping or conflicting requirements. Companies must harmonize controls across frameworks, often by leveraging automation tools, to reduce operational overhead and demonstrate comprehensive compliance without duplicating their work.
Comparing Top Cloud Security Frameworks
Cloud security frameworks each serve a purpose, offering guidance on different aspects of security, compliance, and risk management. However, no single framework covers every need, so those looking to compare them should understand the individual strengths and limitations of each.
Let’s focus on 4 common cloud security frameworks:
- CIS Benchmarks are highly actionable, providing prescriptive hardening guidelines specific to major cloud providers like AWS, Azure, and GCP. They are the go-to framework for technical configuration and operational security in cloud-native environments.
- NIST SP 800-53 is one of the most comprehensive frameworks available, covering technical, procedural, and governance controls for federal systems and enterprises. It’s widely adopted across industries for risk management and compliance.
- ISO 27001 is a globally recognized standard for information security management systems, and ISO 27017 adds cloud-specific controls.
- The CSA CCM is purpose-built for cloud environments, focusing on shared responsibility between cloud providers and customers, filling gaps in traditional frameworks by emphasizing SaaS and cloud-native security.
| Framework | Purpose | Strengths | Challenges | Best For |
| CIS Benchmarks | Hardening cloud setups | Actionable, cloud-specific controls | Needs frequent updates | Cloud-native teams |
| NIST SP 800-53 | Comprehensive controls | Broad, highly detailed | Overwhelming for some setups | Enterprises with diverse needs |
| ISO 27001/27017 | Info security management | Globally recognized certification | Resource-intensive process | International operations |
| CSA CCM | Cloud-specific guidance | Strong on shared responsibility | Less prescriptive than CIS Benchmarks for configuration, but highly technical for mapping responsibilities | SaaS providers and multi-cloud users |
Strengths and Weaknesses Explained
CIS Benchmarks provide actionable guidelines tailored for specific cloud providers, making them practical for cloud-native teams. They address critical security configurations quickly. However, framework updates are frequent, to align with cloud provider changes, requiring teams to stay current. CIS also focuses narrowly on configuration hardening, leaving gaps in broader governance.
NIST SP 800-53 offers a comprehensive set of controls for technical, procedural, and governance aspects, making it versatile for large, complex infrastructures. Yet the vast number of controls can be overwhelming, especially for organizations with fewer resources. Tailoring the framework to specific use cases can help, but it is time-consuming.
ISO 27001 and its cloud extension, ISO 27017, are built around certification. Achieving certification requires demonstrating high-level security practices. But the certification process is lengthy, resource-intensive, and ongoing, which can be a challenge for smaller organizations or those with limited budgets.
CSA CCM is designed specifically for cloud environments and excels at clarifying shared responsibilities between providers and consumers. It’s especially useful for SaaS providers. While excellent for responsibility allocation, it lacks the granular technical depth of frameworks like CIS, requiring additional tools for detailed implementation.
Overlaps and Gaps
These four frameworks each serve distinct roles in cloud security. Yet they share some commonalities while leaving critical gaps.
CIS Benchmarks and CSA CCM focus heavily on cloud-native environments, providing actionable guidance for cloud configuration (CIS) and clarifying shared responsibilities between cloud providers and customers (CSA CCM).
However, both lack the broader governance structure and enterprise-level depth of NIST SP 800-53 and ISO 27001/27017, which address organizational policies, risk management, and global regulatory needs. NIST SP 800-53 and ISO 27001/27017 overlap in their emphasis on comprehensive security controls, but NIST was created by a U.S. government agency (though with wide adoption abroad) and is highly detailed, whereas ISO offers globally recognized standards with a focus on certification.
The differences between frameworks are useful for organizations looking for their own ideal framework. For example, CIS Benchmarks provide specific technical controls for hardening cloud environments, but they don’t address organizational policies or certification needs like ISO does. Similarly, while CSA CCM excels at detailing the shared responsibility model, it is less prescriptive than CIS or NIST in defining technical configurations.
Considering multiple frameworks? Together, these frameworks can provide a layered approach: CIS and CSA CCM for practical cloud security, NIST SP 800-53 for comprehensive control mapping, and ISO 27001/27017 for governance and international compliance. The gaps highlight the importance of combining frameworks to achieve both technical and organizational security goals. Regulation adds pressure, too: the EU AI Act, whose obligations are now applying in phases and a growing number of strict U.S. state privacy laws, such as those in Colorado and Delaware, raise the risk of cross-region compliance gaps and misconfigurations. Many organizations will also need a unified data governance framework that tags data with its required residency, so copies don’t end up in the wrong region.
Approach to Cloud Architecture
The selected frameworks approach modern cloud architectures with varying degrees of alignment and specificity.
CIS Benchmarks are the most directly applicable to modern cloud-native environments like Kubernetes, containers, and serverless architectures, offering provider-specific hardening guidelines for these dynamic setups.
NIST SP 800-53, while comprehensive, was originally designed for traditional IT infrastructures and must be tailored for ephemeral workloads and continuous deployment models common in modern architectures.
ISO 27001/27017 provides overarching governance and compliance structures. ISO 27017 has cloud-specific controls that could support modern architectures if paired with more technical frameworks like CIS.
In contrast, CSA CCM is purpose-built for the cloud, offering a clear shared responsibility model that helps organizations secure their use of Platform as a Service (PaaS), Infrastructure as a Service (IaaS), and Software as a Service (SaaS).
Together, the frameworks reveal the need to blend technical, operational, and governance strategies to address the complexities of modern cloud architectures effectively, but that can be difficult to balance while relying on a single framework.
Upwind Helps Operationalize Cloud Security Frameworks
No matter what organizational needs arise or which frameworks teams use, Upwind can help. Frameworks provide essential guidance, but operationalizing them in modern cloud environments requires real-time visibility and actionable insights. It facilitates alignment with benchmarks like CIS and NIST SP 800-53, and continuously monitors for risks in dynamic cloud-native environments such as Kubernetes and serverless architectures.
Want to see how you can simplify compliance and operationalize controls across frameworks and clouds? Get a demo.
FAQ
What is the difference between NIST and CSA?
NIST emerged from a U.S. government agency providing comprehensive frameworks for managing cybersecurity across industries, not just cloud environments. It focuses on governance, risk management, and security controls. It’s aimed at government organizations, contractors, and large enterprises with diverse architectures, and it is broader than CSA, covering governance and risk management beyond the cloud.
CSA emerged from a nonprofit organization specializing in cloud-specific security. Frameworks like its Cloud Control Matrix (CCM) are explicitly designed to address the shared responsibility model between cloud providers and customers. It’s ideal for organizations with cloud-native ecosystems, and it is more concise than NIST.
How do you implement a cloud security framework in an organization?
Implementing a cloud security framework doesn’t differ much from the implementation process for other business tools. Teams will want to engage stakeholders and users, build a case for a particular framework, ease the adoption process, and ensure they’re getting the use and outcomes they envisioned. Here are the steps:
- Assess Current Environment: Conduct a gap analysis and inventory assets.
- Choose Framework(s): Select frameworks like CIS, NIST, ISO, or CSA based on goals.
- Tailor Policies: Customize guidelines to fit your architecture and priorities, and use your provider’s shared responsibility documentation to map each security control to either the provider or your own team.
- Automate Controls: Use tools like CSPM, CNAPPs, and CI/CD integrations.
- Monitor Continuously: Implement real-time monitoring and regular audits.
- Train Teams: Ensure stakeholders understand framework requirements.
- Evolve Regularly: Update for new threats, changes in infrastructure, and framework revisions.
What is cloud security management?
In the context of cloud security frameworks, cloud security management involves the practical implementation and operationalization of framework controls across an organization’s cloud environments.
While frameworks like CIS, NIST, and CSA provide the guidelines for securing cloud systems, cloud security management focuses on applying, monitoring, and maintaining those controls to address real-world risks and threats. And while framework-driven management is one part of overall cloud security management, general security operations necessarily expand beyond that focus.
What is a cloud security framework, and which ones are worth using for my organization?
A cloud security framework is a structured set of best practices, policies, procedures, technologies, and controls used to protect cloud environments and sensitive data. It organizes controls around areas like identity, configuration, monitoring, incident response, encryption, access management, governance, and compliance. The NIST Cybersecurity Framework and the CIS Critical Security Controls are practical starting points. They offer a proven set of best practices and make compliance audits for standards like ISO, HIPAA, and PCI DSS easier.
How do cloud security frameworks differ from cloud compliance frameworks like SOC 2, PCI DSS, and HIPAA?
Cloud security frameworks, like CIS Benchmarks, CSA CCM, and NIST CSF, are operational best-practice guides that tell you how to secure the cloud. Compliance frameworks like SOC 2, PCI DSS, and HIPAA are externally driven requirements that you must prove you meet to auditors, customers, or regulators. Some are mandatory depending on the data you handle: PCI DSS for cardholder data and HIPAA for medical information. SOC 2 is generally voluntary but often expected in B2B SaaS.
What controls does the CSA Cloud Controls Matrix include?
The CSA Cloud Controls Matrix (CCM) is made up of 207 controls across 17 security domains. These cover areas such as Application & Interface Security, Data Centre Security, Identity & Access Management, Threat and Vulnerability Management, and Universal Endpoint Management. It maps to other standards, regulations, and control frameworks, and it comes with vendor assessment questions such as the CAIQ, auditing guidance, and metrics. CSA is also building machine-readable controls, implementation guidance, and controls as code to support automated, continuous compliance.
How does NIST apply to cloud security in practice?
In practice, NIST works as a risk-based framework. Organizations categorize cloud information and services, then select and tailor baseline controls for their environment. They implement and assess those controls, authorize the system once risk is acceptable, and continuously monitor for changes, weaknesses, and vulnerabilities. Cloud providers use it to strengthen baseline controls and standardize risk management, while consumers use it to evaluate providers, verify service agreements, and add compensating controls. NIST should be integrated early in the system development life cycle, not referenced after the fact.
What are the most common cybersecurity frameworks used in cloud environments?
The most common frameworks in cloud environments are the NIST Cybersecurity Framework, CIS, MITRE ATT&CK, and the CSA Cloud Controls Matrix. Cloud security frameworks also often align with broader standards and compliance requirements such as SOC 2, ISO 27001, GDPR, and HIPAA.