
Using Upwind’s Non-Human Identity Security, you can easily monitor and secure AWS execution roles and ensure best practices for non-human identities (NHIs).
Execution roles are important for granting permissions to AWS EC2 instances and AWS Lambda functions. However, it can be difficult to enforce best practices that allow only known resources to assume and use permissions within the role. Upwind’s Identity Security simplifies this process, providing full visibility and monitoring for all the execution roles in your AWS environment.
What is an Execution Role?
In an AWS cloud environment, an execution role grants permissions to AWS EC2 instances and AWS Lambda functions, to perform actions on behalf of a user or another service. Execution role permissions are IAM permissions that allow EC2 instance or Lambda function permissions to access specific services and resources, and they cannot access any services or resources that are not specified in the permissions. An execution role consists of permissions defined by IAM policies and a trust policy specifying which entity is allowed to assume the role, allowing services to securely access resources without needing permanent credentials.
It’s important to note that Lambda functions and EC2 instances do not have permissions by default, and they rely entirely on the permissions that are granted to them by the execution role. This is designed to follow the Principle of Least Privilege, which grants only the necessary permissions required for a function to perform needed tasks.
How do you secure Execution Roles?
In order to ensure security for your Lambda functions and EC2 instances, you must carefully monitor execution roles and their associated permissions. By controlling the execution role’s permissions and ensuring that it adheres to best practices, you can also ensure your non-human identity security.
Upwind empowers you to do this by providing you with:
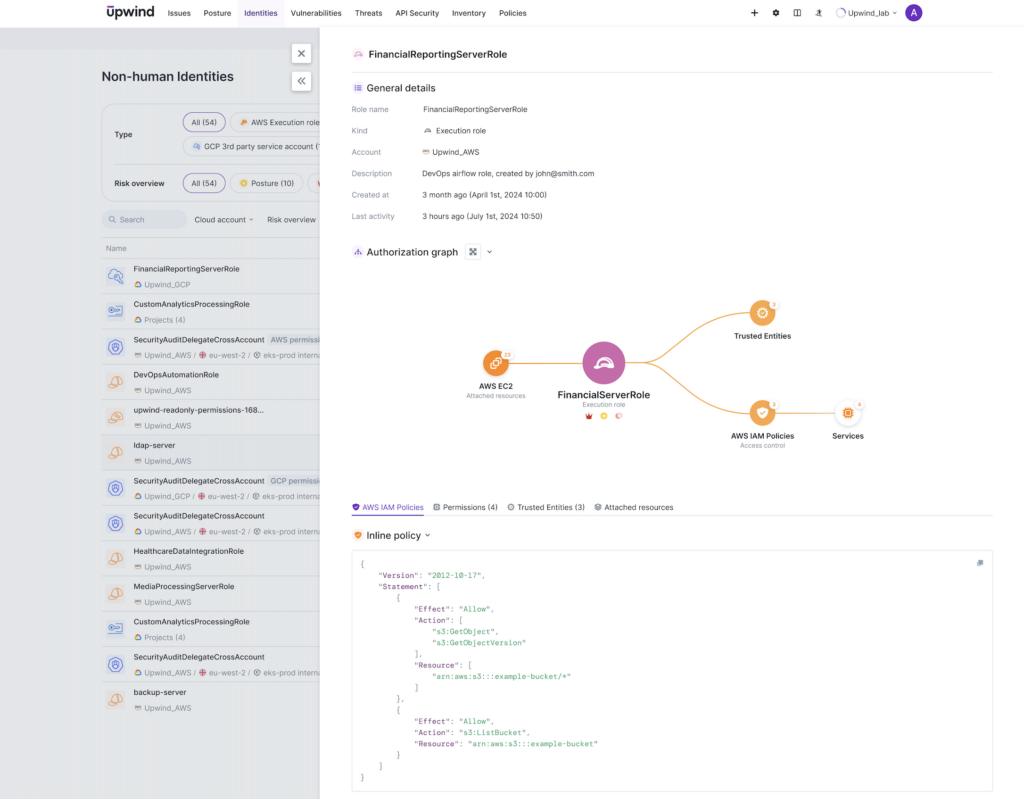
- Execution Role Details: Discover the name of the role, the associated account, and when it was created.
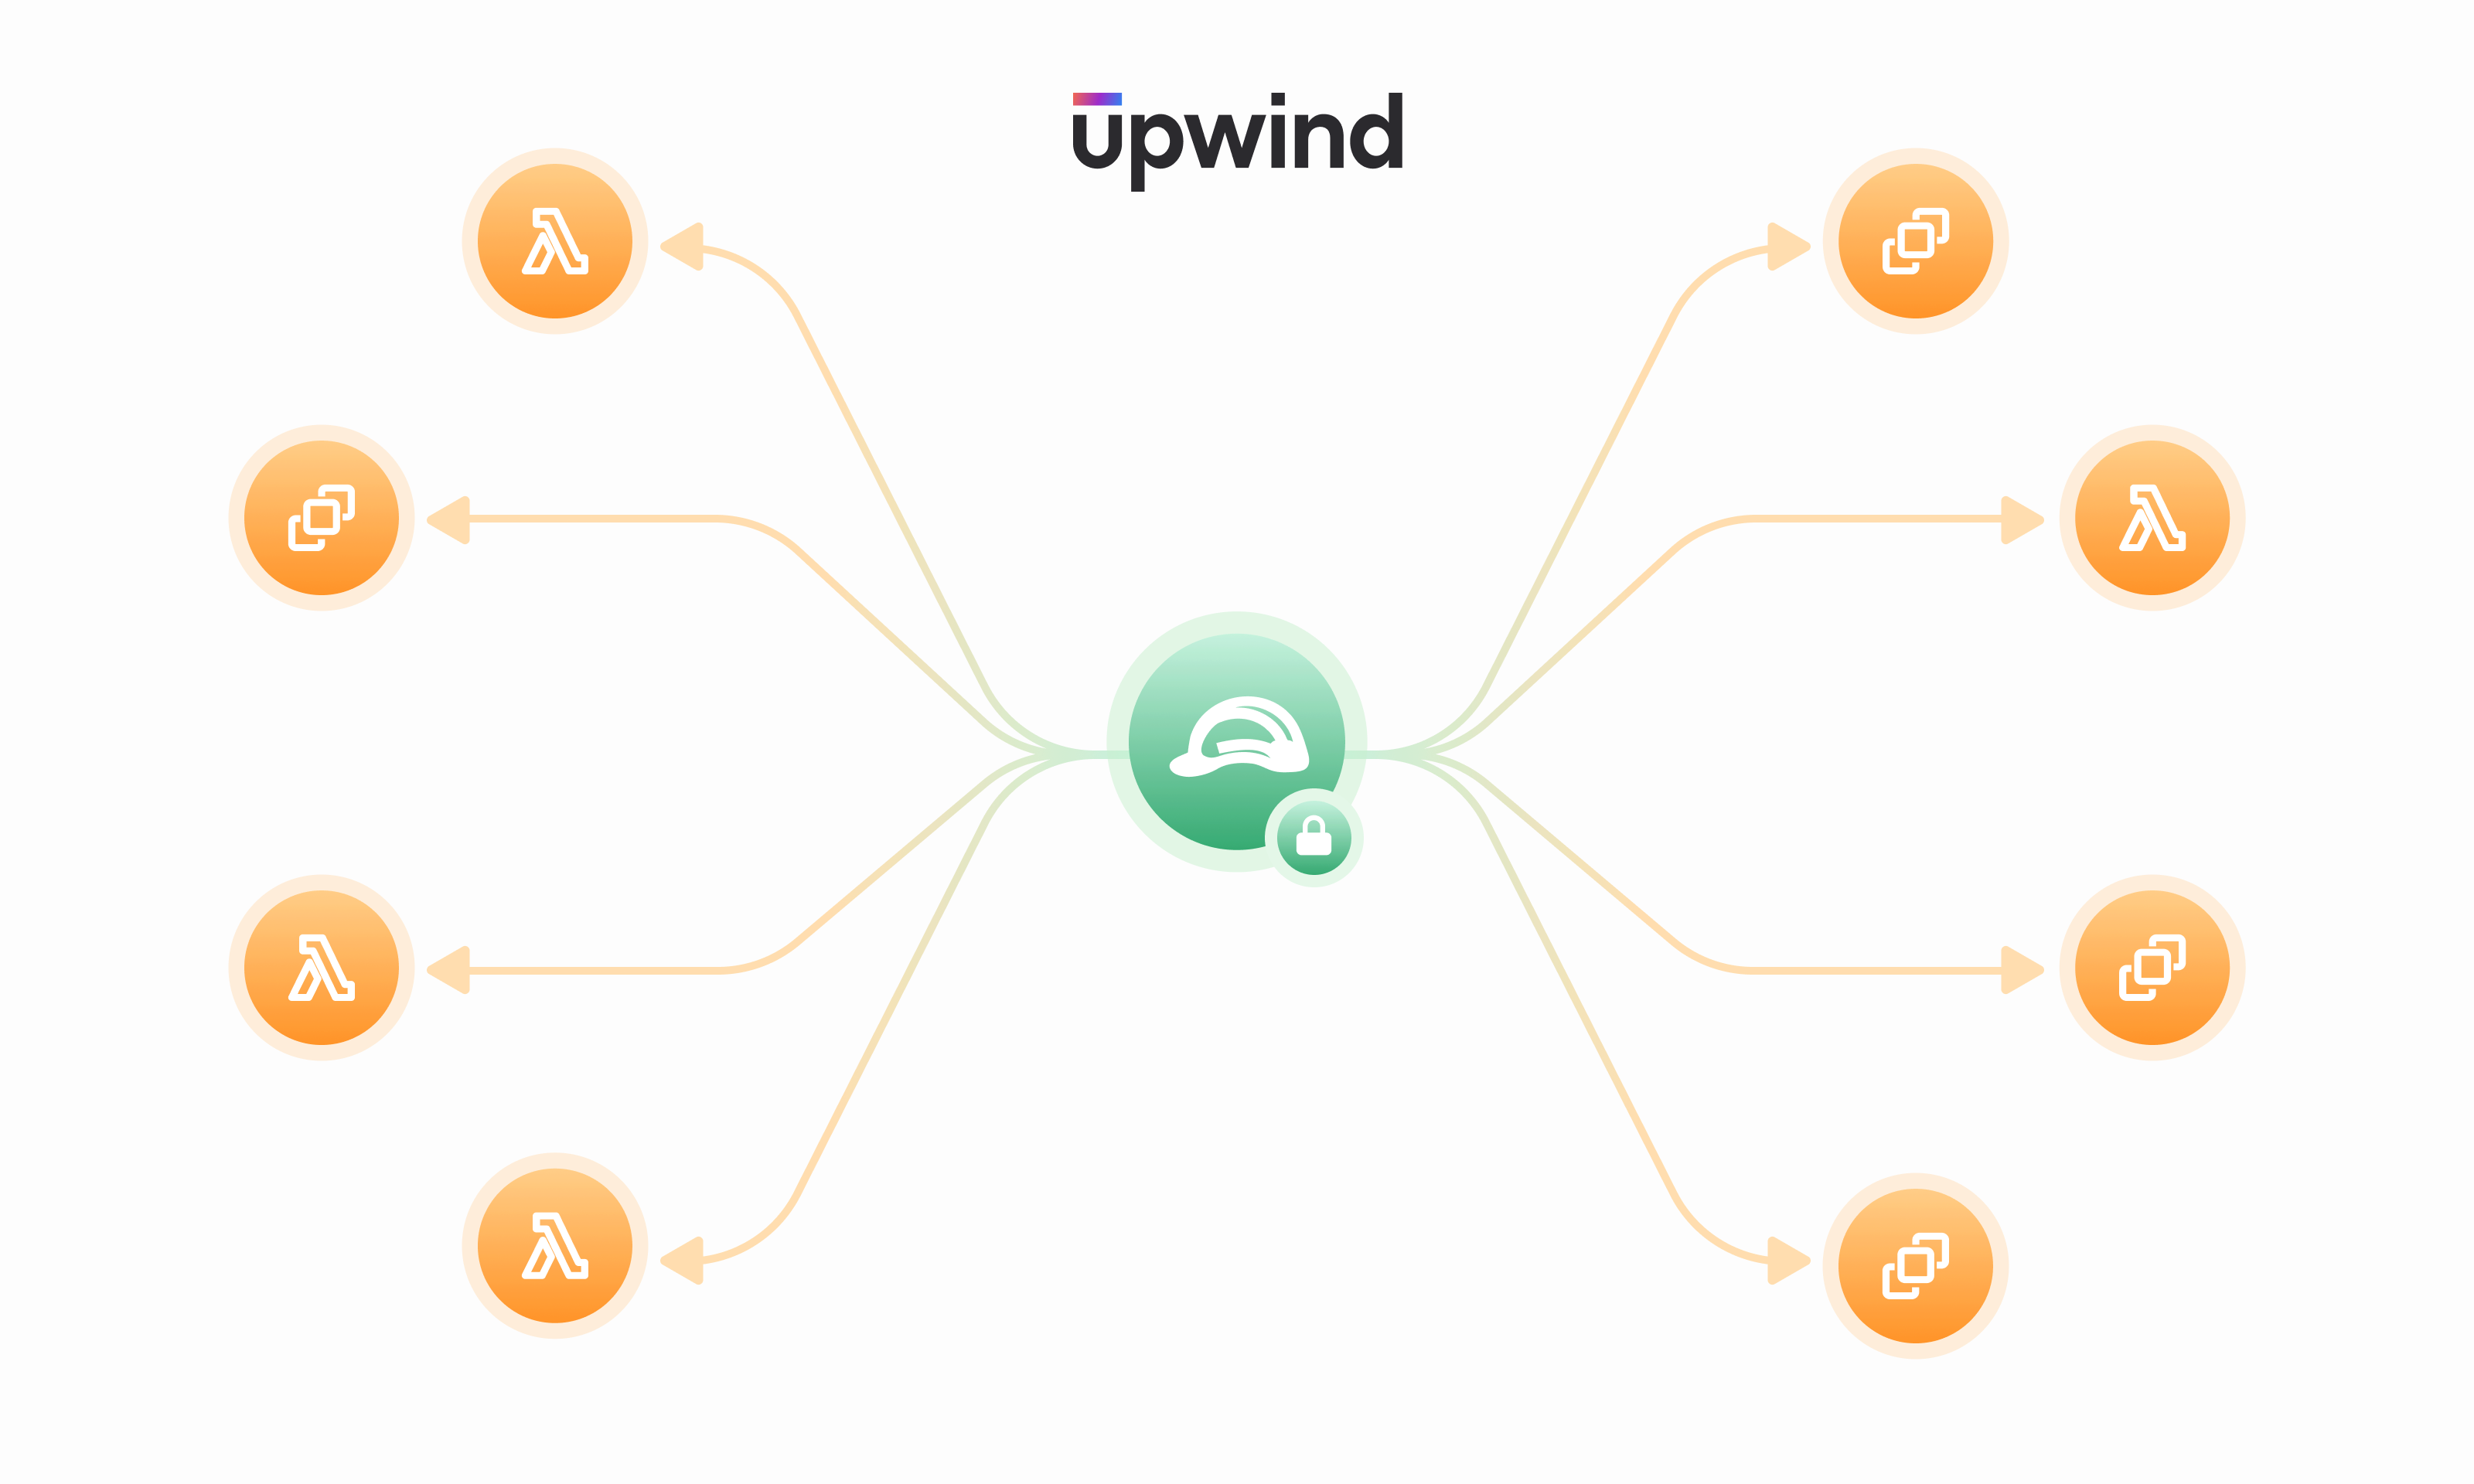
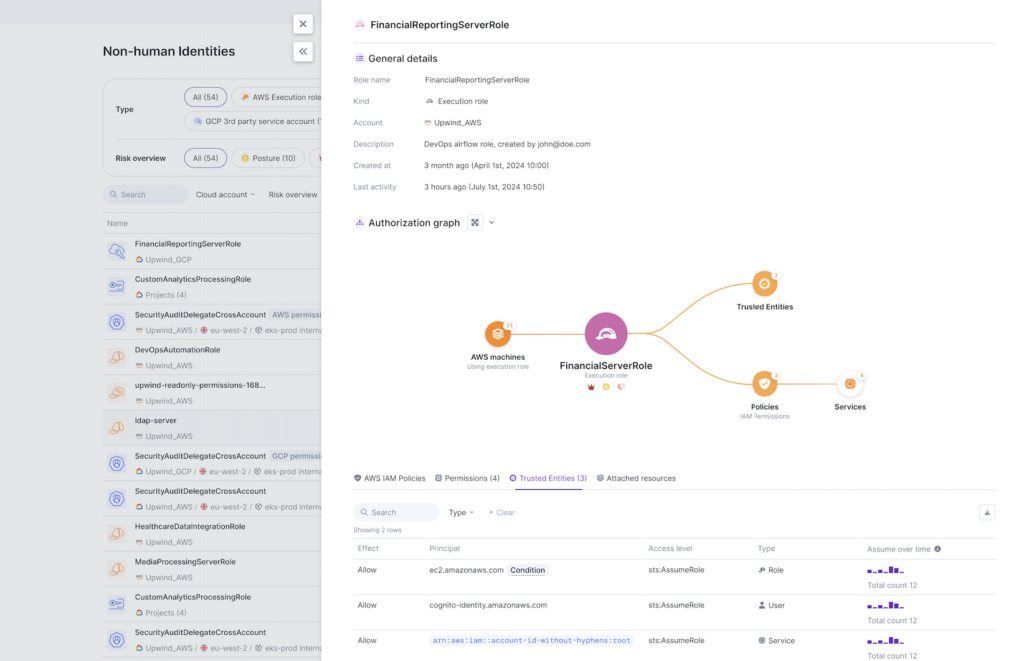
- An Authorization Graph: Visually understand who can assume a role and what permissions they have on which resources.
- A list of Trusted Entities: Including the entities that are allowed to assume a particular IAM role
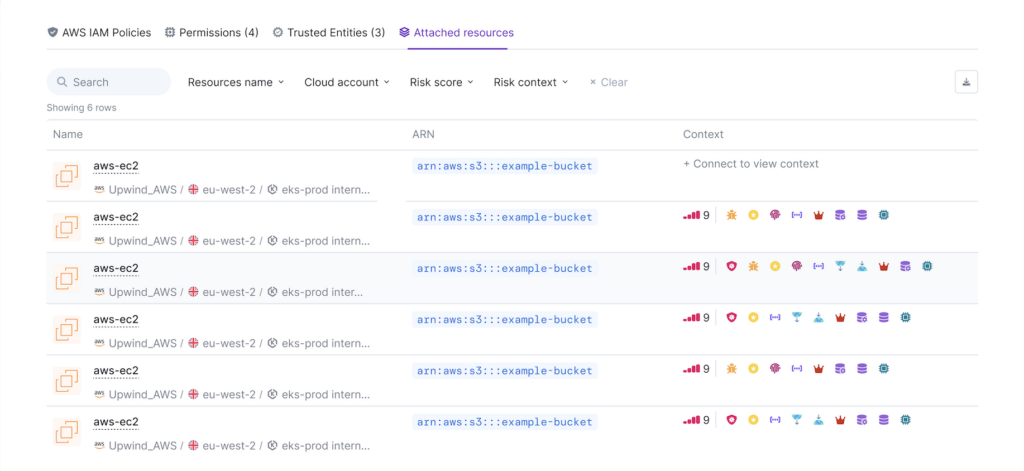
- A Resources overview: View all resources currently assuming a given role
- Highly Privileged Permissions: Automatic identification if a cross-account role’s permissions include highly privileged permissions.
Use Upwind’s Non-Human Identity Security to monitor, track and manage your execution roles and easily understand which resources are currently assuming the role, who can assume a role, and what role permissions they have on EC2 instances and Lambda functions.
To learn more about Upwind’s Non-Human Identity Security, visit the Upwind Documentation Center (login required) or schedule a demo.